Indian certification authority eMudhra’s private keys compromised – one of them was the number ‘4’
Massive clean-up job under way because this mess makes it possible to impersonate any website or service
A critical security incident has been uncovered involving Indian certification authority eMudhra, who has issued over 60 million digital certificates. According to a post from Mozilla's cryptography engineering team, private keys associated with eight of eMudhra's intermediate certificates were compromised on October 17, leaving the validity of the issued certificates in question.
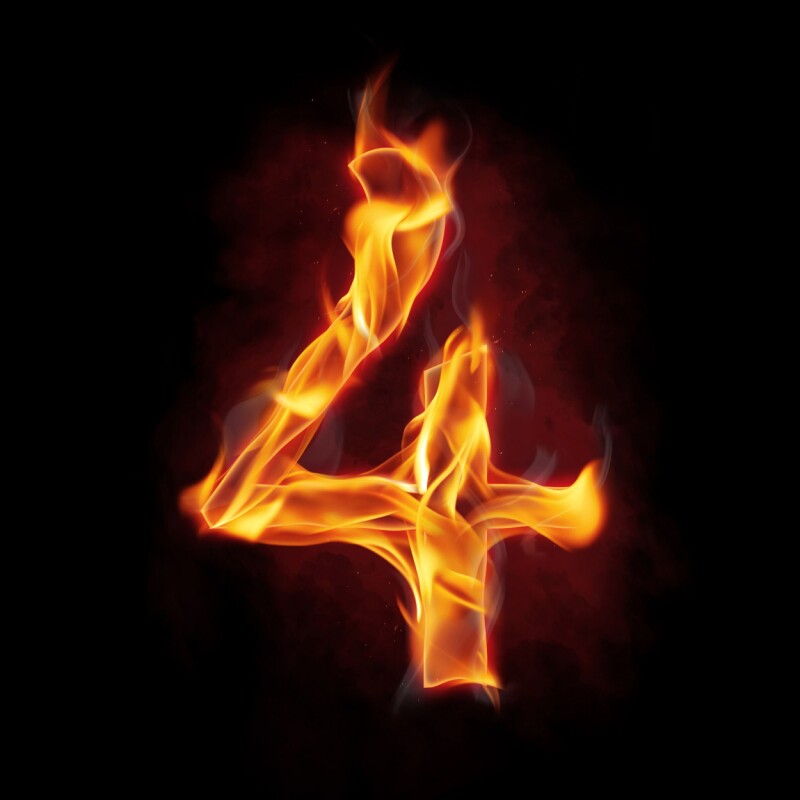
Browser makers such as Mozilla, Chrome, and Apple have since taken steps to remediate the issue by no longer relying on the affected certificates, provided users install the relevant updates. However, it has been revealed that one of the compromised private keys is the number '4', which is particularly vulnerable to brute force attacks.
Other compromised keys include 56, 115, 66, 155, 156, 230, and 237, making all eMudhra-issued certificates susceptible to a range of security threats. While Mozilla, Chrome, and Apple have already taken action to address the issue, it is crucial for developers and services that relied on these certificates to evaluate their environments and ensure they are not vulnerable to potential attacks.
Written by urgent.news from The Register Science's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.
This story
This is one outlet's version. Read the fullest account.