Microsoft targets the ‘agentic insider’ with new controls for rogue AI agents
Microsoft Corp. today introduced security controls for rogue artificial intelligence agents that cut back what an agent may do as its assessed risk climbs. The release takes on what Hayete Gallot, executive vice president of Microsoft Security, called the “agentic insider” in a blog post. Enterprise agents are often overprivileged, and their numbers are growing […] The post Microsoft targets the…
Microsoft has rolled out new security controls aimed at rogue AI agents, focusing on the "agentic insider" threat. These controls are designed to limit the actions of an AI agent as its assessed risk level increases. Executive Vice President of Microsoft Security, Hayete Gallot, highlighted the growing number and overprivileged nature of enterprise AI agents in a recent blog post.
Microsoft Chairman and CEO Satya Nadella recently argued in an essay that companies should treat AI models as insider risks, with safeguards kept outside the model itself. The company's new controls begin with the identification of agents, with Microsoft's discovery tools now able to spot 60 different types of local agents on employee machines. Examples of these agents include those from Anthropic, OpenAI, and Microsoft's own GitHub unit.
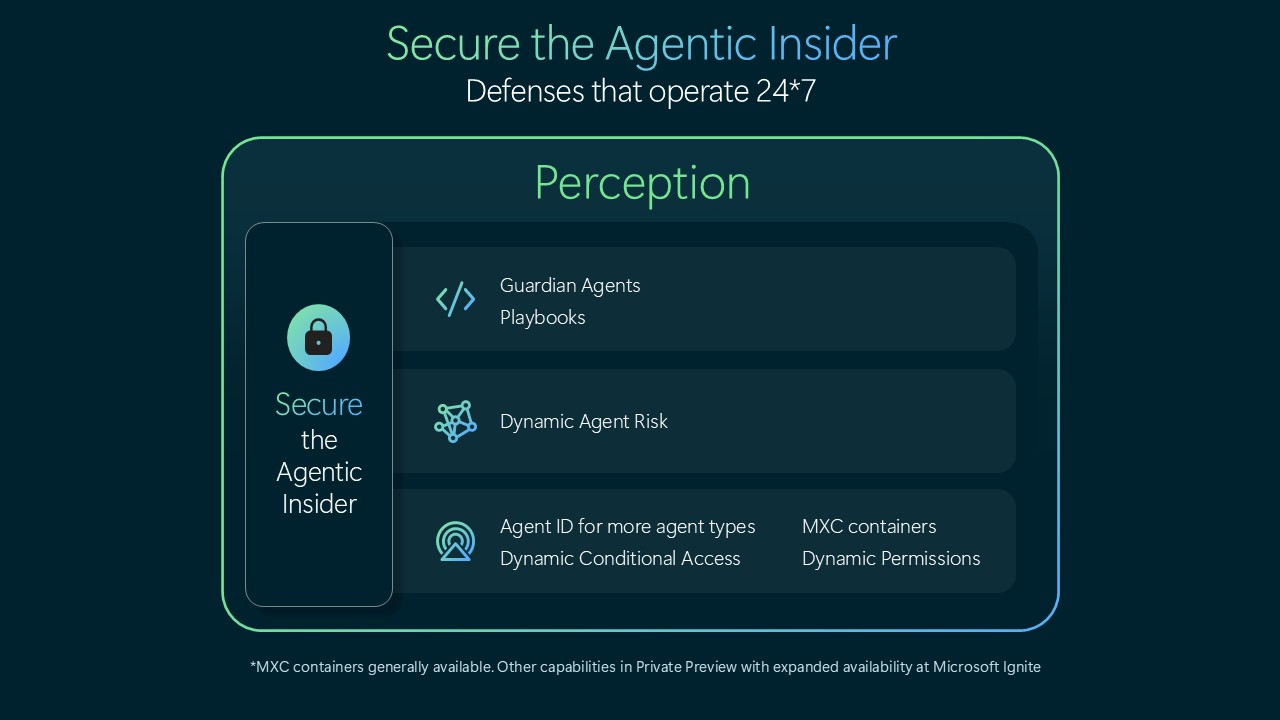
The introduction of Dynamic Agent Risk allows for the continuous updating of each agent's risk score based on signals from Microsoft's various identity, endpoint, cloud, and network tools. As the risk score rises, the Dynamic Conditional Access feature decides the appropriate action. This could range from limiting an agent's ability to change anything, to holding higher-impact actions for human approval, or even isolating or stopping the agent entirely.
Access becomes temporary under Dynamic Permissions, ensuring that agents only have the necessary access for a single task.
Microsoft's Execution Container sandbox ensures that even if an agent is compromised, it cannot switch off the sandbox. Project Perception, an agentic security system introduced in July, has received new tools to aid in the investigation of agents. Guardian Agents, a new team within Project Perception, can recommend containment measures or apply them on their own, while still respecting human policy and approval rules.
Microsoft also plans to provide more information about why an agent acts, by incorporating chain-of-thought and other model-level signals into Dynamic Agent Risk. However, they clarify that this model transparency will not replace containment measures. Microsoft is positioning these new controls as part of Project Perception and Microsoft 365 E7, a suite that includes Agent 365 and Microsoft 365 Copilot. The company is set to provide more details at Microsoft Ignite, which begins on November 17.
Written by urgent.news from SiliconANGLE's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.