Hackers Heat French Supermarket Fridges, Sparking Fires and Spoiling Food
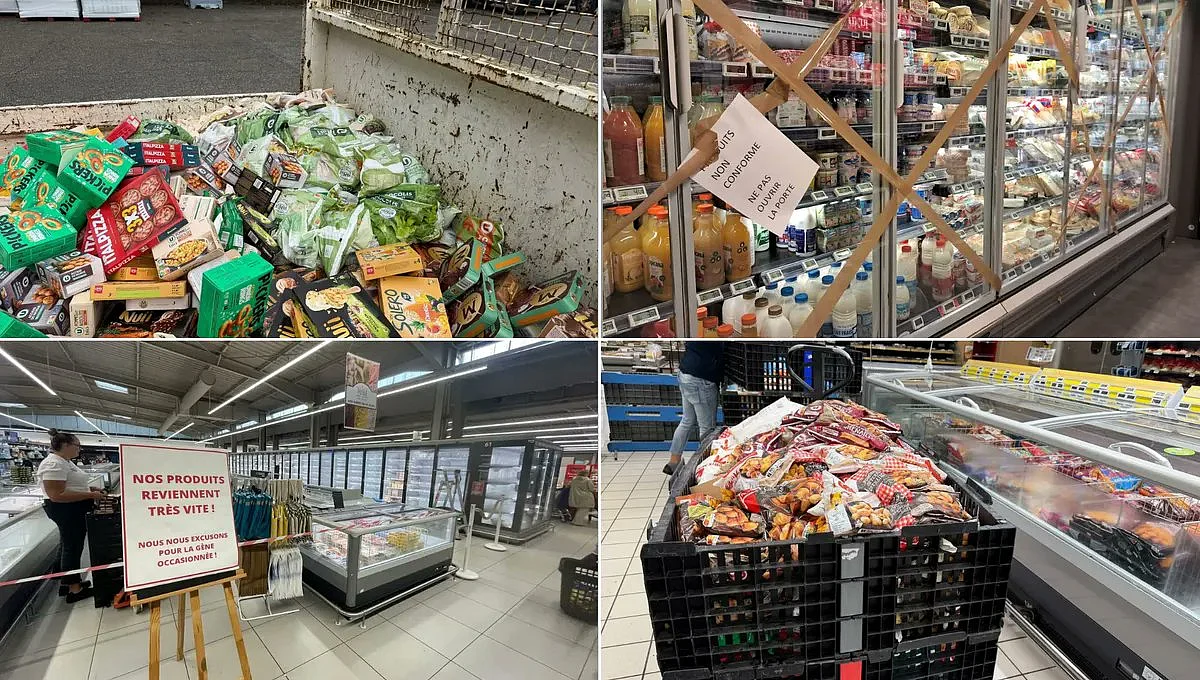
PARIS (Reuters) - Hackers raised the temperature of refrigerators and freezers at hundreds of French supermarkets to as high as 50 degrees Celsius overnight, causing fires and spoiling food. The Paris prosecutor's office said on Monday that a "large-scale" attack was "affecting connected refrigerators in several major food retailers across France", leading to food losses and fires.
Hackers targeted refrigeration systems in hundreds of French supermarkets, causing temperatures to soar to 50°C and leading to fires and spoiled food. The Paris prosecutor's office confirmed a "large-scale" attack affecting numerous food retailers across the country, resulting in estimated losses of tens of millions of euros. Prime Minister Sebastien Lecornu directed the National Cybersecurity Agency (ANSSI) to investigate the incident, which was said to have impacted stores in France and potentially other European countries.
Major supermarkets like Carrefour, Monoprix, and Intermarche reported significant disruptions, with food losses and damaged equipment. The vulnerability was traced back to outdated firmware in Danfoss refrigeration management systems, with the company admitting to running outdated software. French retail associations called for transparency from Danfoss, and affected stores worked to restore operations.
Meanwhile, Dutch retailer Ahold Delhaize indicated it was experiencing a "security issue" and took systems offline as a precaution.
Written by urgent.news from The Japan News by The Yomiuri Shimbun's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.