Danfoss Refrigeration RCE: OT Sabotage via Supply Chain Compromise
Originally published on satyamrastogi.com French supermarket chains targeted via Danfoss controller compromise. Remote defrost attack exploited unpatched IoT devices in critical supply chain infrastructure, demonstrating OT vulnerability cascade. Danfoss Refrigeration RCE: OT Sabotage via Supply Chain Compromise Executive Summary On October 12, 2026, coordinated cyberattacks targeting Danfoss…
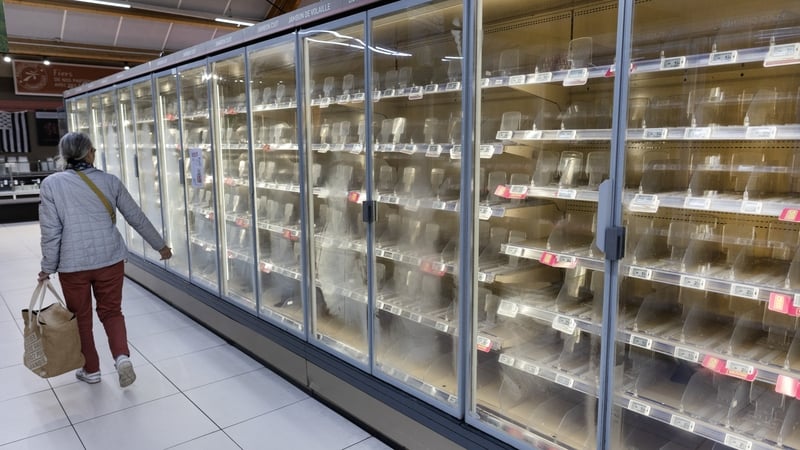
French supermarkets faced severe disruptions when French refrigeration controller manufacturer Danfoss suffered a supply chain compromise on October 12, 2026. This OT sabatoge demonstrated the vulnerabilities in industrial control systems.
Attackers exploited unpatched IoT devices by compromising Danfoss service accounts and cloud management portals. They weaponized the software supply chain, using legitimate manufacturer protocols to distribute malicious firmware and trigger defrost cycles remotely. The attackers moved laterally within supermarket networks, commandeered temperature monitoring systems, and forced the shutdown of cold storage units.
The attack showcased a cascade of OT vulnerabilities. The initial compromise involved trusted relationships, compromised software supply chains, and lateral tool transfers to exploit Modbus protocol vulnerabilities. Despite the sophisticated attack chain, the impact was devastating - millions of dollars in perishable inventory lost and critical supermarket operations halted overnight.
This incident highlights the dangers of failing to secure industrial control systems. It also underscores the risks of relying on outdated supply chain practices and the importance of rigorous vulnerability management for critical infrastructure.
Written by urgent.news from Dev.to's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.