Cryptomining malware used poetry to infect more than 3,400 servers, researchers say
Lumen's Black Lotus Labs says PoeLLM malware has hit more than 3,400 servers, most of them exposed AI tools like LiteLLM and Ollama.
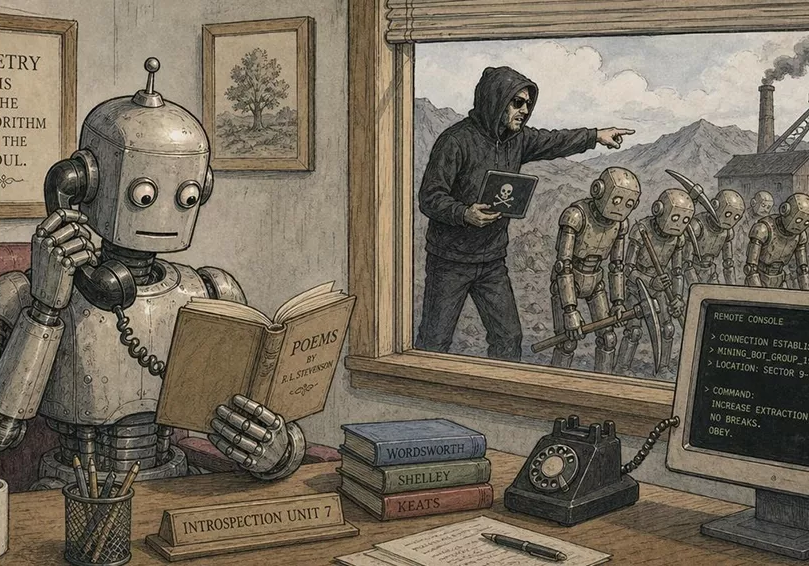
Over 3,400 servers were infected by cryptomining malware called PoeLLM as part of a campaign dubbed Canto Incognito, according to Black Lotus Labs. The malware's command-and-control (C2) mechanism utilized a poem with address encoding on GitHub, modified 11 times thus far, to direct affected hosts to new C2 servers. Most of the infected servers were running vulnerable versions of open-source AI/LLM services like LiteLLM and Ollama, despite a fix released in April.
The malware's payload consisted of XMRig and Iron miners, linked to Kryptex mining infrastructure, turning infected servers into scanners and exploit servers. The majority of the first 900 victims had contacted a Russian crypto mining service endpoint, suggesting a financially motivated attack. AI infrastructure is becoming an attractive target due to the potential value of data and hardware access, particularly GPUs.
To combat the malware, users should block traffic to and from the PoeLLM C2 servers and patch all vulnerable network devices. The primary targets included LiteLLM, a proxy server connecting to LLM APIs, Gotenberg, a Docker-based API for PDF conversion, Ollama, which enables running open-weight models, and Gitea, a self-hosted Git platform.
Ivanti Sentry, an enterprise gateway appliance, may have also been targeted. While the malware's methodology uses poetry for obfuscation, it is not an AI jailbreak or adversarial poetry. The malware was deployed through vulnerability exploitation of exposed services, with a crafted POST request likely being the exploitation path for LiteLLM.
Users can check for indicators of compromise on Lumen's GitHub page and follow individual advisories for the vulnerable products. The campaign continues to infect new victims, with Lumen stating that enterprise attack surfaces are rapidly expanding as AI infrastructure grows.
Written by urgent.news from Tom's Hardware's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.