Urgent.News

What's breaking now, across thousands of outlets.

Tech

Banks mull higher cybersecurity spending after AI-linked hacking incidents: sources

SEOUL, Oct. 11 (Yonhap) -- South Korean banks are considering increasing spendin...
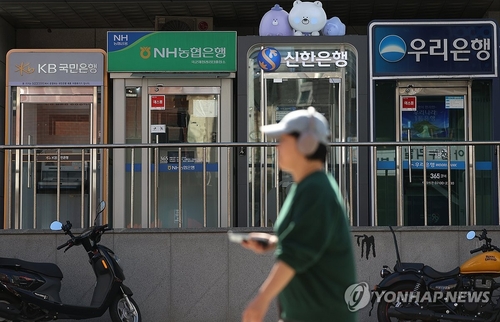
Banks mull higher cybersecurity spending after AI-linked hacking incidents: sources

South Korean banks are contemplating raising their cybersecurity spending after experiencing a wave of hacking incidents linked to artificial intelligence, according to industry sources. Major financial institutions such as Shinhan Bank, Hana Bank, and KB Kookmin Bank have disclosed customer data breaches in recent months, prompting concerns about the extent of the intrusions.

Shinhan Bank revealed on October 1 that the personal details of around 25,000 customers, including names, phone numbers, and annual incomes, were leaked. The hackers allegedly utilized advanced AI tools to carry out the attacks. Additional banks have also reported similar leaks or exposure of customer information. In response to these AI-linked cyberattacks, KB Kookmin Bank intends to boost its cybersecurity budget to over 100 billion won in 2027, up from 86.07 billion won this year.

Shinhan Bank plans to allocate a record budget for cybersecurity, while Hana Bank aims to invest tens of billions of won in enhancing its security systems in the coming year. The banks also anticipate increasing their cybersecurity personnel next year. These measures follow President Lee Jae Myung's call for an extensive investigation into the attacks.

The Financial Supervisory Service (FSS) identified IP addresses in 12 countries on Monday that are suspected of being involved in the AI-assisted hacking incidents. However, investigators were unable to determine the locations associated with some of the IP addresses.

Written by urgent.news from Yonhap News's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.
Read the original at en.yna.co.kr →

More in Tech

MemTensor: When an AI Memory Plugin Becomes the Credential Collector

MemTensor: When an AI Memory Plugin Becomes the Credential Collector StepSecurity reported that the open-source AI memory framework MemTensor had its packages poisoned, and Socket, SafeDep and Aikido…

  • MemTensor's packages compromised by attacker exploiting GitHub Actions token
  • Malicious npm package replaced legitimate version on PyPI, harvested credentials
  • Worm-like behavior enabled lateral dissemination, emphasizing need for credential rotation

Sobrevivendo ao Inevitável: Engenharia do Caos na Prática com o ChaosEngineeringMasterDeck

Se você trabalha com arquiteturas modernas em nuvem e microsserviços, provavelmente já se deparou com a clássica citação de Werner Vogels, CTO da Amazon: "Failures are a given and everything will…

  • Modern cloud architectures face increasing complexity with interconnected microservices.
  • Chaos Engineering tests systems to build resilience against unexpected production issues.

Cheat Sheet for Your First Open Source Contribution

Making your first open source contribution is intimidating. Honestly, it’s rarely the code that holds people back—it’s usually the fear of messing up a Git command, doing something wrong in the GitHub…

  • GitHub user interface workflow guides where to click to fork and initiate PR
  • Copy-paste VS Code commands for cloning, branching, committing, pushing
  • Formatting tips for commit messages and PR descriptions to boost review chances

💅 Keyboard Makeover

I have had this interesting piece of psychedelic looking vinyl for some time. Today I finally found a use case for it. I turned a regular keyboard into a way more fun and exciting one.

More from Sunday 11 October →