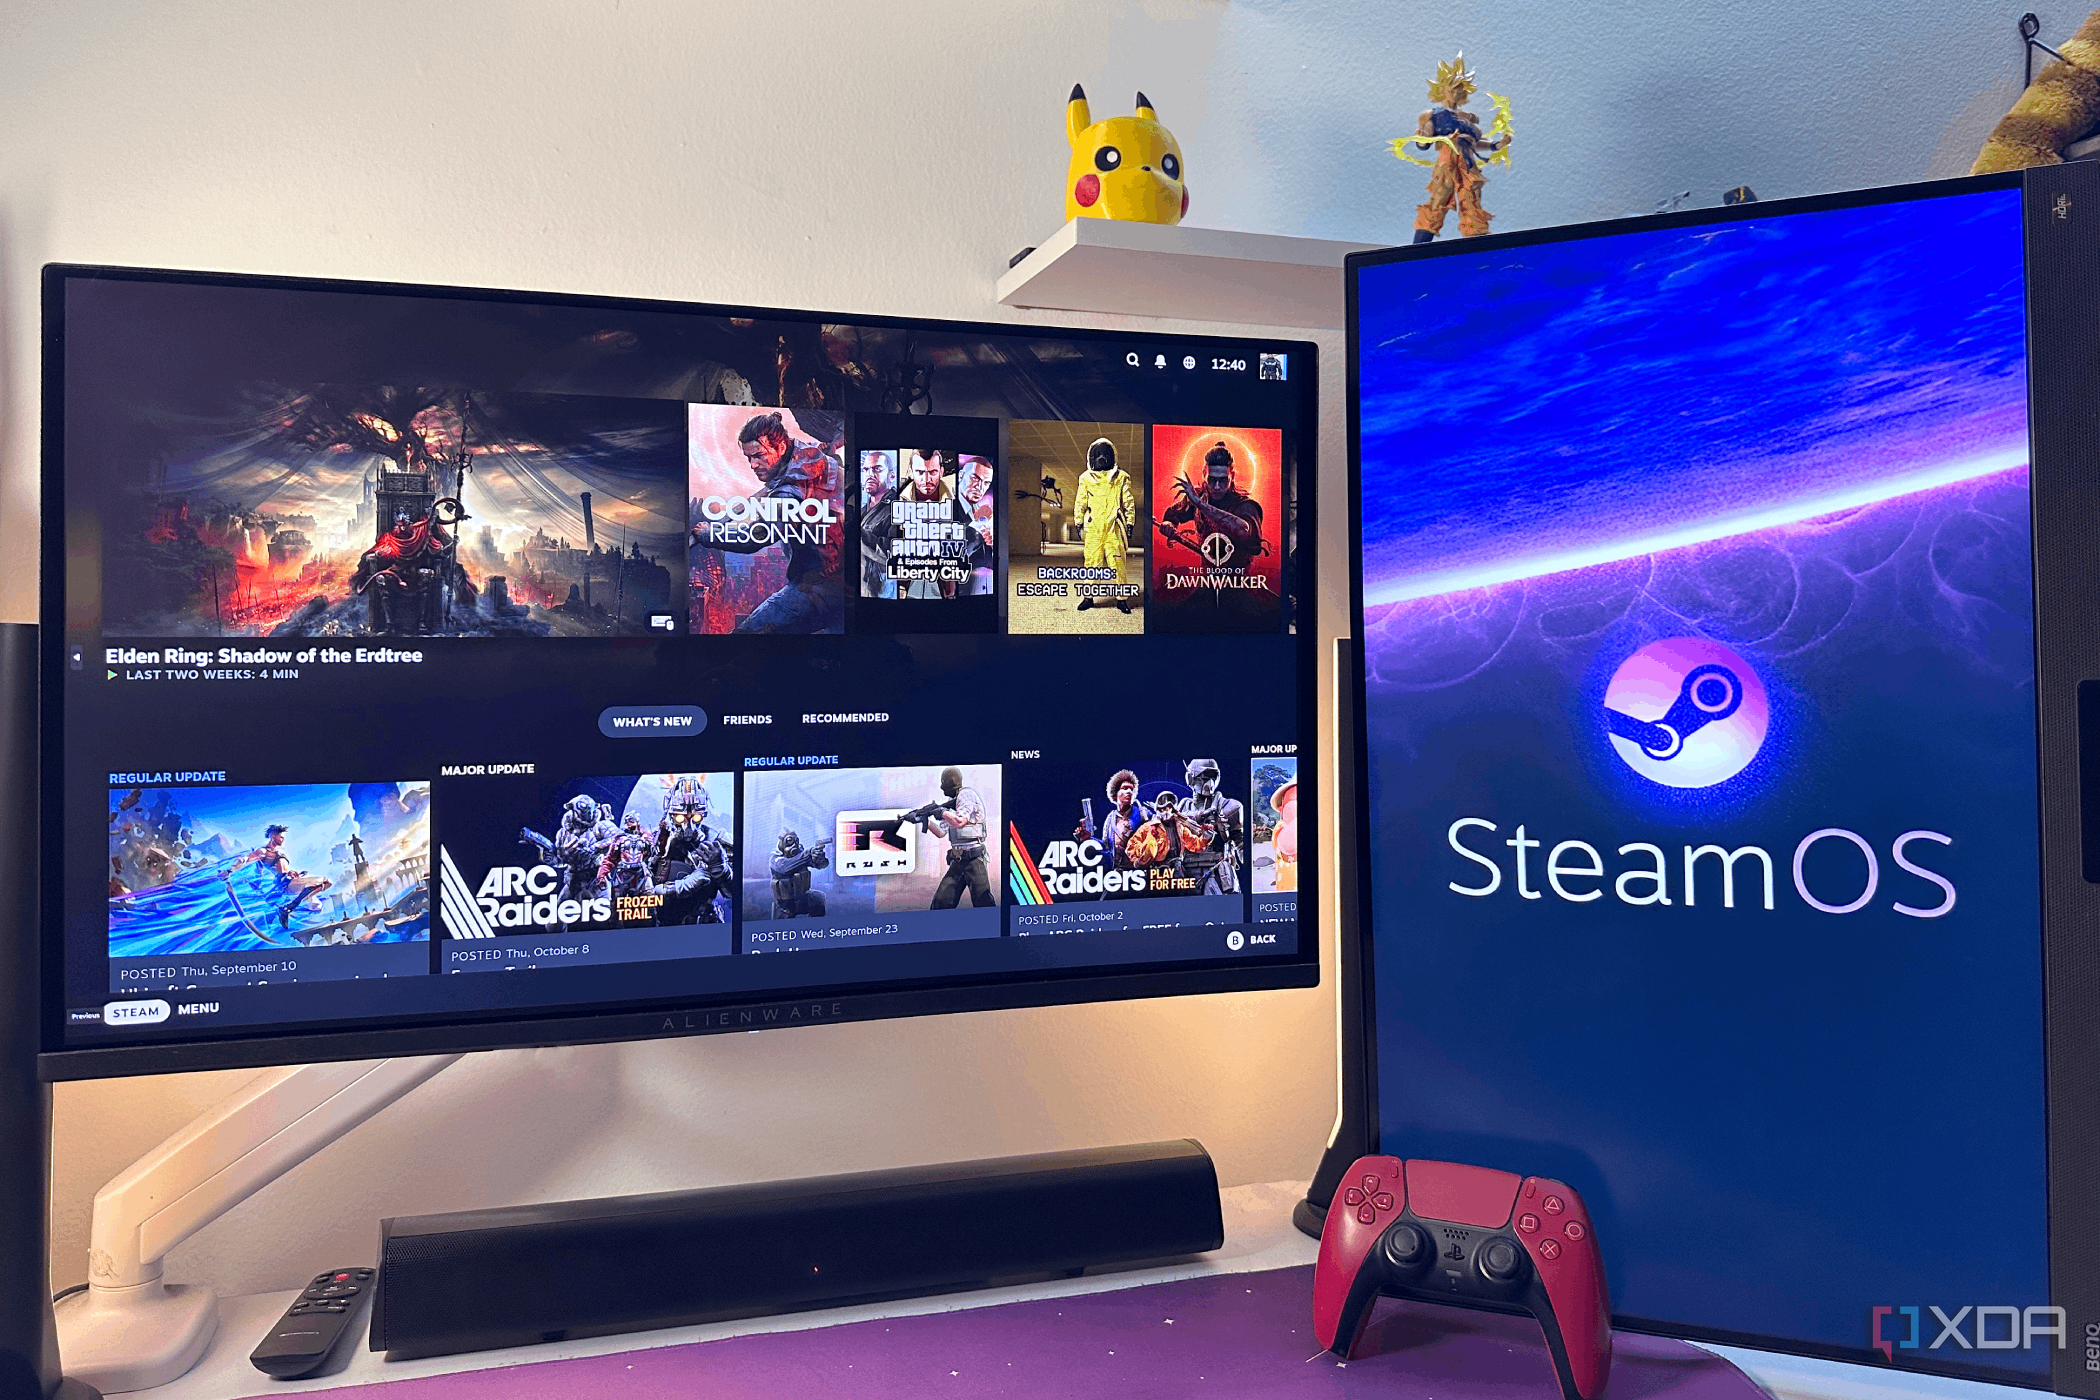
The $1,049 Steam Machine isn't a bad deal — I just priced one out and proved it to myself
Not quite the rip-off I thought it was
We haven't written up this one. XDA Developers has the full story — the link below goes straight to it.
What's breaking now, across thousands of outlets.
Not quite the rip-off I thought it was
We haven't written up this one. XDA Developers has the full story — the link below goes straight to it.
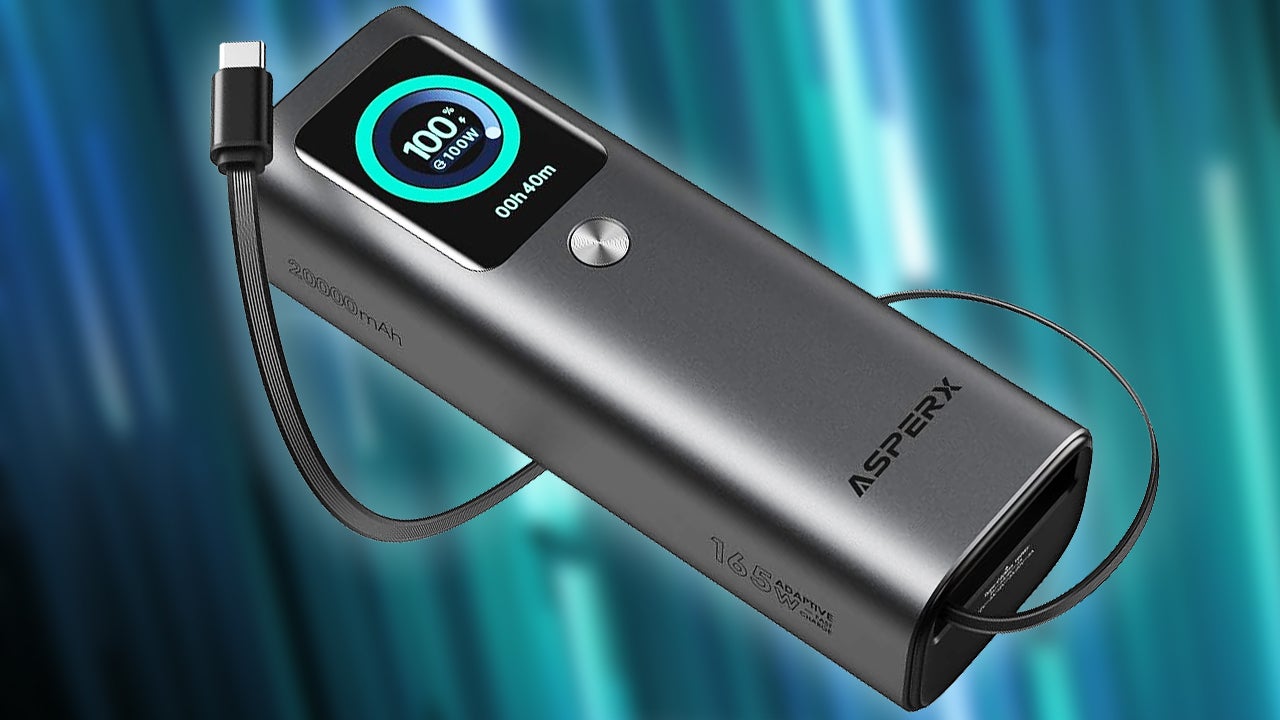
Features a unibody aluminum alloy shell and a retractable USB-C cable.
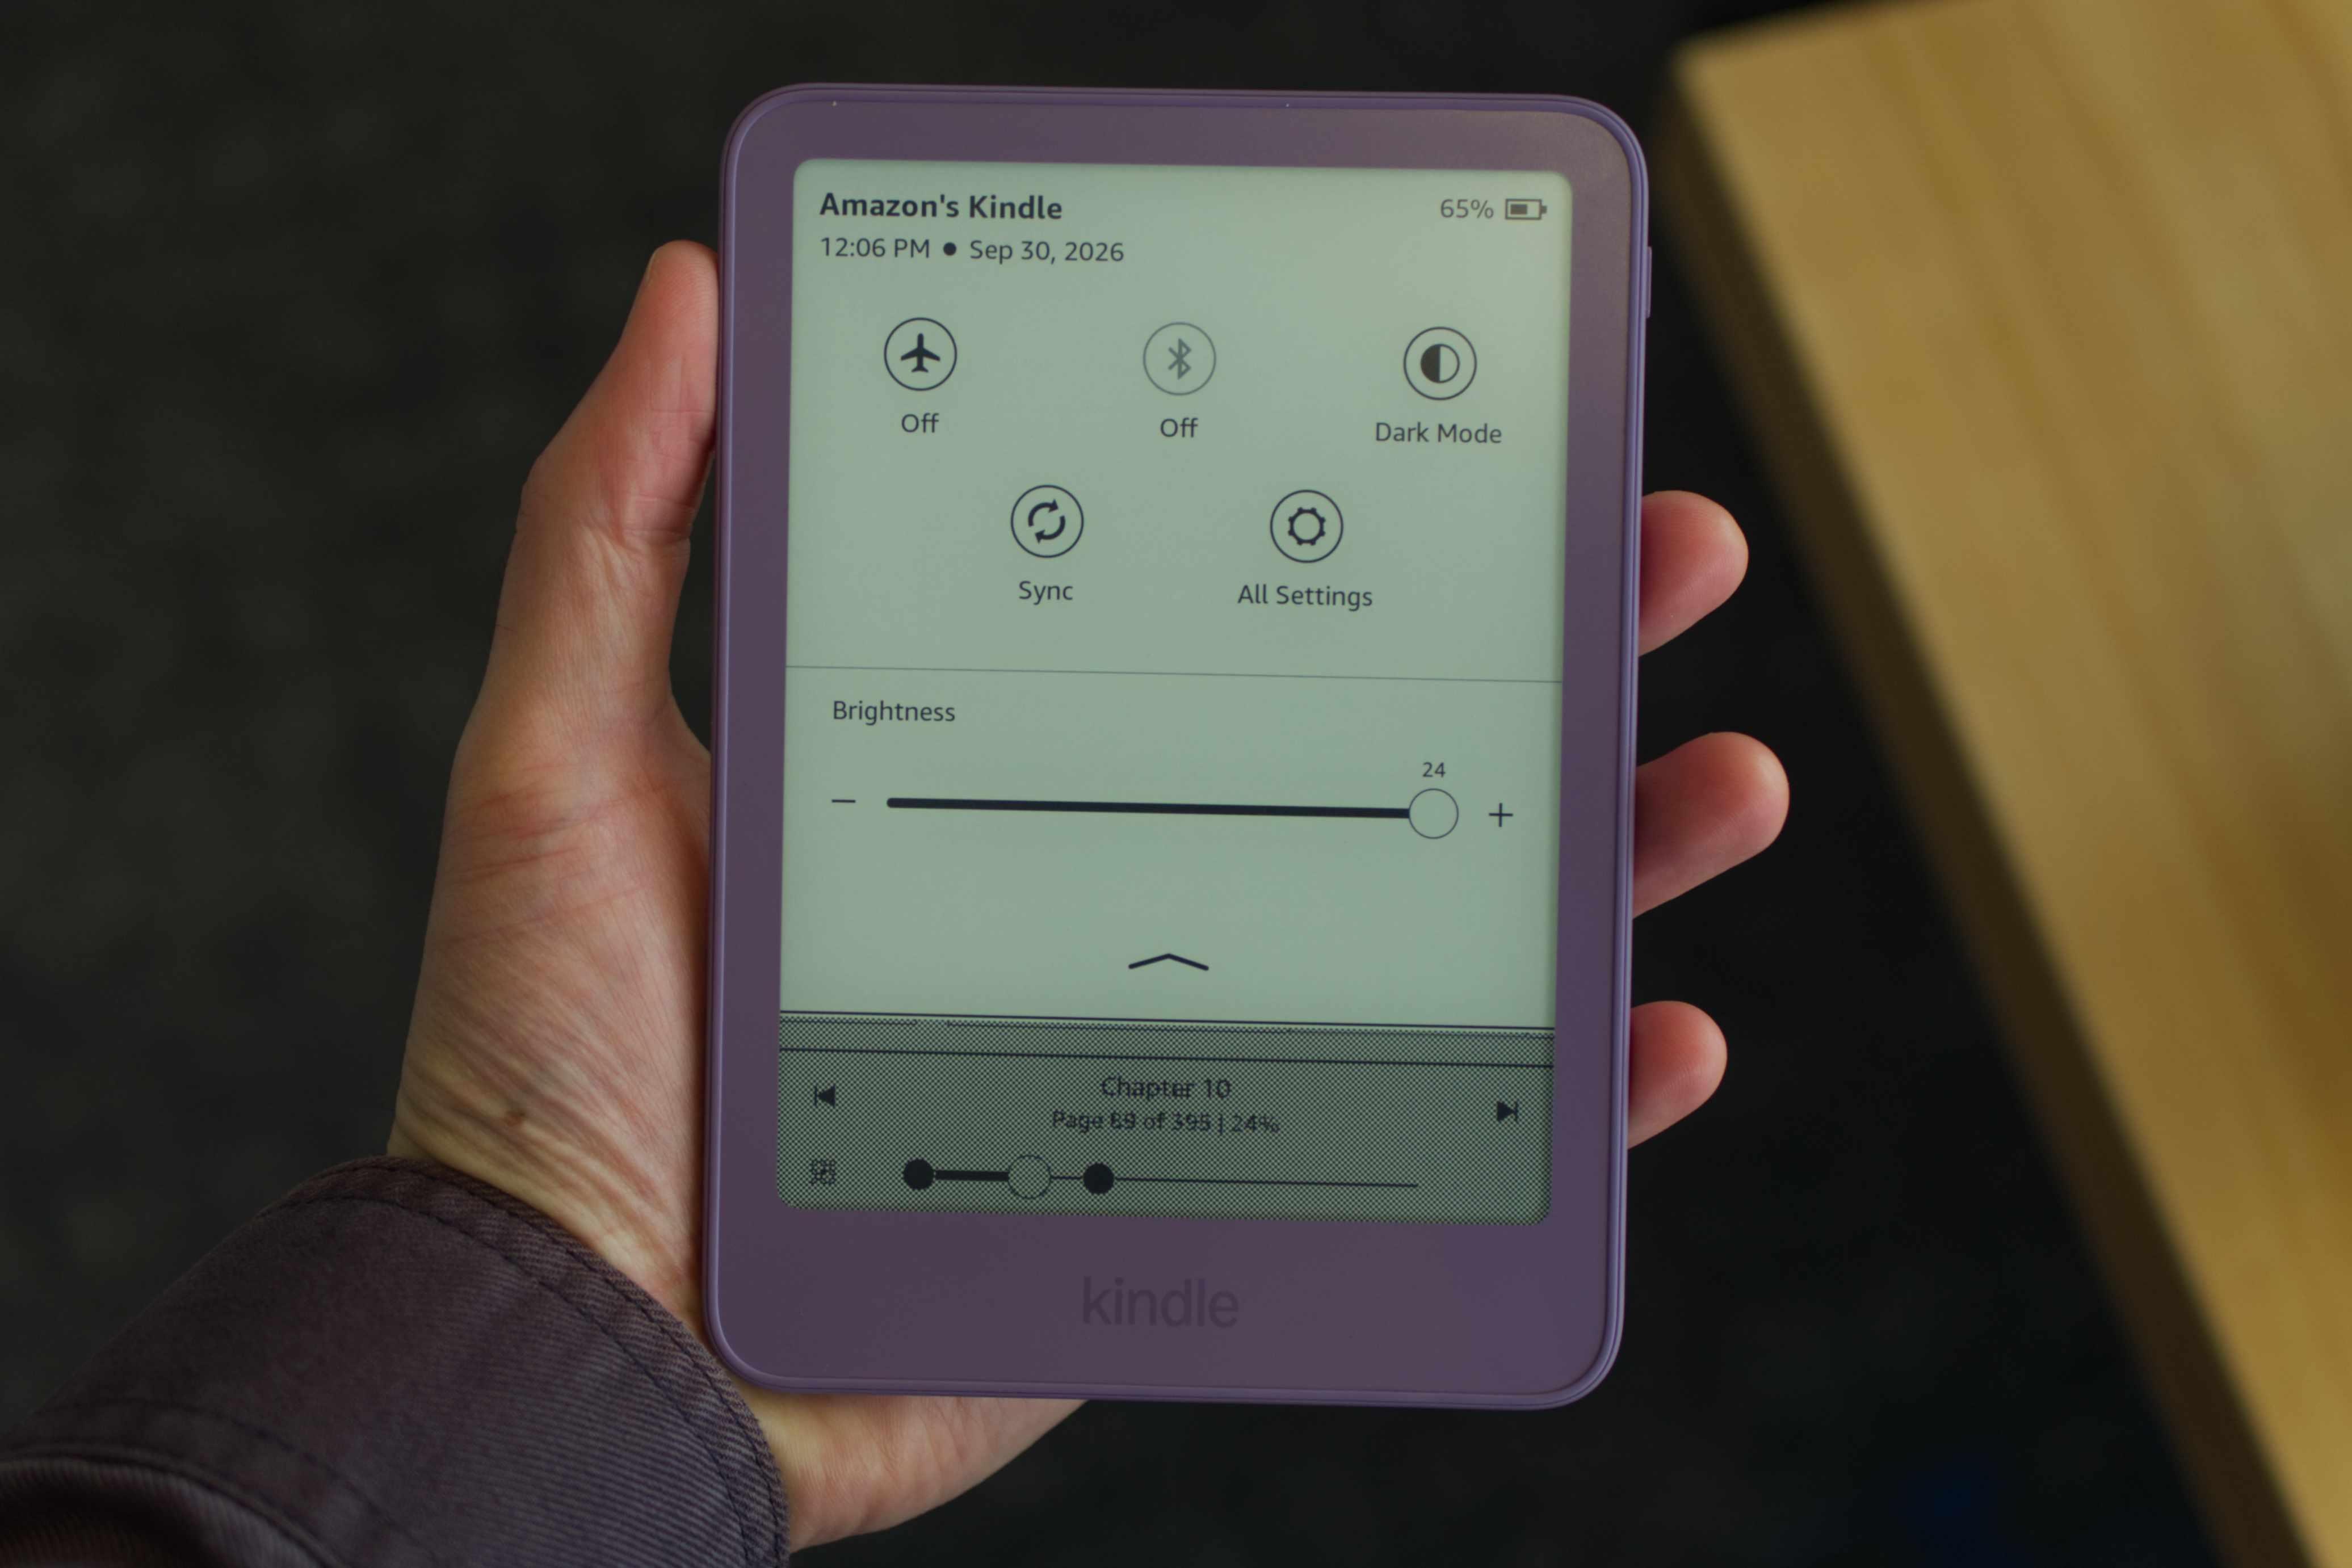
Some users are reporting that the new Kindles have a light leak issue that is especially apparent when using dark mode. The latest base-model Kindles have a flush bezel that gives them a sleek…
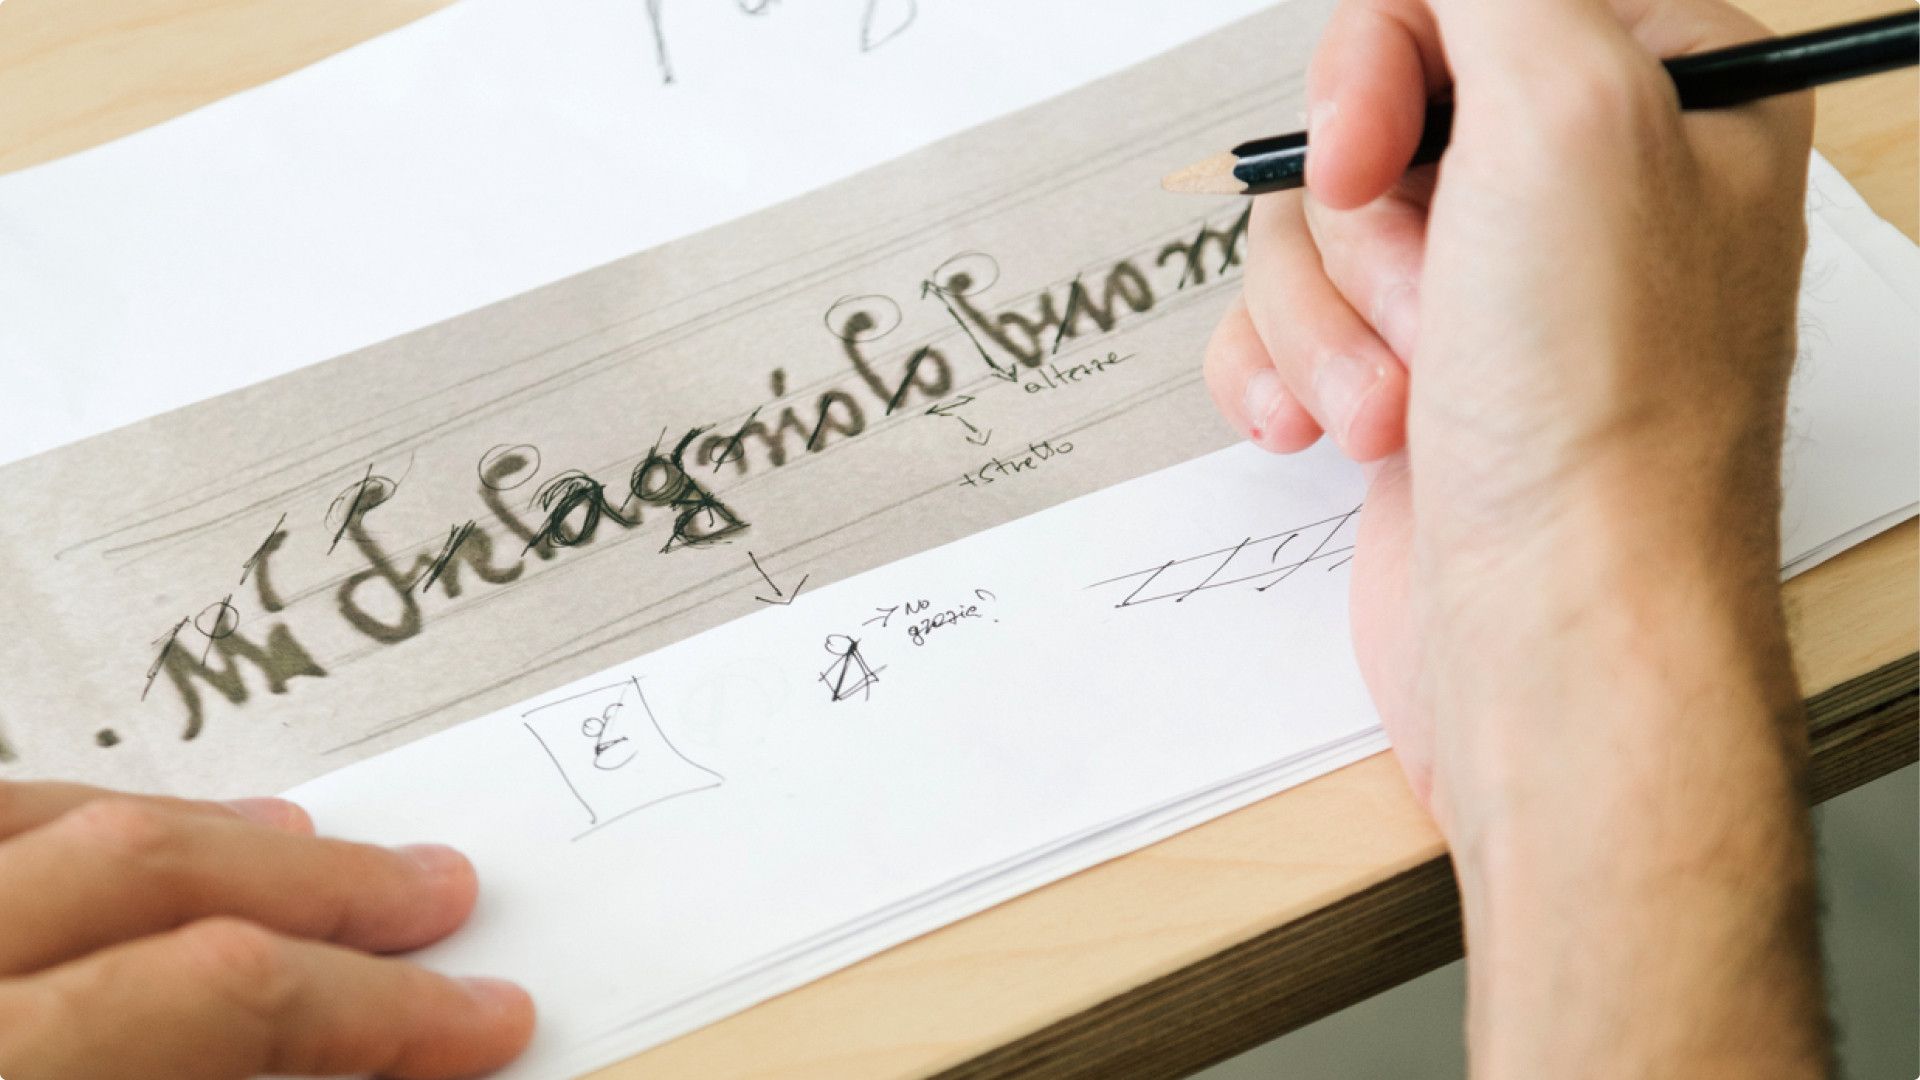
'I really don't feel their execution lives up to their intent': new Word font is based on Michelangelo's handwriting, but some think the two are 'wildly' different.
iOS 27 brings new features to Apple Wallet , Maps , Notes , Messages , and more —and it packs key upgrades for the Mail app too. Here’s everything new for Apple Mail in iOS 27. more…
The hot new Fitbit could formally debut in just a few more days.
CVE-2026-100727: unauthenticated file read in GROWI's local upload mode GROWI, the wiki and collaboration platform published by GROWI, Inc., received a security fix in version 7.5.5 on October 5…