Some cheap Android phones are shipping with malware baked in
Midnight Mimosa malware arrives pre-served.
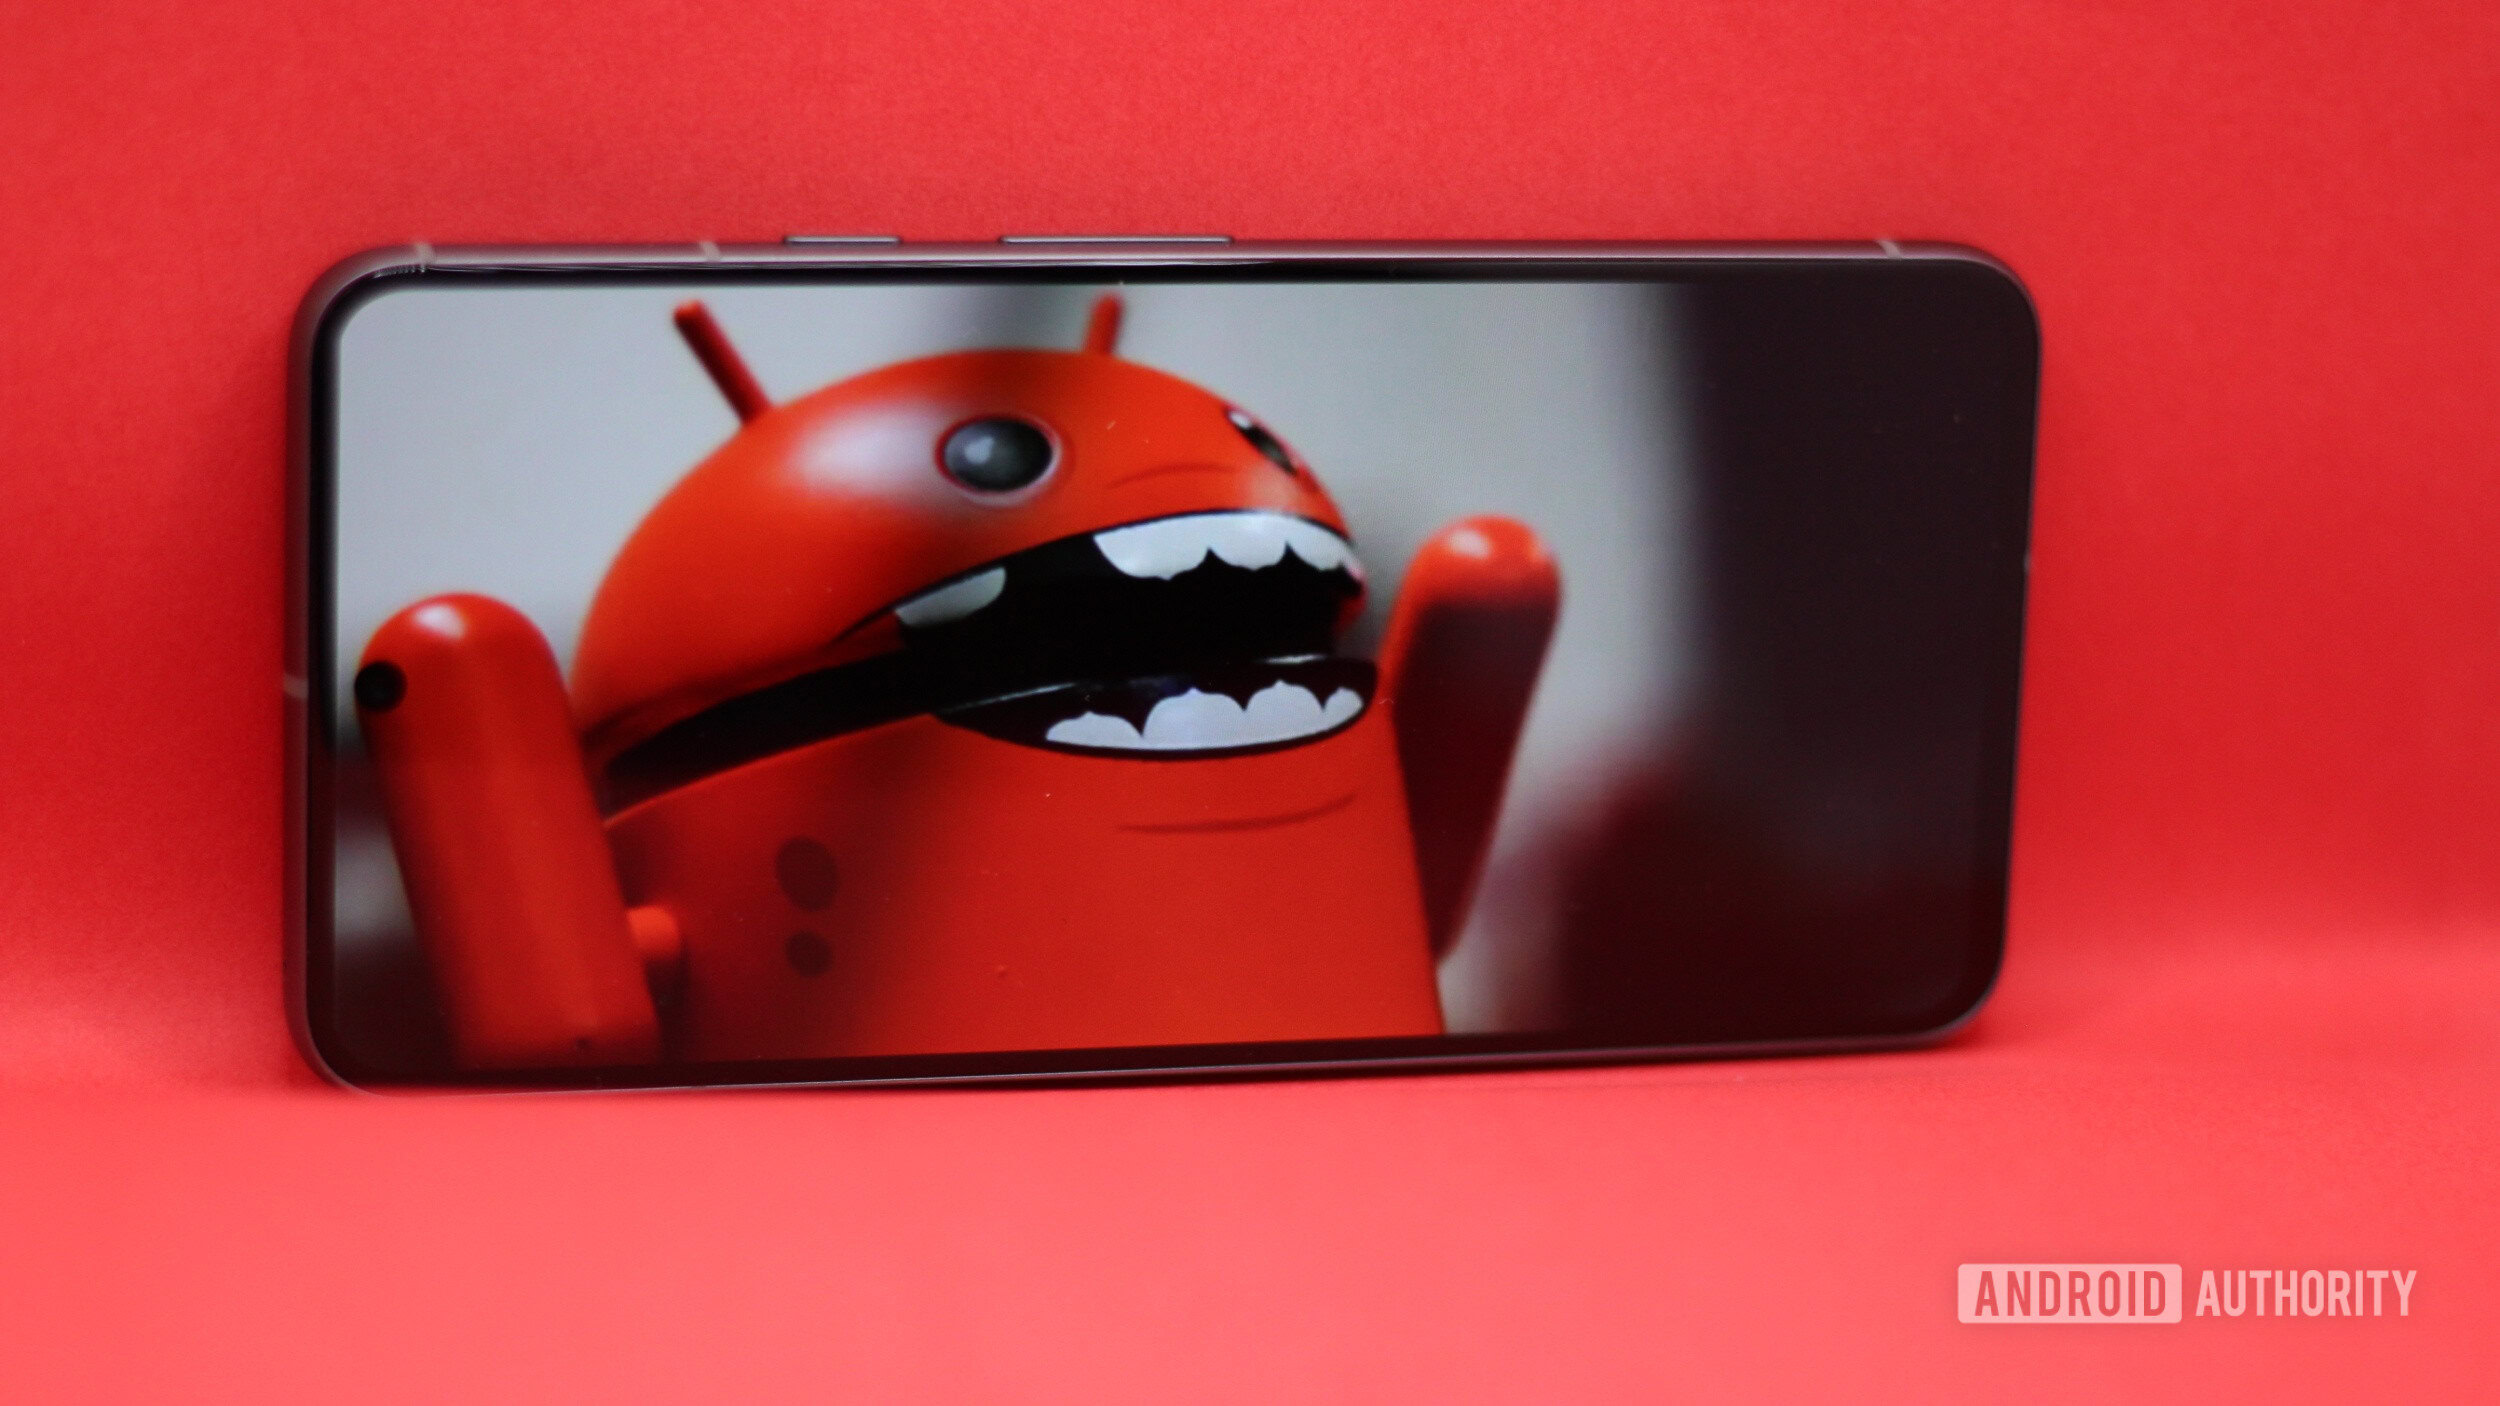
Researchers have discovered a concerning malware campaign targeting some budget Android phones, including models from Doogee and Cubot. Dubbed Midnight Mimosa, this malicious software is embedded within the phone's firmware and can install applications, request permissions, bypass Play Protect, and transform devices into part of a botnet.
The campaign has been observed on thousands of devices in over 150 countries. Removing the malware proves challenging due to its location in the system partition. Over the years, warnings have been issued about the risks of downloading unknown apps onto smartphones, emphasizing the importance of relying on the Google Play Store and being cautious when sideloading APKs from untrusted sources.
However, what if your phone was already infected before you even unboxed it? Bitdefender researchers have uncovered this new malware campaign, Midnight Mimosa, which poses a significant threat to unsuspecting users.
Written by urgent.news from Android Authority's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.
Also reported by 3 other outlets
- Old Android phones make better smart home wall panels than any $200 displays xda-developers.com
- Thousands of cheap Android phones shipped with ad-fraud malware therecord.media
- Midnight Mimosa malware is preinstalled on cheap Android phones androidpolice.com