Malicious VPN config files can let attackers run commands on Asus routers
Until routers on Asus’s 3.0.0.6_102 firmware are updated, the company says not to import untrusted VPN files.
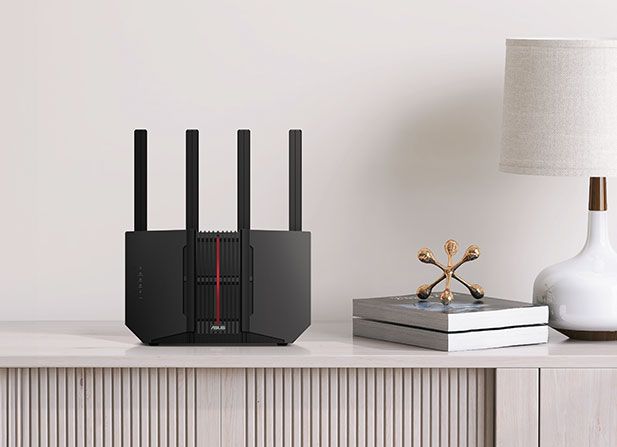
Malicious VPN configuration files uploaded through an Asus router's web interface could allow attackers to execute arbitrary commands on the device, a critical security risk that the company has patched. A second bug, enabled through debug code, could bypass security checks to allow Telnet commands with potential root privileges.
Asus advises users to only import VPN files from trusted sources. The vulnerabilities, CVE-2026-14157 and CVE-2026-13313, have high severity scores on the CVSS scale. Users are advised to update their firmware to version 3.0.0.6_102, and for affected motherboards, BIOS versions 1502 or 2203. Asus also recommends strong, unique passwords and discourages running untrusted scripts.
Written by urgent.news from Tom's Hardware's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.