(2nd LD) Regulator instructs financial firms to check security systems over series of cyberattacks on banks
SEOUL, Oct. 2 (Yonhap) -- The financial regulator on Friday instructed financial...
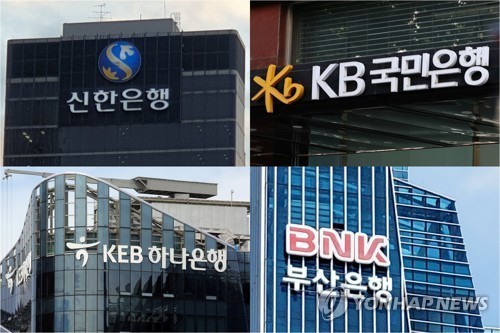
Seoul, on October 2, the Financial Services Commission issued an order to financial firms to review their computer security systems following a series of cyberattacks on major banks. This directive was prompted by the leak of personal information belonging to 89 of Hana Bank's clients, who had their data - including resident registration numbers, names, addresses, and phone numbers - stolen through a hacking attack.
Hana Bank's spokesperson expressed regret over the incident and pledged to do all it could to prevent such occurrences in the future.
Woori Bank and NH Nonghyup Bank were also targeted by similar hacking attacks, but they managed to thwart unauthorized access to their systems. Earlier, industry insiders had reported that customer information at KB Kookmin Bank, a prominent commercial bank, had been compromised following an identical incident by its rival Shinhan Bank. According to these sources, over 100 KB Kookmin Bank clients had their personal data stolen via hacking.
On Thursday, Shinhan Bank announced that personal information of about 25,000 clients, such as annual income, names, and phone numbers, had been leaked. Suspicion fell on overseas hackers who used advanced artificial intelligence tools to execute the assault. A division of the police responsible for cyberterror response has initiated a preliminary investigation into these recurring bank hacks, according to Yonhap News Agency.
Written by urgent.news from Yonhap News's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.