Urgent.News

What's breaking now, across thousands of outlets.

Tech

CISA Adds Exploited Cisco Catalyst SD-WAN Manager Auth Bypass to KEV

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Wednesday added a critical authentication bypass flaw impacting Cisco Catalyst SD-WAN Manager to its Known Exploited Vulnerabilities (KEV), following reports of active exploitation. The vulnerability, tracked as CVE-2026-76504 (CVSS score: 9.8), could allow an unauthenticated, remote attacker to access an affected system with
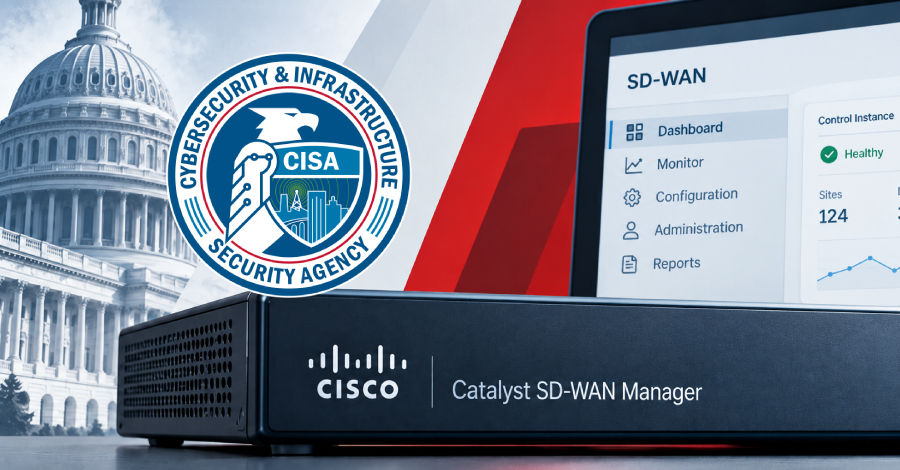
CISA Adds Exploited Cisco Catalyst SD-WAN Manager Auth Bypass to KEV

We haven't written up this one. The Hacker News has the full story — the link below goes straight to it.
Read the original at thehackernews.com →

More in Tech

Reliable Webhooks in TypeScript: Idempotency, Deduplication and Failure Recovery

Webhook providers deliver at least once, not exactly once. That single fact explains most webhook bugs: duplicate emails, double-credited balances, orders marked paid twice.

  • Implement authenticity by verifying provider's signature using raw body and HMAC digest
  • Record events in PostgreSQL table with unique constraint on provider's event ID
  • Separate acknowledging from processing by returning 2xx status and using row lock

What it does to your brain after solving Leetcode for more than 5 months?

TLDR: Solved atleast 1 question daily. Creating and following a list to identify and understand patterns Exhilaration, Exhaustion, and the will to continue.

  • Daily Leetcode practice maintains focus and motivation.
  • Intense problem-solving sessions cause exhaustion and accomplishment.
  • Persistence and breaks aid in overcoming mental blocks.

More from Thursday 1 October →