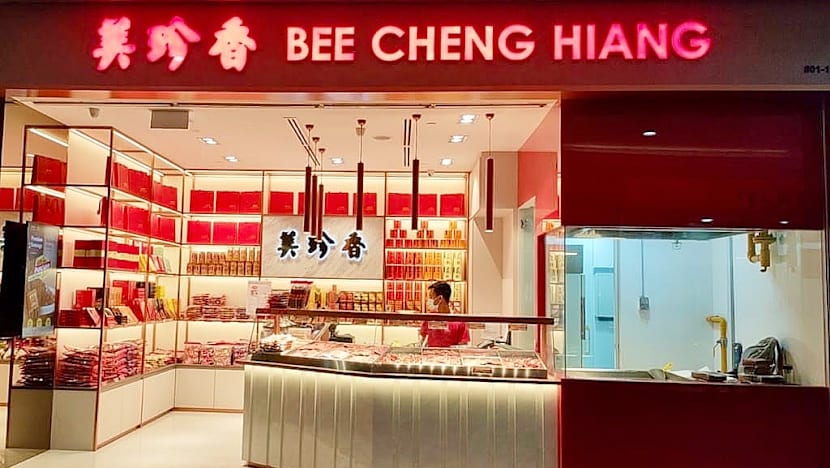
Nearly 100,000 Bee Cheng Hiang customers' email addresses exposed in first AI-related data breach in Singapore
"The incident was caused by a human error in developing the email distribution code with an AI tool," said the Personal Data Protection Commission.
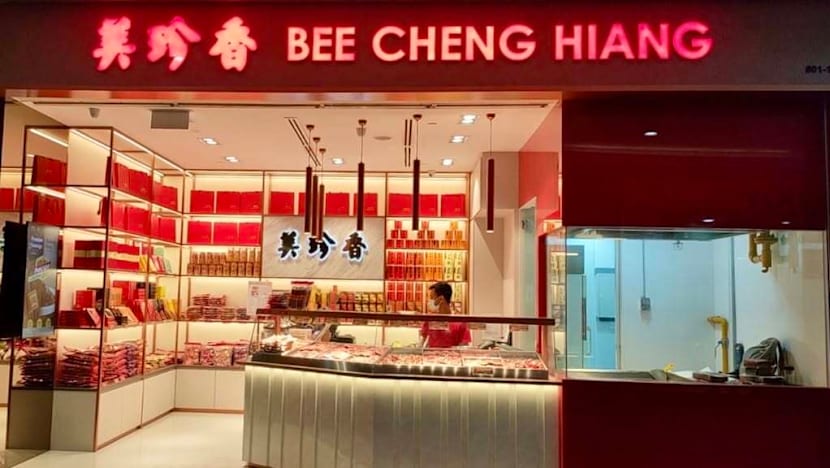
The email addresses of approximately 95,364 customers of Singaporean food stall chain Bee Cheng Hiang were exposed without permission in what the Personal Data Protection Commission (PDPC) described on September 30th as the country's first AI-related data breach. This incident took place in April when an employee utilized an AI tool to craft a Python script for disseminating a promotional email. The code inadvertently exposed the recipients' email addresses, leading to widespread visibility among the affected customers.
Written by urgent.news from CNA - Singapore's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.
This story
This is one outlet's version. Read the fullest account.
- Bee Cheng Hiang customers’ e-mail addresses exposed in Singapore’s first case of AI-related data breach businesstimes.com.sg
- Bad AI prompt exposes Bee Cheng Hiang customers’ e-mail addresses in first case of AI-related data breach straitstimes.com
- Nearly 100,000 Bee Cheng Hiang customers' email addresses exposed in first AI-related data breach in Singapore channelnewsasia.com