Legit Security launches agentic remediation for open-source dependency vulnerabilities
Tel Aviv, Israel, 30th September 2026, CyberNewswire
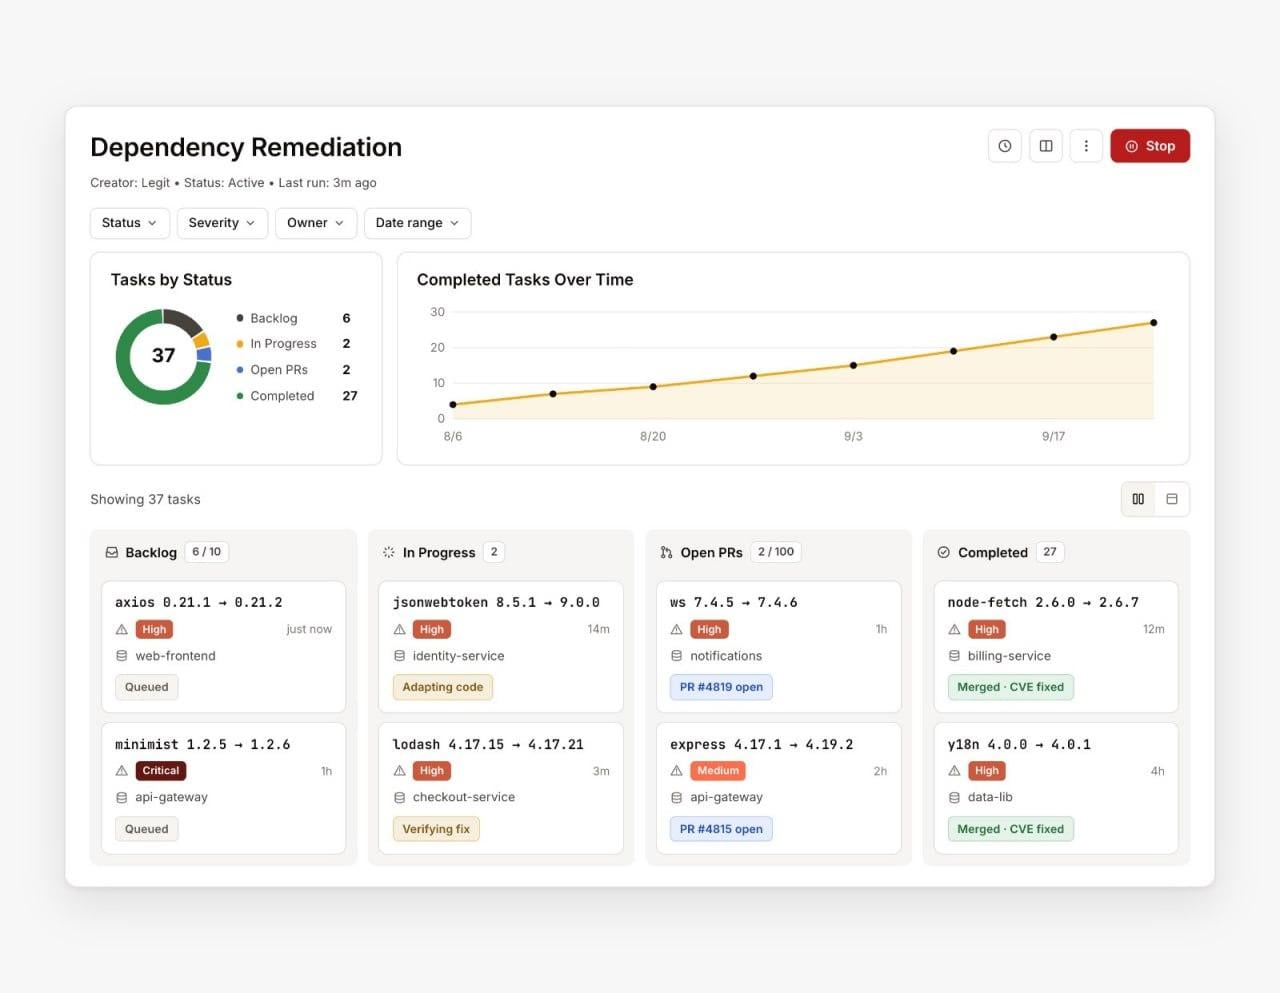
Tel Aviv, Israel – Legit Security has expanded its Agentic Remediation capability to address vulnerabilities in open-source dependencies, not just the company's own code. This move aims to bridge the gap between vulnerability detection and verified fixes, especially as AI-generated code increasingly drives software delivery.
With this expansion, Legit's Agentic Remediation can now handle vulnerabilities found in open-source dependencies, which are often the majority of modern codebases. Traditional find-it, fix-it AppSec workflows, reliant on human teams, struggle to keep up with the volume of potential vulnerabilities, particularly when they reside several layers deep in third-party packages.
The process begins when the agent identifies the vulnerable dependency, determining whether it's a direct or indirect (transitive) dependency within the codebase. It then locates the safest upgrade – the smallest version bump that resolves the issue, without breaking changes where possible. The agent applies the fix by updating the dependency configuration and regenerating the lockfile, while also scanning for the vulnerable version in other parts of the dependency tree.
Before opening a pull request (PR), the agent re-scans the fix to ensure the vulnerability is resolved and no new issues were introduced. When a major version upgrade is required, the agent performs an additional AI-assisted analysis layer to evaluate how the specific repository uses the package and proposes necessary source code adaptations. The PR then clearly flags this distinction, informing developers which aspects have been verified and which may need closer review before merging.
Legit Security sees this expansion as part of a broader effort to close the detection-verification gap for both first-party code and open-source dependencies, offering a solution that doesn't rely on manual backlog triage. For more information, contact Dave Howell at Legit Security (dave@legitsecurity.com).
Written by urgent.news from DevOps.com's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.