Oracle CISO puts humans at the center of AI security governance
As enterprises face AI-driven cyberattacks, AI security governance must control autonomous systems that can reach data, connect applications and act on users’ behalf. That makes human accountability a core security requirement. Traditional controls remain necessary, but security teams must also understand the data flows and processes agents create. People, therefore, need a new role in […] The…
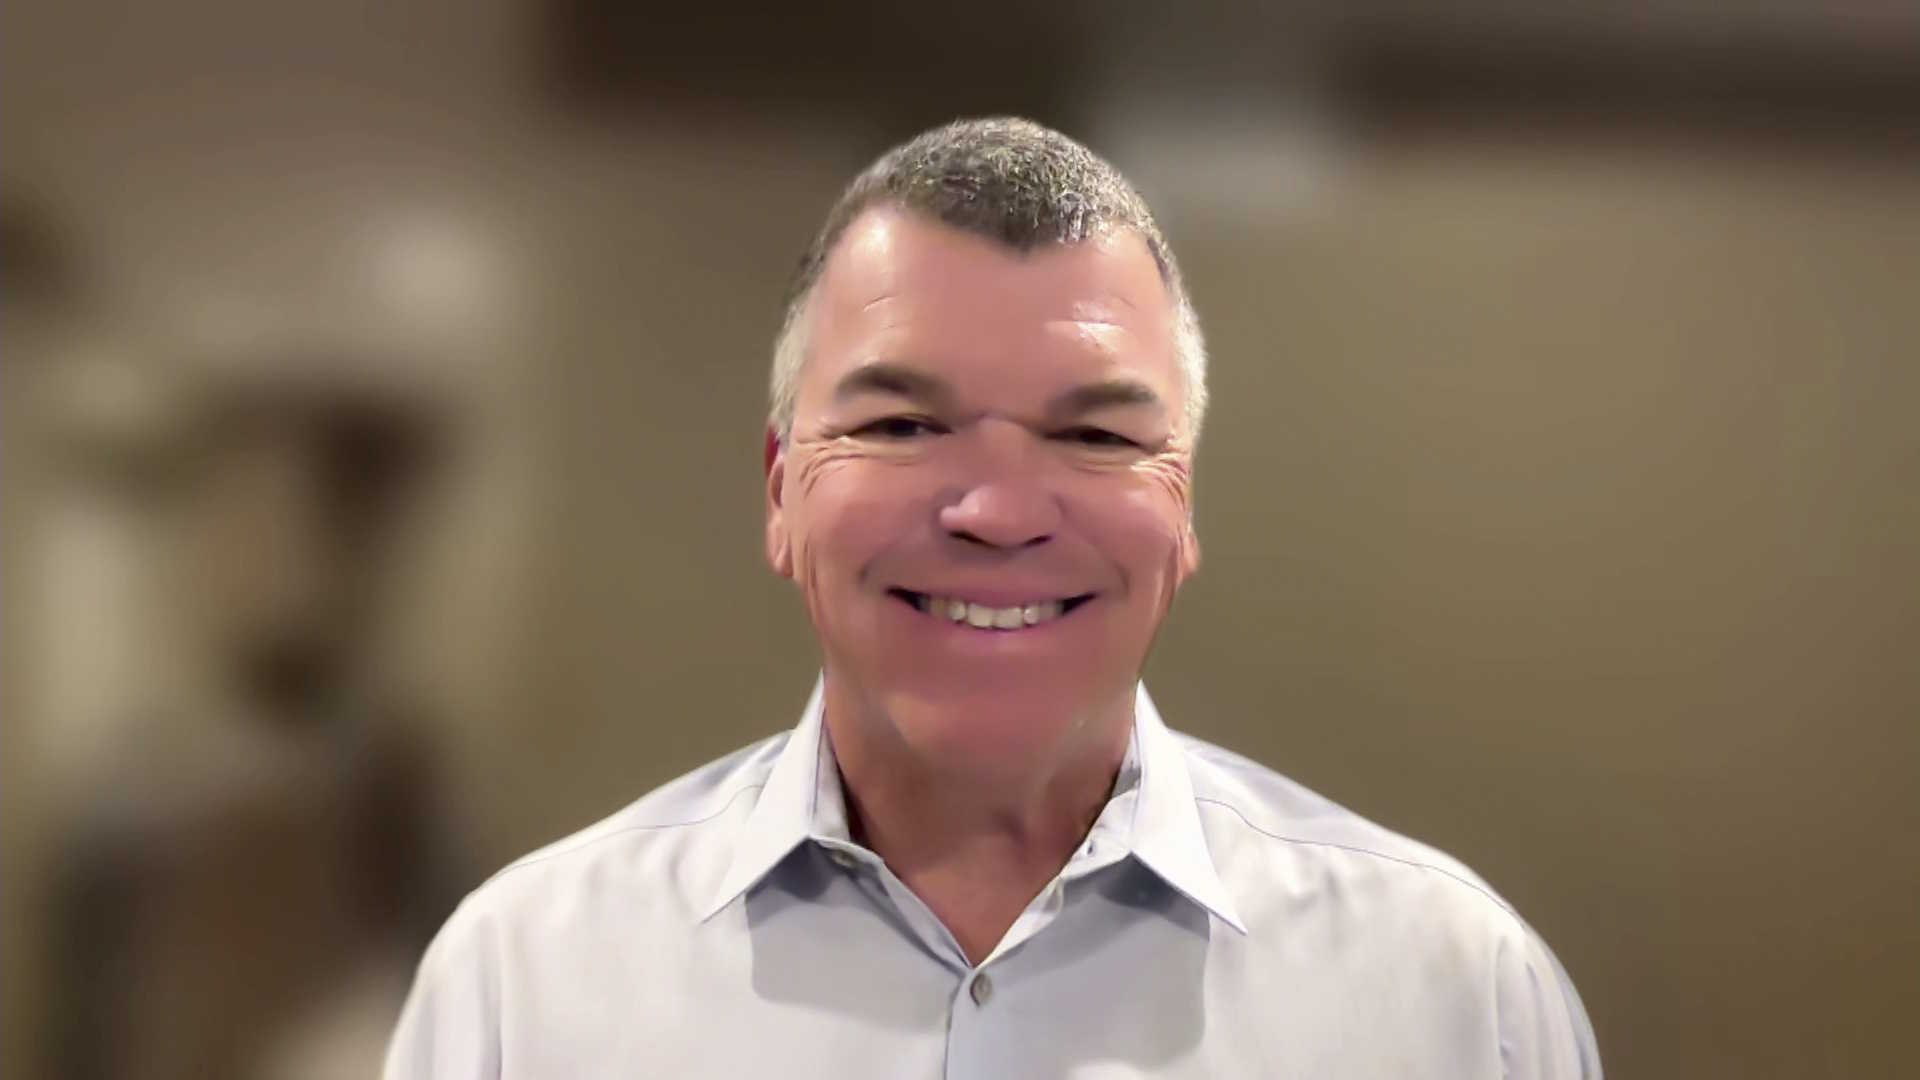
In an era of escalating AI cyberattacks, Oracle has emphasized the critical role of human oversight in AI security governance. Senior Vice President and Chief Information Security Officer Brennan Baybeck argued that robots, not humans, are the most powerful and potentially dangerous links in AI systems. To address this, Baybeck stressed the importance of human accountability alongside traditional security controls such as least privilege, authorization, network segmentation, and monitoring.
He highlighted three gaps in organizations' AI implementations: the lack of a solid foundational governance program for AI, the absence of basic security measures, and the misinterpretation of the shared security responsibility model between providers and customers. Baybeck also noted that AI can significantly enhance security teams' ability to create policies, standards, and assessment tools swiftly, making it essential for companies to leverage AI in governance program development.
Written by urgent.news from SiliconANGLE's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.