How we found 24 Android vulnerabilities using our open source AI security agent
A look at the targeted AI taskflows behind these findings, the critical Android bugs they uncovered, and how to run the same open-source agent on your own app. The post How we found 24 Android vulnerabilities using our open source AI security agent appeared first on The GitHub Blog .
In a recent development in the realm of AI-powered security, researchers have uncovered 24 vulnerabilities in Android applications using a tool known as the GitHub Security Lab Taskflow Agent. The taskflows, which are open source and created by the team, enable security researchers to automate, package, and share AI prompts and workflows that enhance their work efficiency.
The discovery of these vulnerabilities was made possible through the use of custom taskflow prompts that guide AI models, allowing them to focus on specific classes of vulnerabilities in Android applications. By splitting research into incremental steps, the LLM can find complex vulnerabilities more rapidly, and potentially identify ones that would have gone unnoticed otherwise.
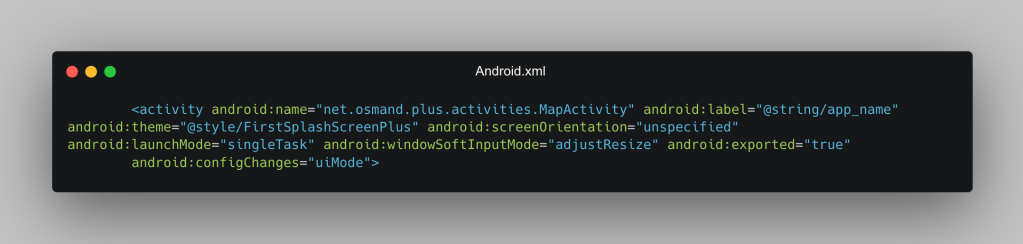
One of the vulnerabilities discovered involves a tracking mechanism in the OsmAnd third-party navigation app, which has over 10 million downloads. The taskflows identified a flaw in MapActivity, an exported activity that handles opening settings files and deeplinks within the app. This vulnerability enables malicious apps to send intents with arbitrary extras, which can be used to import settings undetected and track the user's location.
Written by urgent.news from GitHub Blog's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.