Dutch Police Arrest ‘Reformed’ Hacker in Shiny Hunters Investigation
Authorities in the Netherlands have arrested a 23-year-old convicted cybercriminal on suspicion of aiding in data thefts and extortions by the prolific hacker group ShinyHunters. In the days immediately following the suspect's arrest, remaining ShinyHunters members dramatically escalated their attacks, stealing highly sensitive data from the FBI and extorting the Russian ransomware group Cl0p.
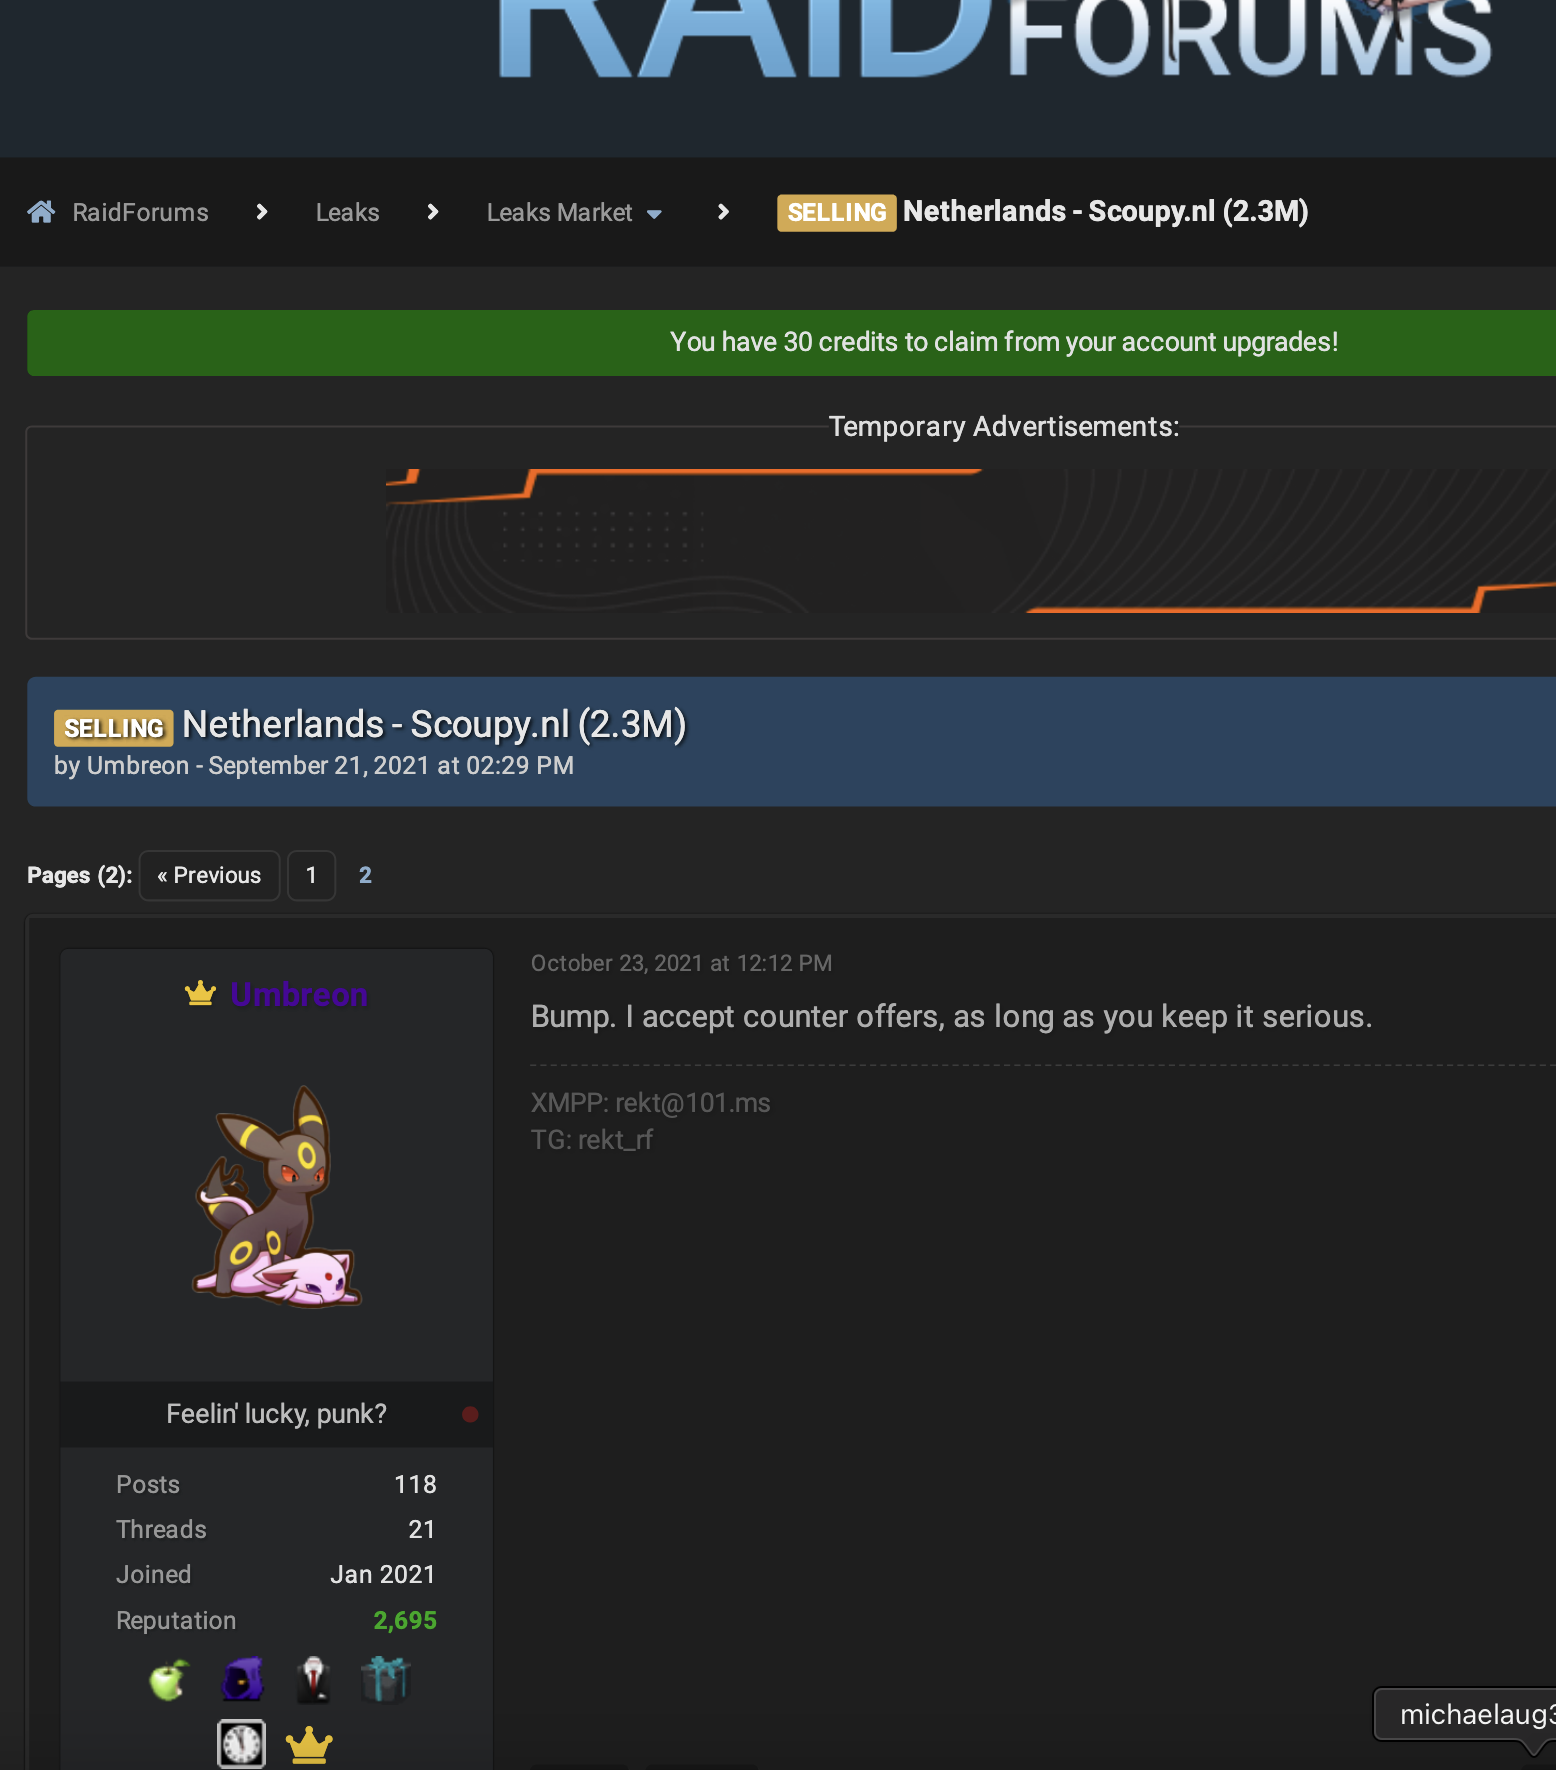
In the Netherlands, a 23-year-old former hacker named Pepijn van der Stap has been arrested on suspicion of aiding in data thefts and extortions by the hacker group ShinyHunters. Following his arrest, ShinyHunters members allegedly intensified their attacks, stealing sensitive data from the FBI and extorting the ransomware group Cl0p.
Van der Stap, convicted in 2023 for data thefts and extortions, admitted to his alter ego "Umbreon" selling a database containing 2.3 million Netherlands residents' information in September 2021. He claimed to have PTSD from childhood trauma and sought psychological help, but his release from prison in December 2025 was followed by a sudden cessation of communication.
Authorities have been seeking public assistance to identify a recorded phone call from February 2026 where a Dutch-speaking ShinyHunters member attempted to socially engineer a telecommunications provider. ShinyHunters claimed they supported their member emotionally, mentally, and financially, providing a criminal defense lawyer.
The group is also threatening further large-scale data thefts in the Netherlands, dismissing the Dutch police as incompetent and irrelevant.
Written by urgent.news from KrebsOnSecurity's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.