Boeing identifies 737 MAX software glitch that may prompt delays
The issue with the jet’s navigation system could increase pilot workload during landing and may delay the arrival of new narrowbody models.
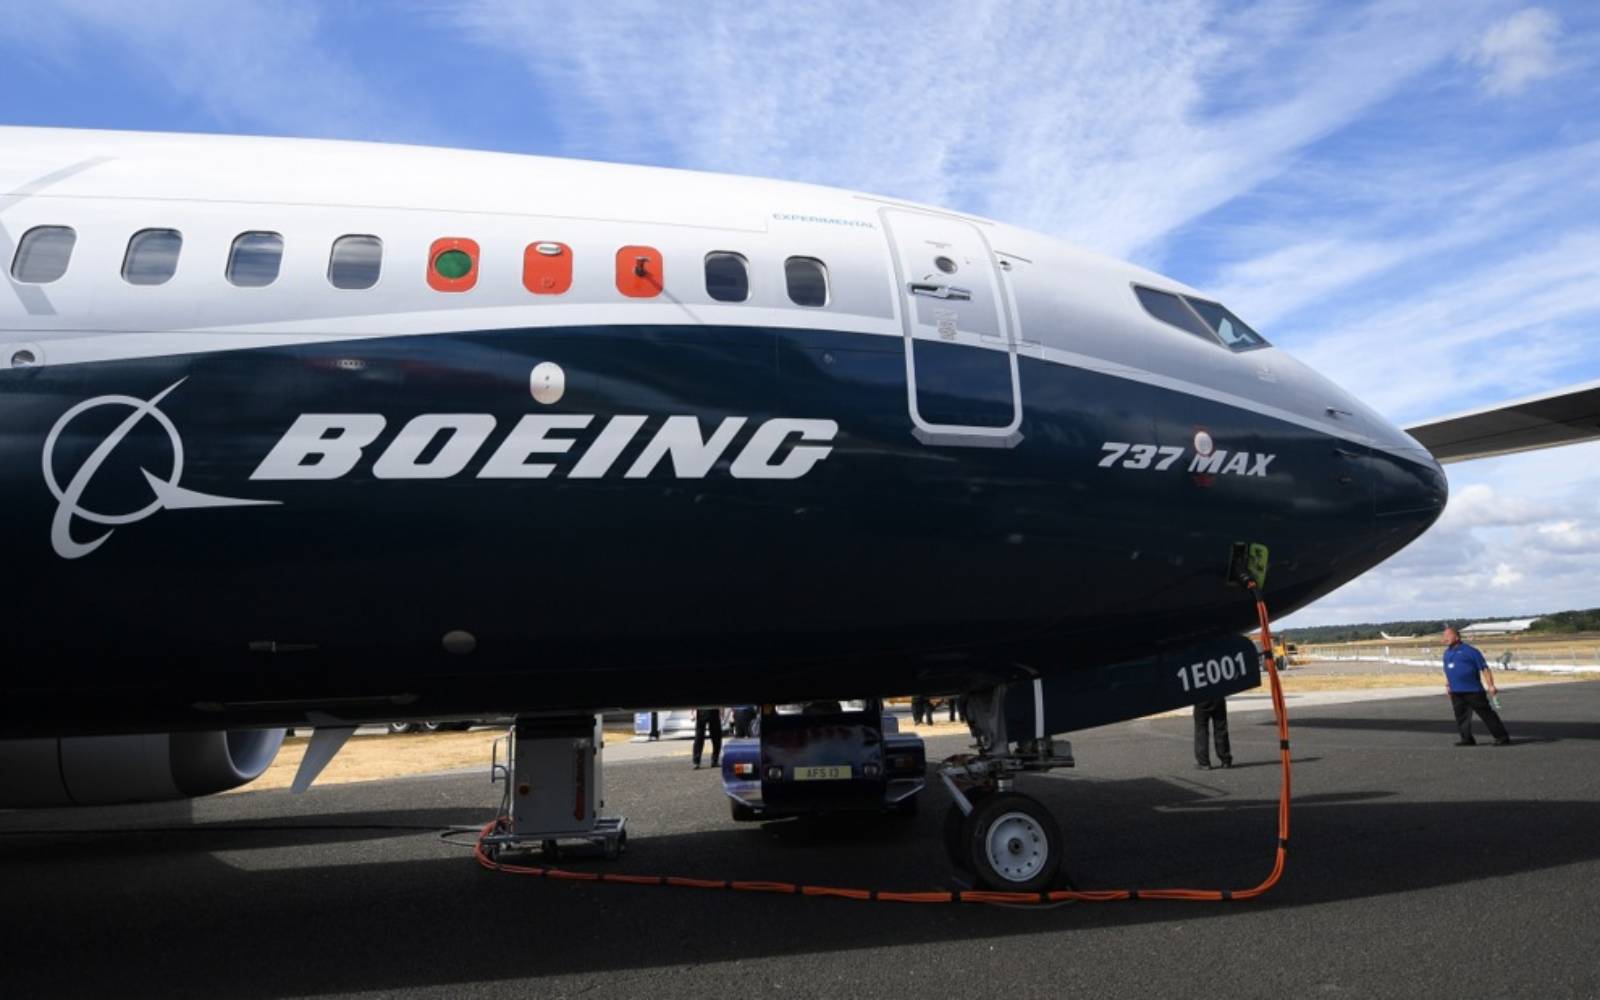
The US Federal Aviation Administration has assembled a review board to assess whether an issue with the 737 MAX jet's navigation system could pose a safety risk. Boeing confirmed on April 13, 2023, that a software glitch in the 737 MAX's navigation system could potentially increase pilot workload during landing, possibly causing delays in the delivery of the airline's latest narrowbody models.
The glitch arises when pilots may not have access to automated flight guidance during a specific landing scenario, a situation for which Boeing had previously provided guidance to operators. The company reiterated its commitment to reinforcing existing pilot procedures for safely handling such cases. The Federal Aviation Administration's review could potentially delay the certification of Boeing's new 737 MAX 10 model and complicate the introduction of the recently approved MAX 7.
The software glitch occurs when a pilot needs to abort a landing attempt, forcing the autopilot into a simpler level of pitch control automation, which increases the pilot's workload compared to the standard mode. The Wall Street Journal had earlier reported on the software glitch and its implications for Boeing's certification schedule.
Boeing aims to finalize a permanent fix for the issue initially planned for 2028, although the company is working to expedite this. Until a fix is implemented, a bulletin is being prepared for pilots operating the 737 MAX.
Written by urgent.news from Free Malaysia Today's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.