Urgent.News

What's breaking now, across thousands of outlets.

Tech

The Galaxy Z Fold 8 is exactly what I’ve wanted in a foldable, but I’m more excited for the Z Fold 9

The Galaxy Z Fold 8 is easily the closest I've come to pulling the trigger on a foldable. But I still can't do it.
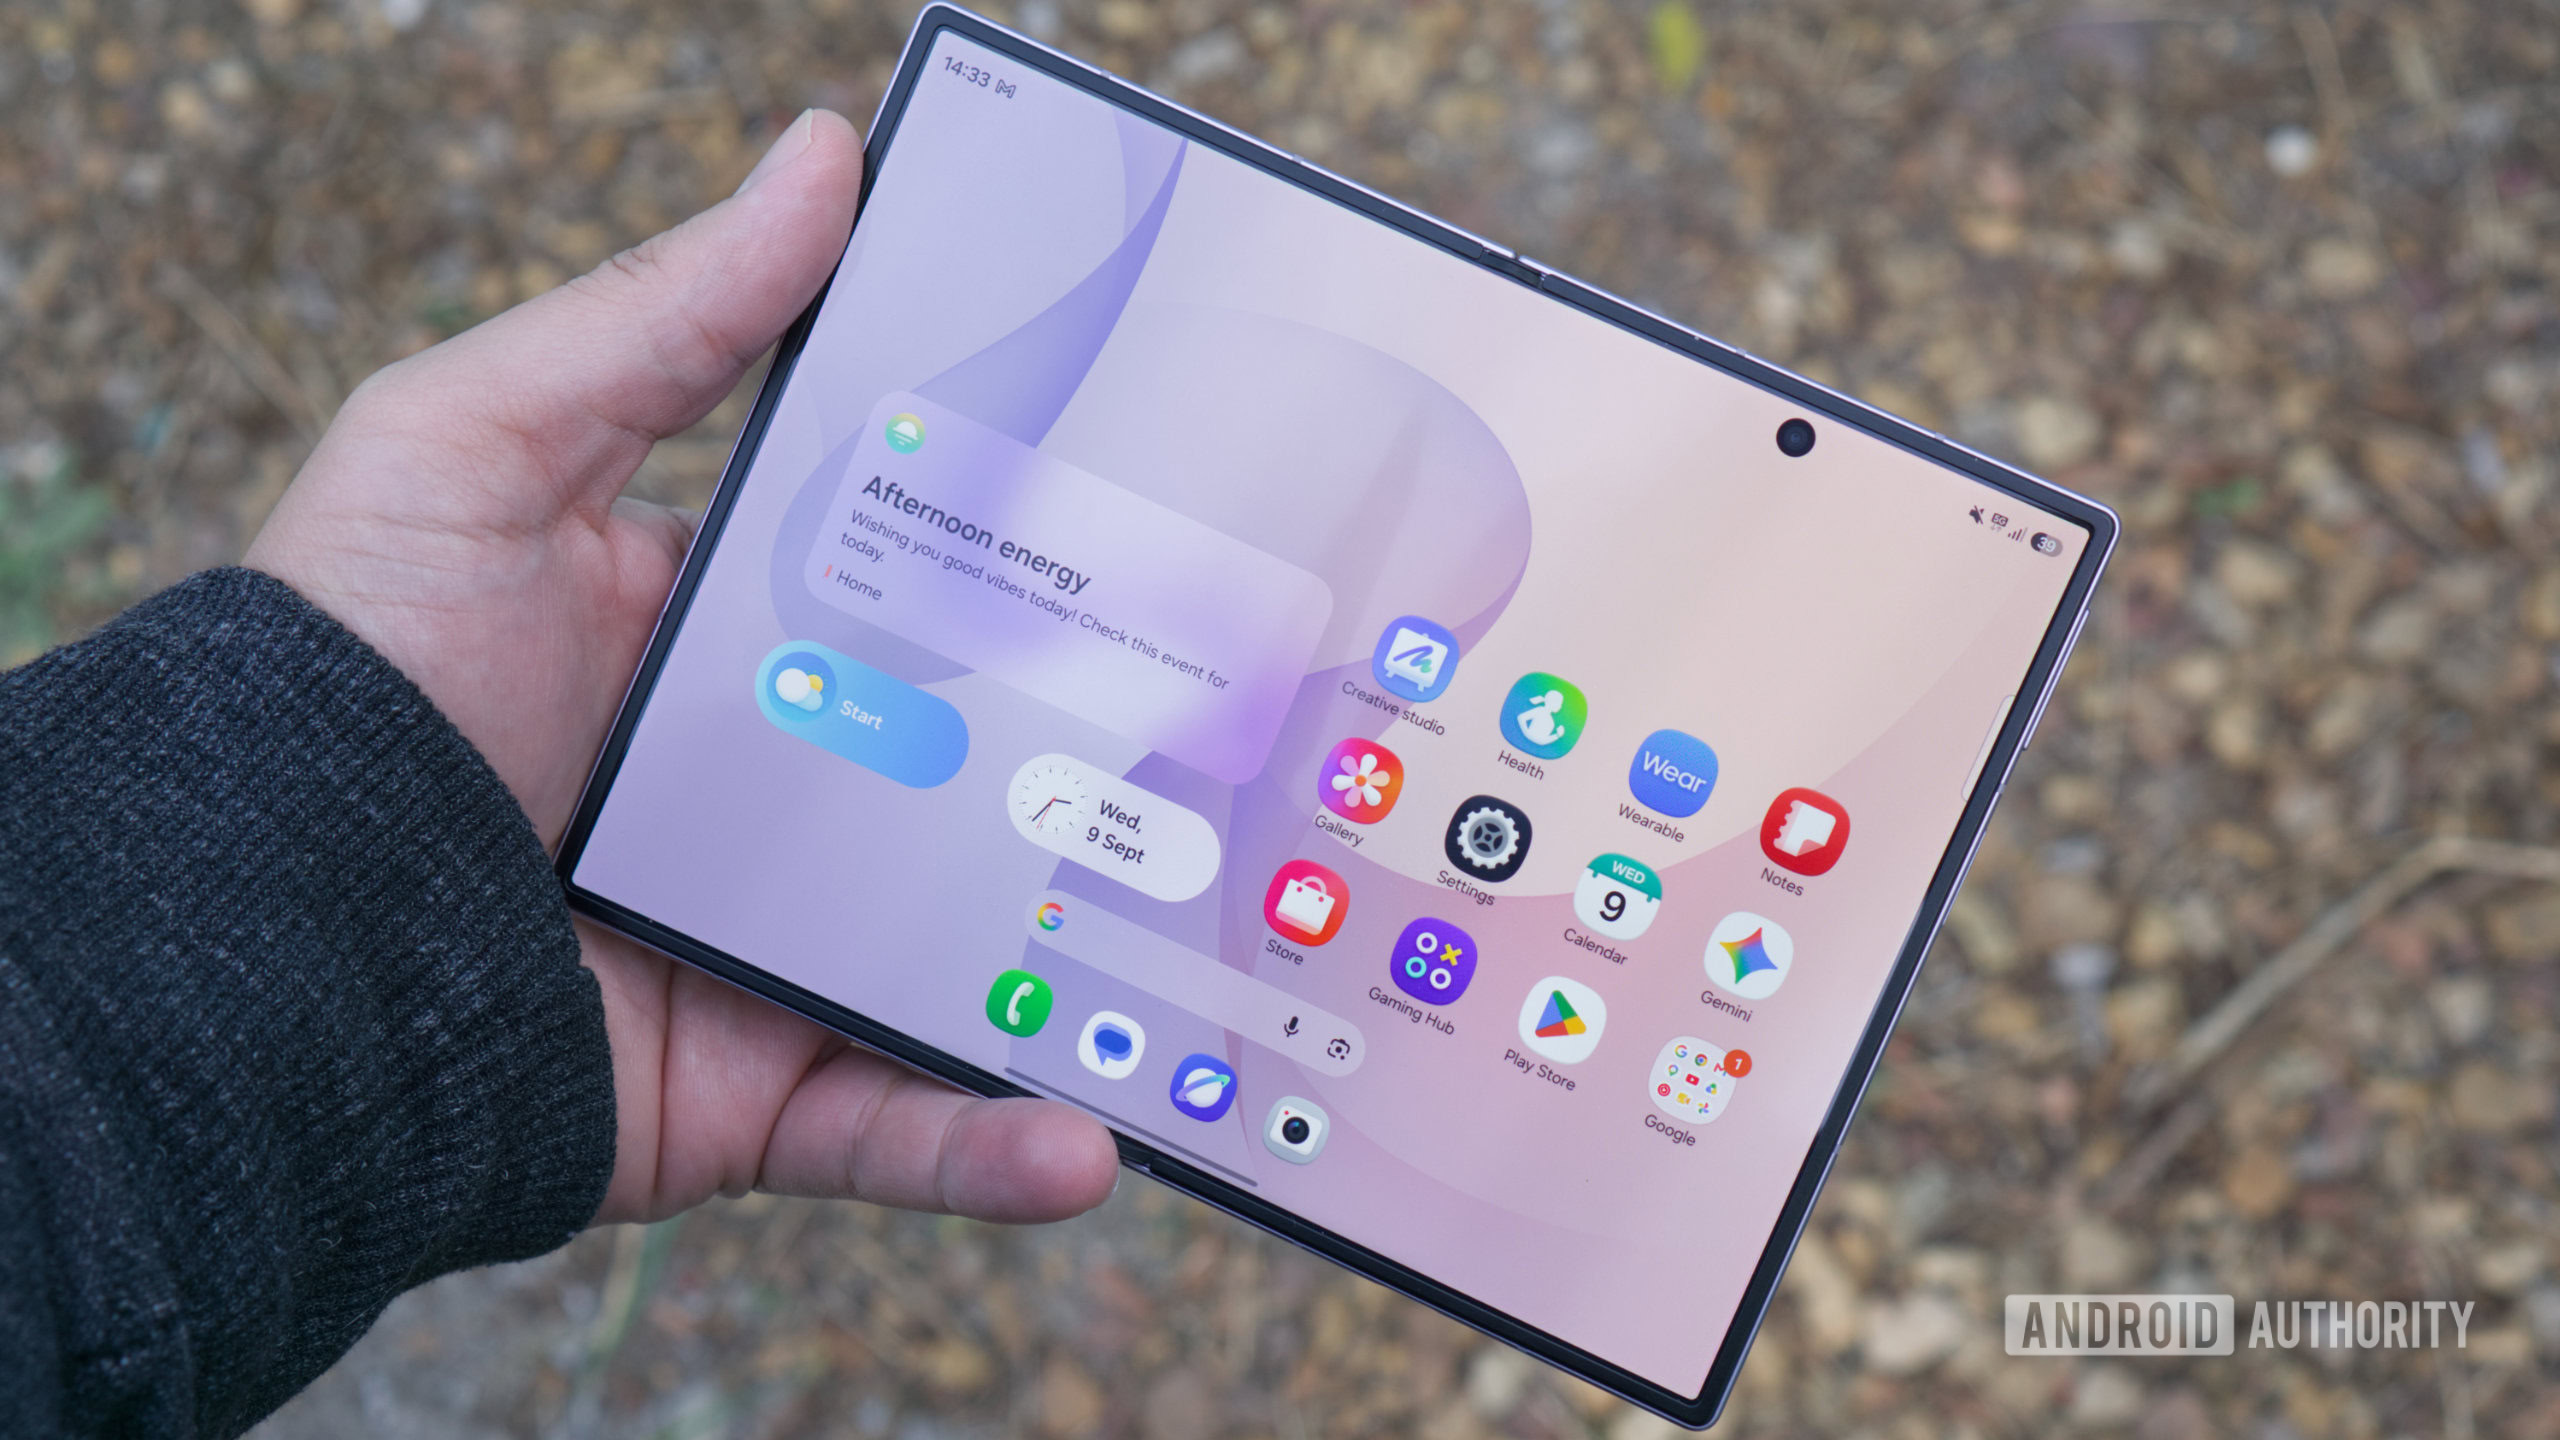
The Galaxy Z Fold 8 is exactly what I’ve wanted in a foldable, but I’m more excited for the Z Fold 9

Samsung’s Galaxy Z Fold 8 has been the subject of much attention following its unveiling at the company’s Unpacked event in July. This foldable device distinguishes itself with its short yet wide form factor, a departure from the previous Galaxy Folds and the Galaxy Z Fold 8 Ultra. While it isn’t the first wide foldable on the market, Samsung’s offering has gained popularity, especially as Apple prepares to enter the foldable market with its first-ever foldable device.

Despite the strong appeal of the Z Fold 8, the author of this review found themselves on the fence about pre-ordering the device, hinting at a possible anticipation for an even more advanced model in the future – the rumored Galaxy Z Fold 9.

Brief written by urgent.news from Android Authority's own syndicated text. Machine-written — may contain errors; check the original before relying on it.

Read the original at androidauthority.com →

More in Tech

A 5-minute SEO checklist for your homepage

A 5-minute SEO checklist for your homepage Your homepage is usually the page with the most links pointing at it, so it is the one search engines and social networks look at first.

  • Ensure only one H1 heading accurately describes the page using plain language
  • Craft a customized meta description to increase click-through rates
  • Verify presence of canonical URL and eliminate stray noindex tags

CVE-2026-66066: an image upload path that reads /proc/self/environ

CVE-2026-66066: an image upload path that reads /proc/self/environ The shortest way to describe CVE-2026-66066 is that a framework default turned an ordinary avatar upload into a file read primitive…

  • CVE-2026-66066 exploits image upload path in Ruby on Rails with Active Storage and libvips.
  • KindaRails2Shell vulnerability allows reading process environment and SECRETKEYBASE via HDF5 files.
  • Fix includes upgrading, setting Vips.blockuntrusted = true, and rotating SECRETKEYBASE.

More from Saturday 26 September →
