Urgent.News

What's breaking now, across thousands of outlets.

Tech

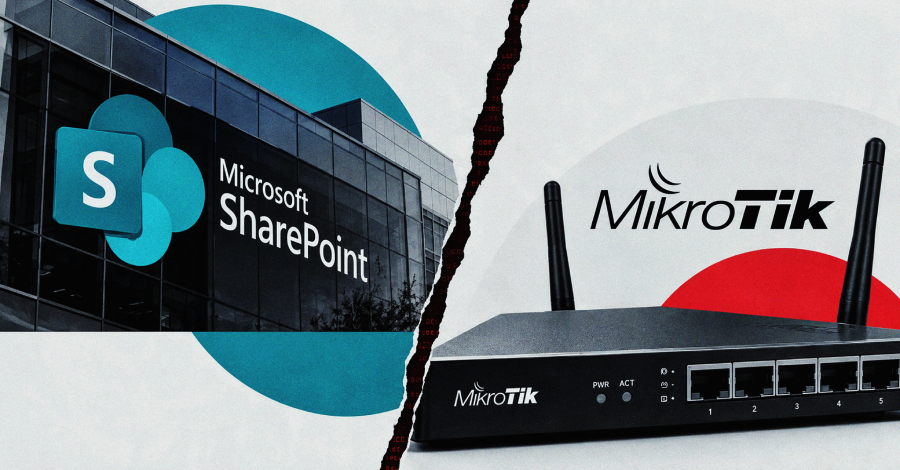
SharePoint RCE and MikroTik RouterOS Flaws Actively Exploited in the Wild

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Friday added two security flaws impacting Microsoft SharePoint and Mikrotik RouterOS to its Known Exploited Vulnerabilities (KEV) catalog, citing evidence of active exploitation. The vulnerabilities in question are as follows - CVE-2026-65660 (CVSS score: 8.8) - A code injection vulnerability in Microsoft Office SharePoint
SharePoint RCE and MikroTik RouterOS Flaws Actively Exploited in the Wild

We haven't written up this one. The Hacker News has the full story — the link below goes straight to it.
Read the original at thehackernews.com →

More in Tech

grok-bot-cli

Tested - working well - grok-bot-cli https://github.com/ScriptedAlchemy/grok-bot-cli

Building an i18n Pipeline That Doesn't Break Screen Readers: EAA Compliance for Devs

The European Accessibility Act (EAA) has been in force since 28 June 2025, and if you ship e-commerce, banking, ticketing or e-reader products into the EU, it applies to you.

  • European Accessibility Act (EAA) enforced June 28, 2025
  • Translated text accessibility often overlooked in engineering
  • Pipeline created to prevent accessibility compliance breakdown

Beyond boilerplate bots: Unified messaging architecture with wconnect

Building Telegram bots shouldn't require reinventing dispatch loops, attachment parsers, and connection pools. wconnect brings declarative, enterprise-grade messaging to Python.

  • Telegram bots simplified with declarative messaging in Python
  • In-memory streaming enables direct RAM processing of binary files
  • Open-source project available on GitHub and PyPI

More from Saturday 26 September →