Urgent.News

What's breaking now, across thousands of outlets.

Tech

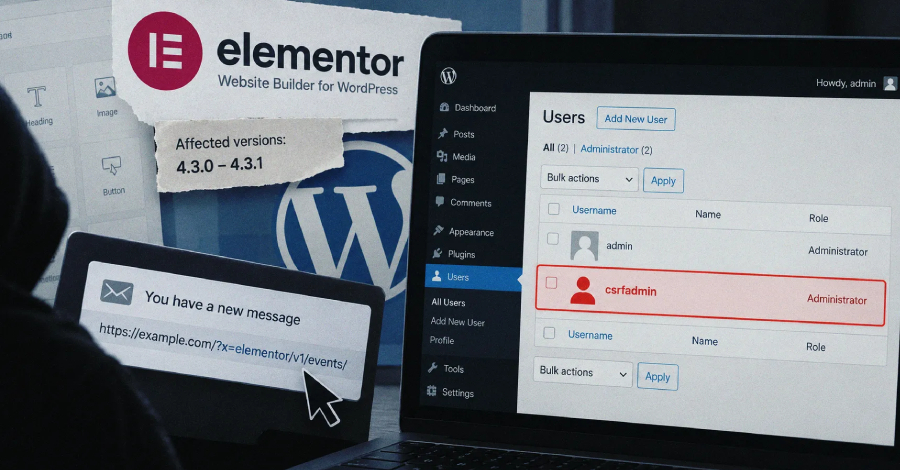
Elementor CSRF Flaw Lets Attackers Take Over Sites After Admin Clicks Crafted Link

Details have emerged about a high-severity security flaw in the Elementor Website Builder WordPress plugin that could be exploited by an unauthenticated attacker to create rogue administrator accounts and take control of a site. The cross-site request forgery (CSRF) vulnerability, which has yet to be assigned a CVE identifier, carries a CVSS score of 8.8 out of 10.0. It only affects versions
Elementor CSRF Flaw Lets Attackers Take Over Sites After Admin Clicks Crafted Link

We haven't written up this one. The Hacker News has the full story — the link below goes straight to it.
Read the original at thehackernews.com →

More in Tech

Cloudflare Details Its Migration from WordPress to EmDash

Cloudflare recently documented the migration of its main blog from WordPress to EmDash, the open source content management system developed internally.

  • Cloudflare migrated from WordPress to open-source CMS EmDash.
  • EmDash designed to enhance performance, handles up to 7,000 requests per second.
  • Migration achieved faster, more reliable site with consistent response profile.

Validating Image File Uploads in Ecommerce Chat Widgets to Prevent Security Risks

Introduction to Image File Verification in FastAPI In the world of ecommerce, chat widgets have become a vital tool for enhancing user engagement, particularly when it comes to product inquiries.

  • Two-tiered verification system combines header checks with binary signature validation
  • First layer rejects non-image file types based on Content-Type header
  • Second layer inspects file binary signatures using Python’s magic library

More from Saturday 26 September →