Renfe is investigating a cyberattack linked to Adif systems that exposed basic user data.
The company assures that the attackers were only able to access names and email addresses and that there are no indications of a leak of banking data or of an impact on the rail service.
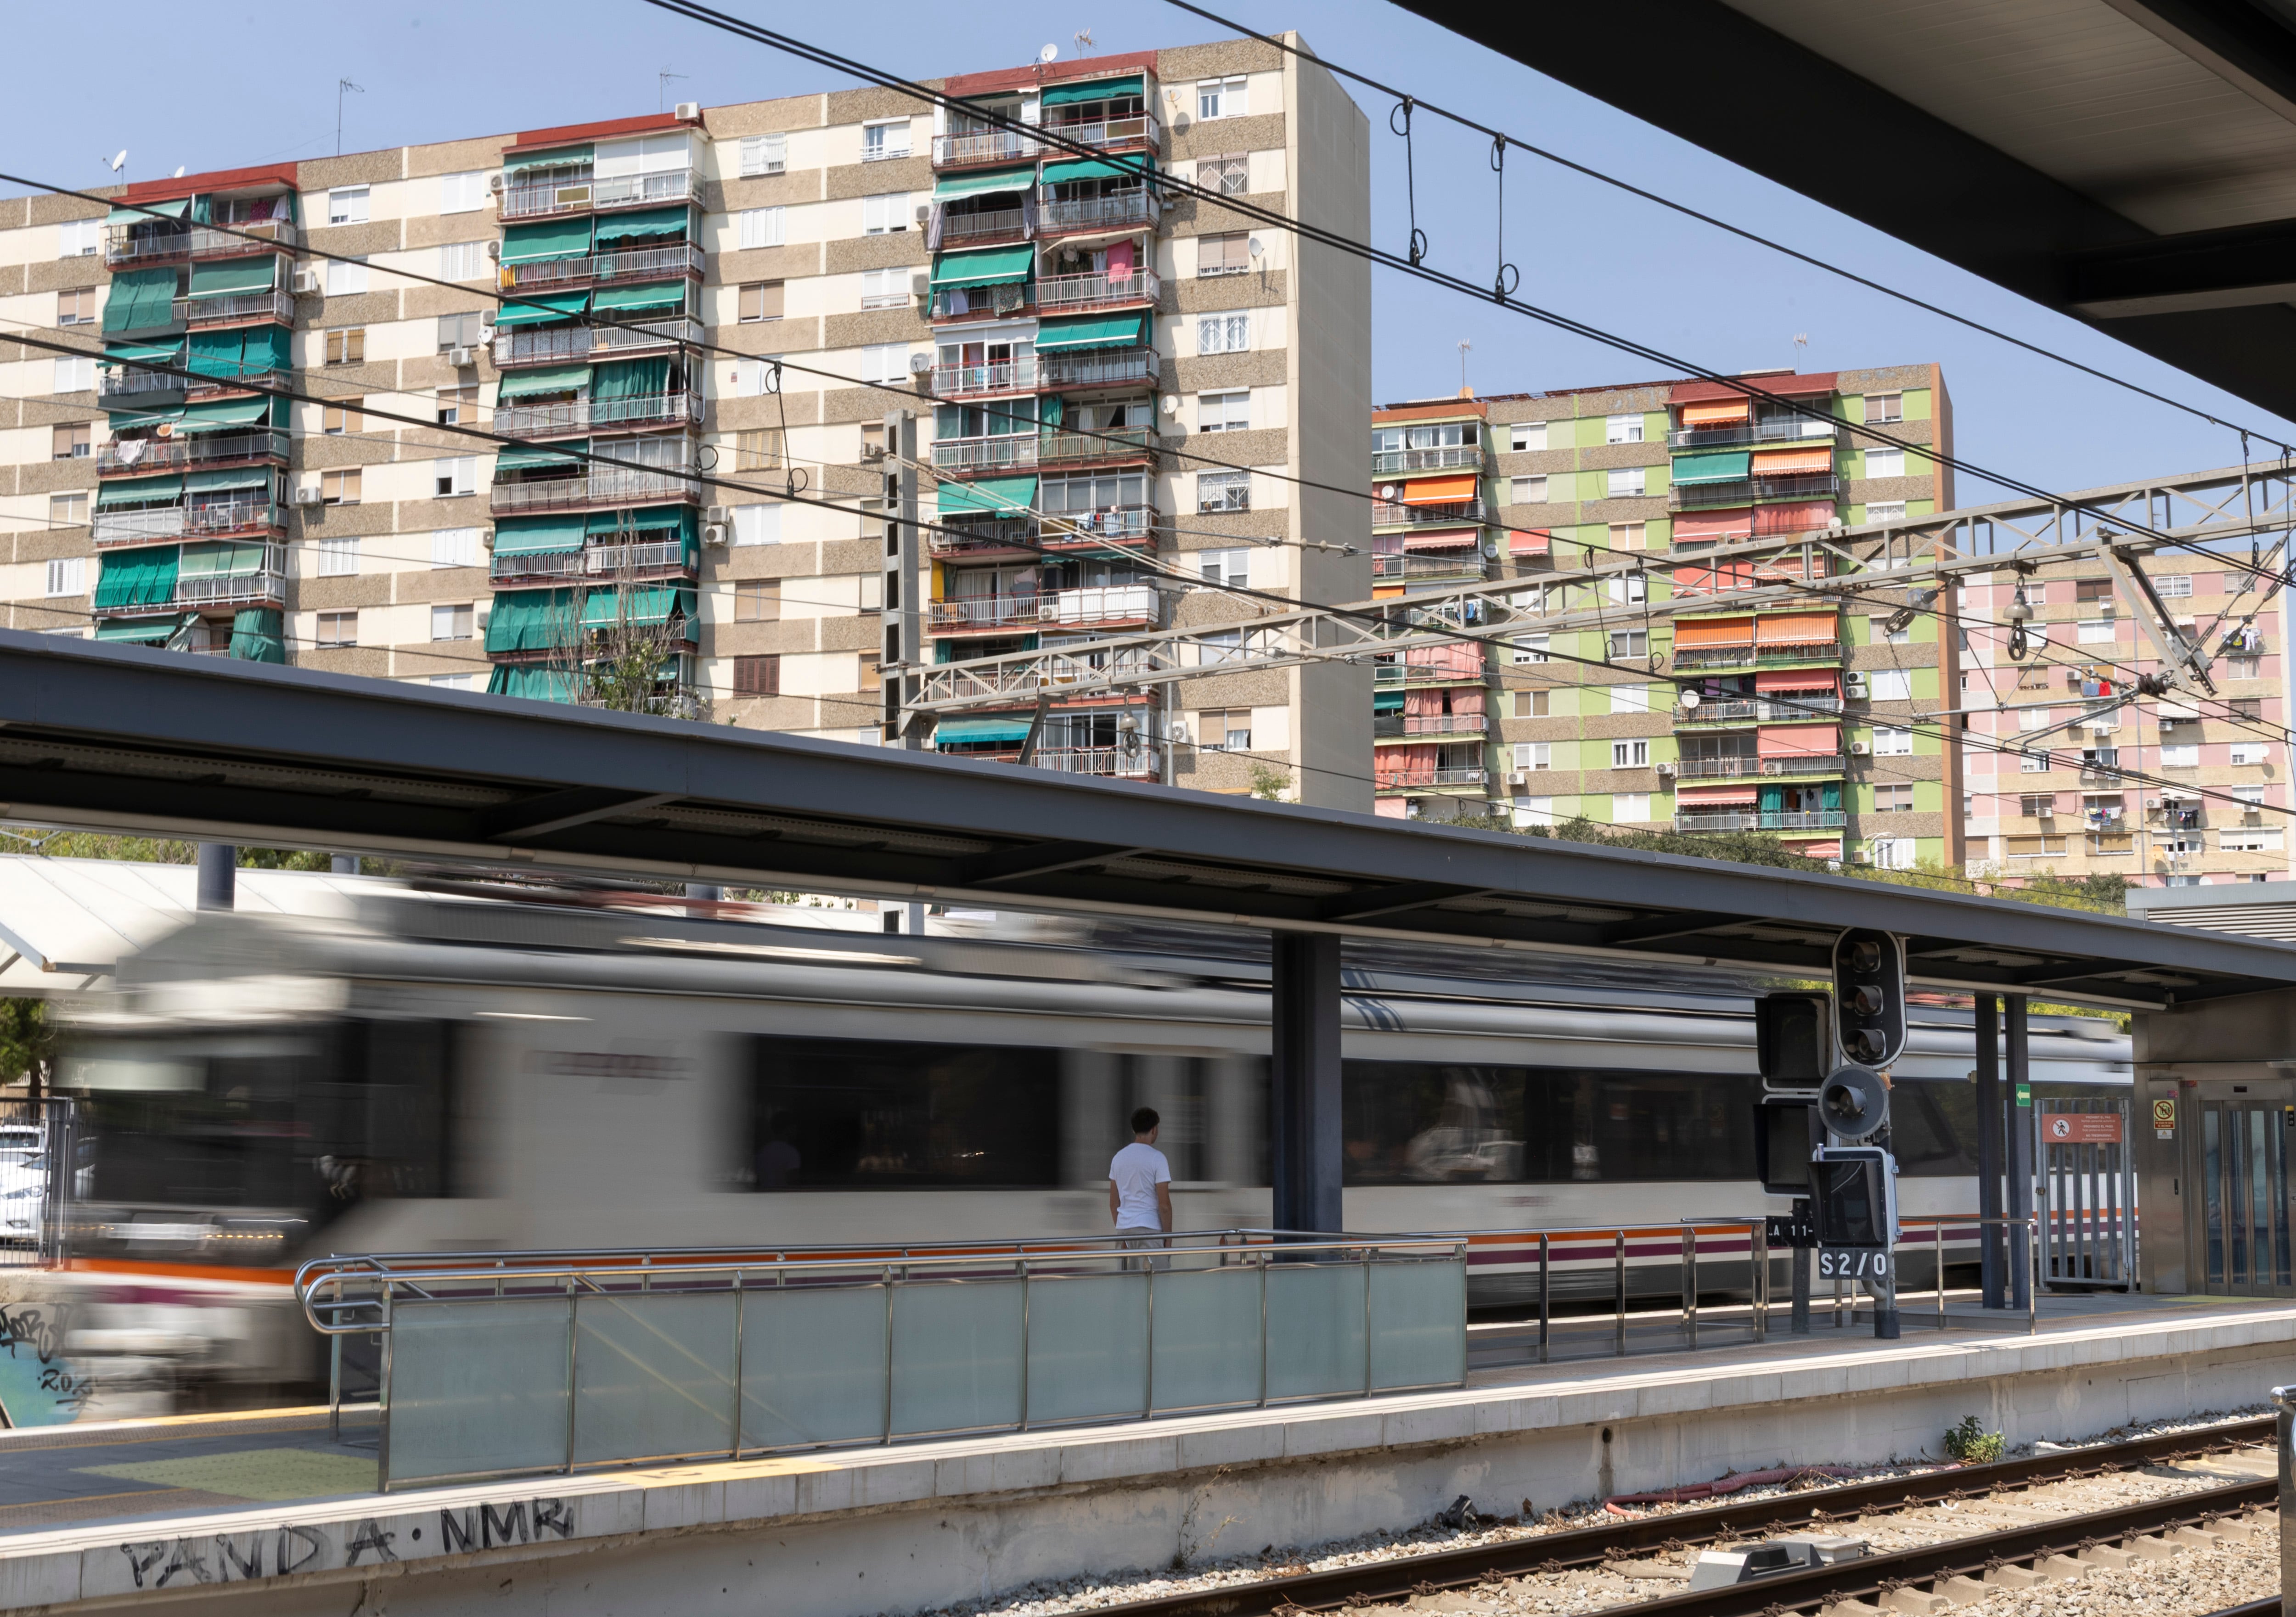
Renfe, a Spanish public railway company, has experienced a cybersecurity incident that originated from previously compromised servers of Adif, the country's railway infrastructure administrator. The incident did not affect train circulation or the railway service, but it did involve potential unauthorized access to limited user information, including names and email addresses.
Renfe states that there is no evidence that sensitive information, such as banking or financial data, was accessed or publicly disclosed. The company, along with Adif, is investigating the incident and collaborating with cybersecurity specialists and authorities.
Written by urgent.news from El Pais Economia's report — not a translation of it. Machine-written — may contain errors; check the original before relying on it.