Accenture leverages Oracle’s Deep Data Security for database-driven trust boundaries
Oracle Corp.’s Deep Data Security offers a basic premise on enterprise security: When the application layer is an AI agent, the trust boundary must move somewhere else. The trust boundary can be relocated to the database, and Roger Cornejo (pictured), technology innovation principal director of gen AI/AI at Accenture Enkitec Group, has published research results […] The post Accenture leverages…
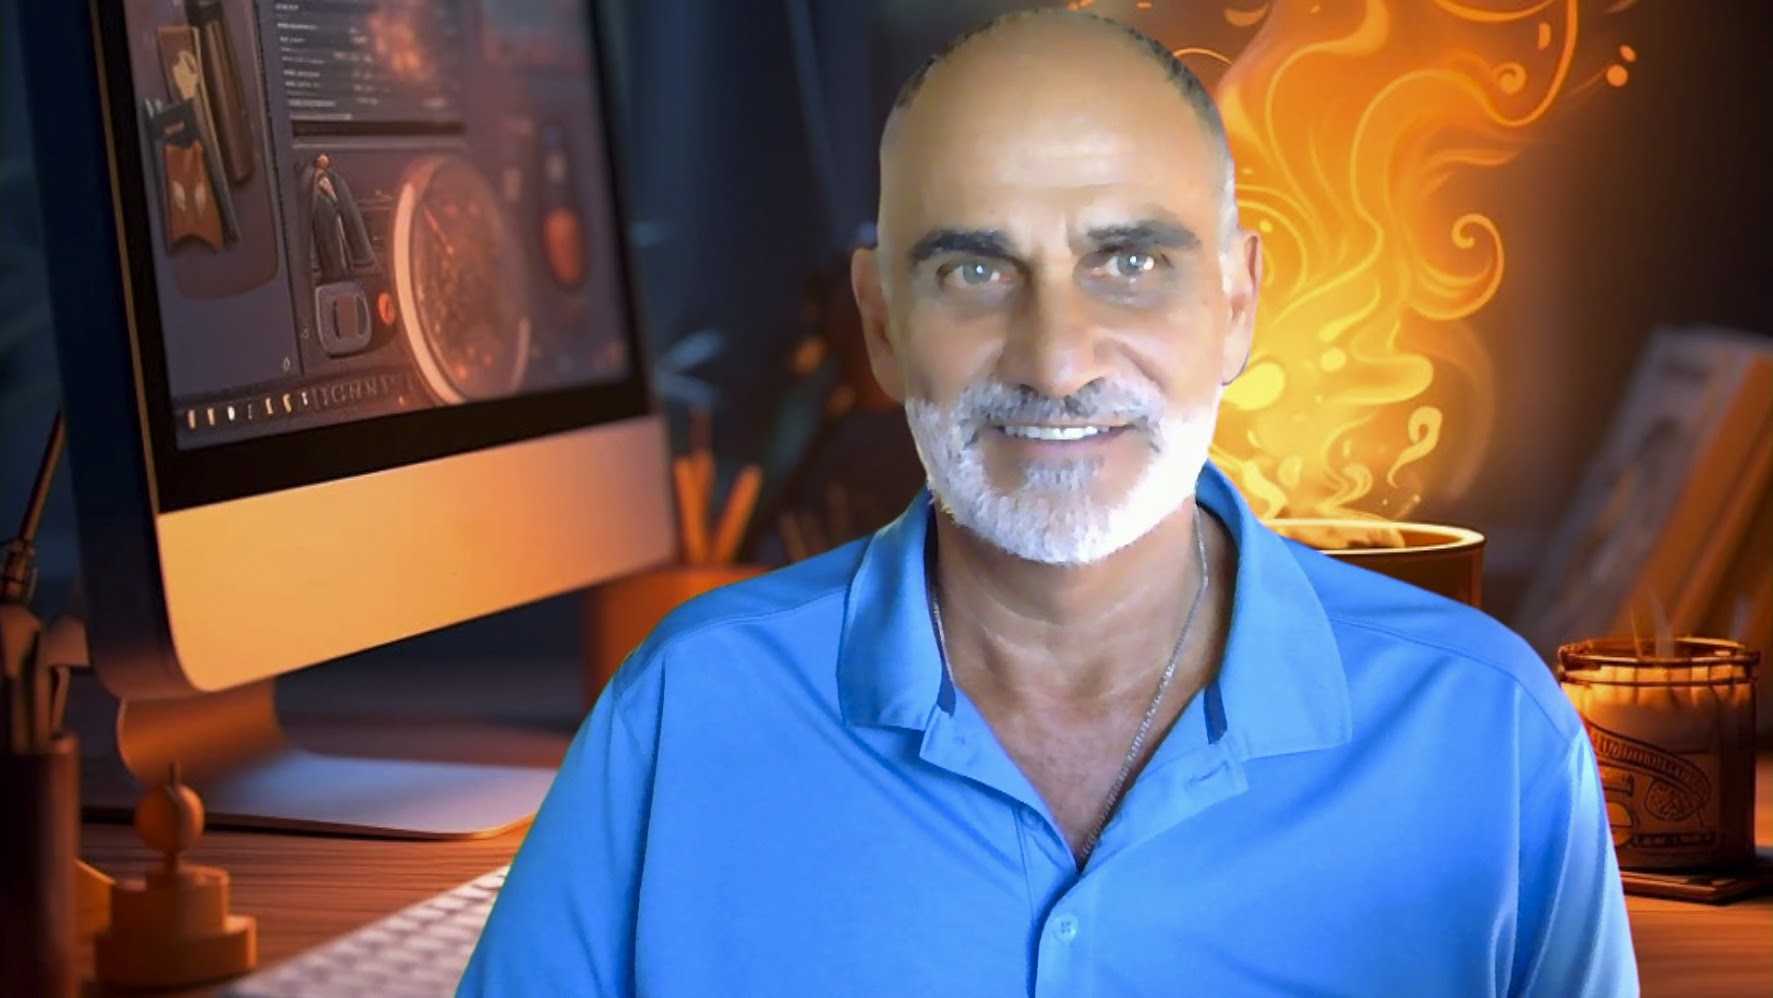
Oracle's Deep Data Security enables enterprise security by relocating the trust boundary to the database when the application layer is an AI agent. Accenture's technology innovation principal director of gen AI/AI, Roger Cornejo, has published research showing how this works with Oracle's Deep Data Security. Cornejo and his team developed an application that leverages Oracle's security solution, allowing the database to enforce access policies regardless of the Structured Query Language used by the agent.
Accenture's Model Context Protocol server provides AI agents with access to a large repository of documents, with different authorization levels for each agent. Oracle's solution implements end-user-specific privacy rules inside the database. In Cornejo's work with Accenture, Deep Data Security is used to define boundaries in SQL for each agent, ensuring robust security for all queries.
The application has been tested to scale to 300 simultaneous queries, with most results returned in 15 seconds or less.
Written by urgent.news from SiliconANGLE's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.
This story
This is one outlet's version. Read the fullest account.
- Oracle shifts agent controls toward data-layer security siliconangle.com