Exploit Released for Unpatched Ubuntu Linux Flaw Enabling Host-Root Container Escape
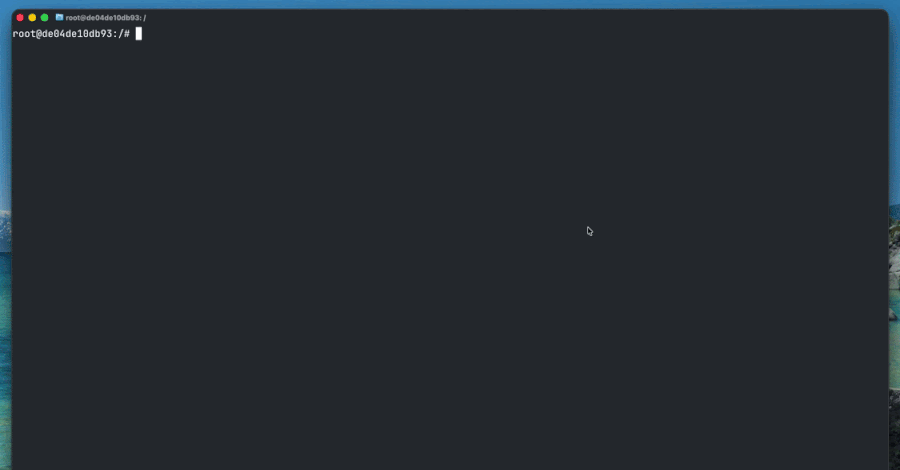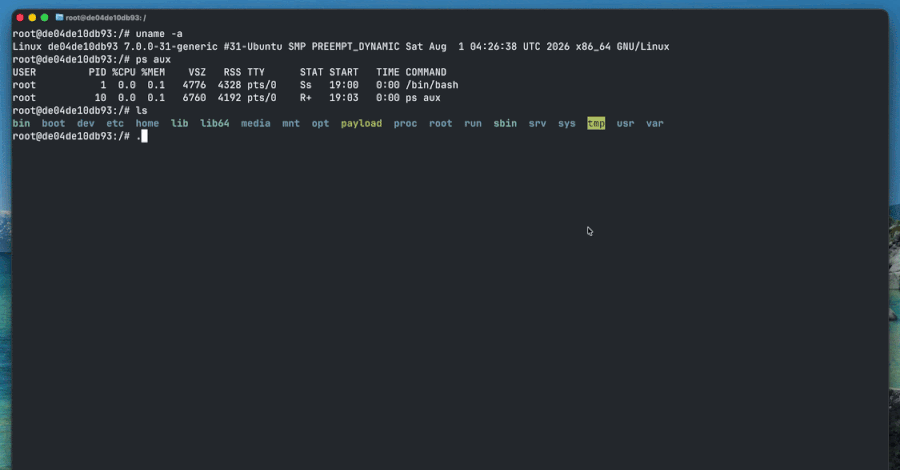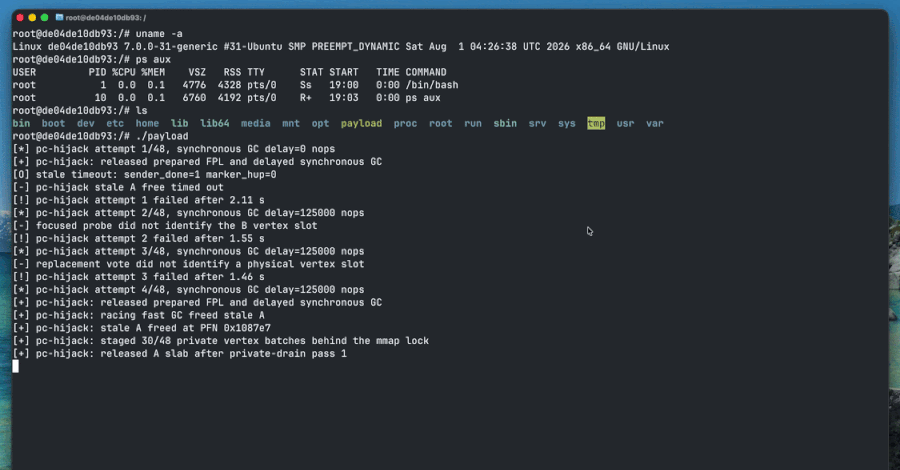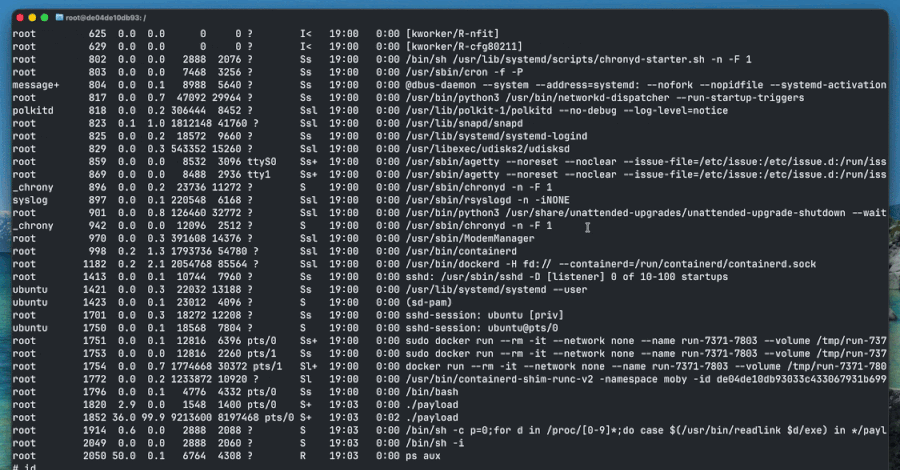
A use-after-free in the Linux kernel's AF_UNIX socket subsystem can be used to escape a container and gain root on the host, security firm DepthFirst said in research published September 22. The flaw, tracked as CVE-2026-80521 (CVSS score: 7.8), was fixed upstream on August 6, but Ubuntu has not shipped the patch for its 26.04, 24.04, or 22.04 LTS releases. DepthFirst
We haven't written up this one. The Hacker News has the full story — the link below goes straight to it.