Critical Next.js ImageResponse Flaw Can Lead to Server Code Execution via Crafted SVG Input
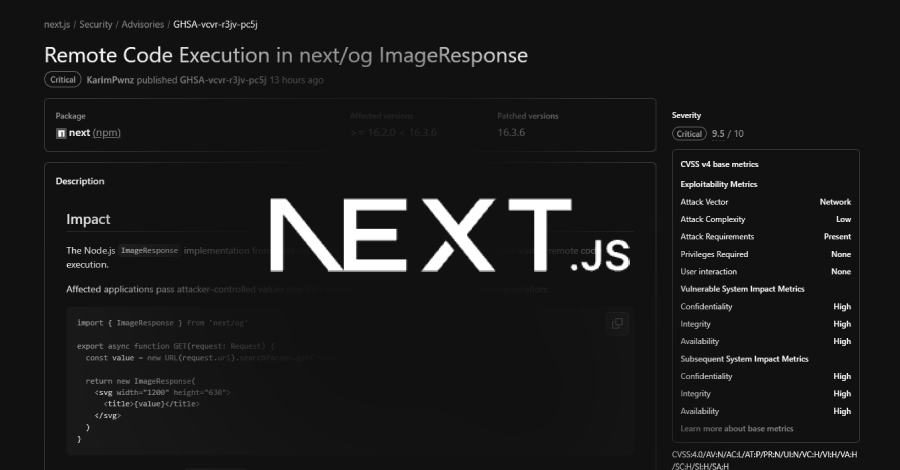
A new security vulnerability in Next.js could allow attackers to run code on a server via ImageResponse, the feature that generates Open Graph and other social preview images, Vercel said. The risk applies when an app puts values an attacker controls, such as text read from the request URL, into the image. Vercel, which develops Next.js, fixed the flaw on September 22 in version
We haven't written up this one. The Hacker News has the full story — the link below goes straight to it.
This story
This is one outlet's version. Read the fullest account.