WordPress Comment2Shell Flaw Can Turn Anonymous Comment XSS Into RCE via Admin Session
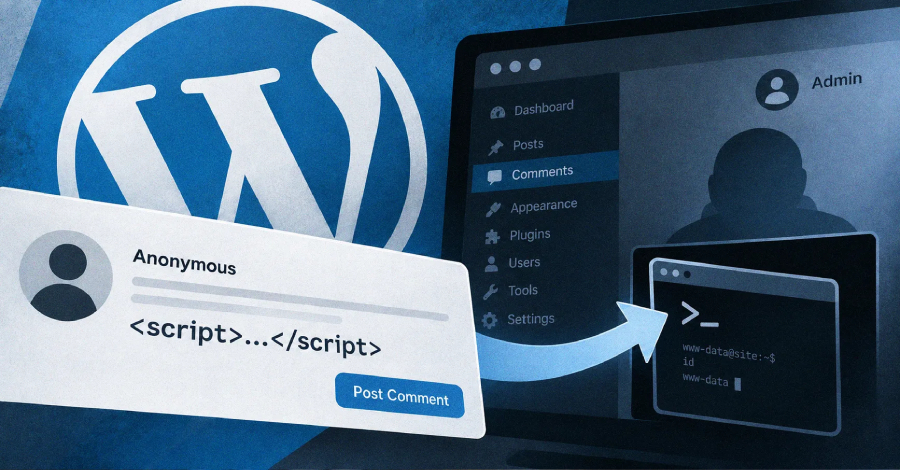
A new flaw in WordPress core let an anonymous visitor leave a comment that planted a hidden script on the page. If a logged-in administrator later opened that page, the script could run code on the site's server. WordPress fixed the flaw, tracked as CVE-2026-93485 and dubbed "Comment2Shell," on September 17 in version 7.1.1 and told site owners to update right away. There is
We haven't written up this one. The Hacker News has the full story — the link below goes straight to it.