Why Kubernetes RBAC Misconfigurations Are the Easiest Privilege Escalation You’ll Ever Find
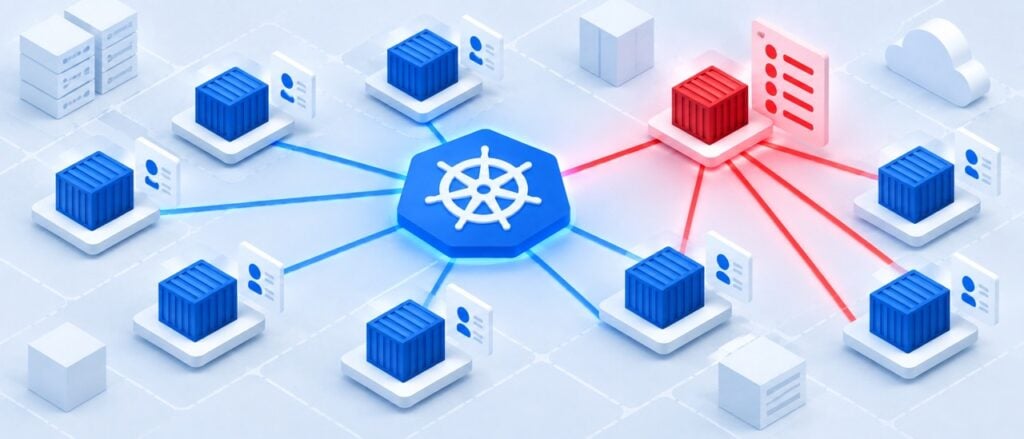
Ask any penetration tester which part of a Kubernetes assessment reliably produces a finding, and RBAC comes up almost every time. Not because Kubernetes’ permission model is poorly designed — it’s genuinely thorough — but because it’s flexible enough that teams misconfigure it in the same handful of ways, over The post Why Kubernetes RBAC Misconfigurations Are the Easiest Privilege Escalation…
We haven't written up this one. Container Journal has the full story — the link below goes straight to it.