AWS ramps up security tools amid growing AI risks
As AI moves rapidly from experimentation into production Amazon Web Services is expanding its security portfolio to help businesses manage emerging risks while scaling AI capabilities
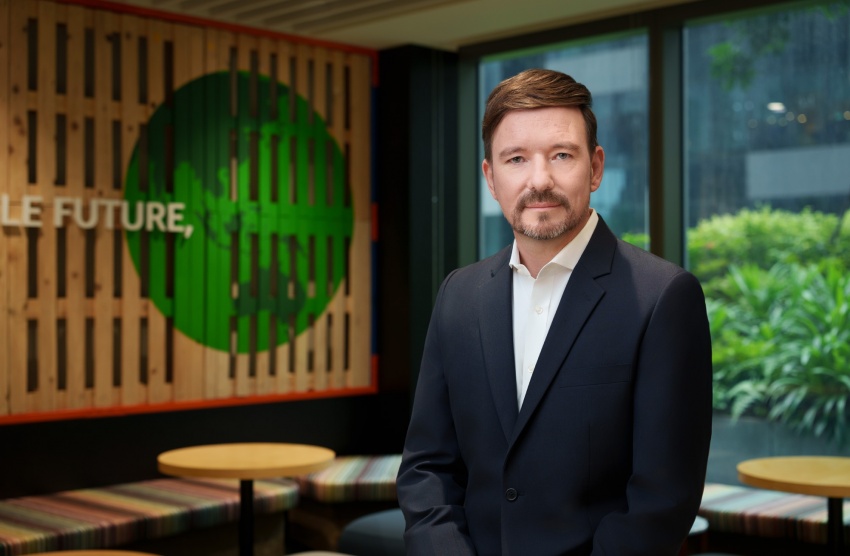
Amazon Web Services (AWS) is bolstering its security tools in response to increasing concerns over artificial intelligence (AI) risks. At a regional briefing, AWS VP Bryce Boland emphasized that 13% of organizations using AI have already faced breaches, with 97% of these incidents attributed to weaknesses in AI access controls. Boland explained that enterprises are allocating 10-12% of their AI budgets to security, a figure expected to rise as more AI is integrated into production systems.
AI agents can autonomously execute transactions, interact with customers, and access sensitive data, making any vulnerabilities a direct business risk.
The regulatory scrutiny surrounding AI is intensifying, with governments across the region imposing new obligations on AI-powered systems. Boland noted that AI security is no longer just an IT issue; when an agent can move money or access customer data, securing it becomes a board-level business priority.
AI brings both defense and attack capabilities, with attackers able to find vulnerabilities much faster than before. In 2018, it took around 2.3 years to find a vulnerability, while today it can be done within just 10 hours. The number of Common Vulnerabilities and Exposures (CVEs) reported has more than doubled this year, increasing from about 5,000 CVEs per month in Q1 to about 10,000 CVEs per month in Q3.
Most organizations struggle with patching speed, but AI models are making vulnerability detection easier. The three key differences impacting enterprise customers are vulnerability overload, regulatory compliance, and risk management. Vulnerability overload means that when a vulnerability is announced, it must be patched, and if patching is not automated, organizations face a scaling problem and a significant increase in the number of patches they must deal with.
Regulatory compliance is evolving rapidly, with frameworks like CSA, NIST, and OWASP continuously revising their guidance. Risk management is also challenging, as most protocols are designed for vulnerabilities and exploits patched at human speed, but the scale and speed of AI threats require new risk management approaches.
Written by urgent.news from Vietnam Investment Review's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.