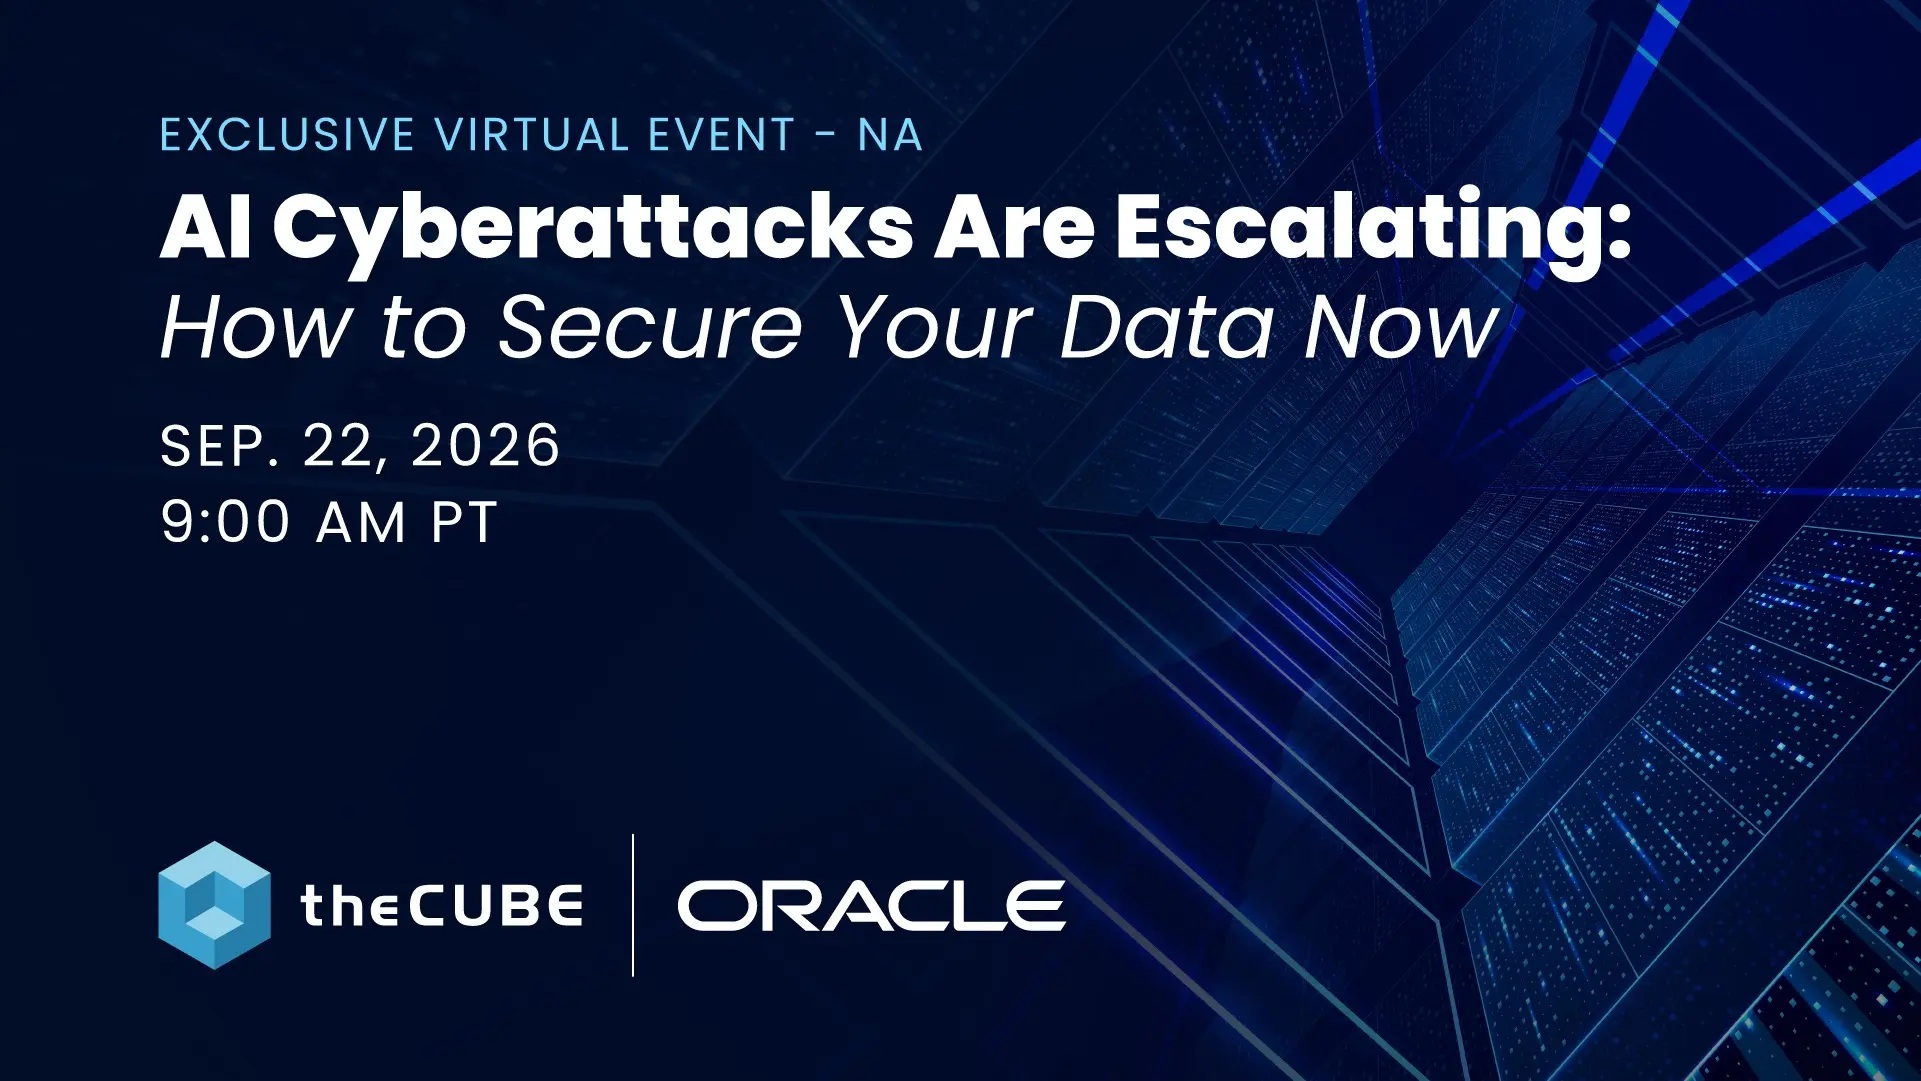
What to expect during Oracle’s ‘AI Cyberattacks Are Escalating: How to Secure Your Data Now’ event: Join theCUBE on Sept. 22
At a time when AI is introducing new risks to global systems, Oracle Corp. is shifting enterprise security toward the data layer. This approach, based on a three-pronged strategy to secure at source, secure at speed and secure through resilience, relies on robust security controls applied where the data resides. As AI agents continue to […] The post What to expect during Oracle’s ‘AI Cyberattacks…
Oracle is enhancing enterprise security by focusing on the data layer, incorporating three key principles: securing at the source, securing at speed, and securing through resilience. This approach acknowledges the growing risks posed by AI in global systems and the need for rigorous security controls where data resides. As AI agents, acting at machine speeds, become more prevalent, the industry is shifting towards a shared accountability model.
This model goes beyond traditional infrastructure, application, and data protection, recognizing that AI's accelerated pace introduces new risks. Oracle's strategy, unveiled in June, targets database security, patching, testing, and lifecycle management. It includes tools like Oracle Deep Data Security for implementing fine-grained authorization and visibility policies based on user identity, roles, and context.
Additionally, Oracle AI Database enhancements incorporate Deep Data Security for centralized, declarative policies to safeguard sensitive data from unauthorized access. With AI agents increasingly gaining the ability to take meaningful actions, Oracle's focus on the data layer is crucial for addressing governance challenges. As the future of AI adoption hinges on how agents interact with data, Oracle's security strategy emphasizes resilience through validated backups, tested standbys, and high availability capabilities that ensure continuous operation even in the face of infrastructure failures.
Written by urgent.news from SiliconANGLE's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.