Urgent.News

What's breaking now, across thousands of outlets.

Tech

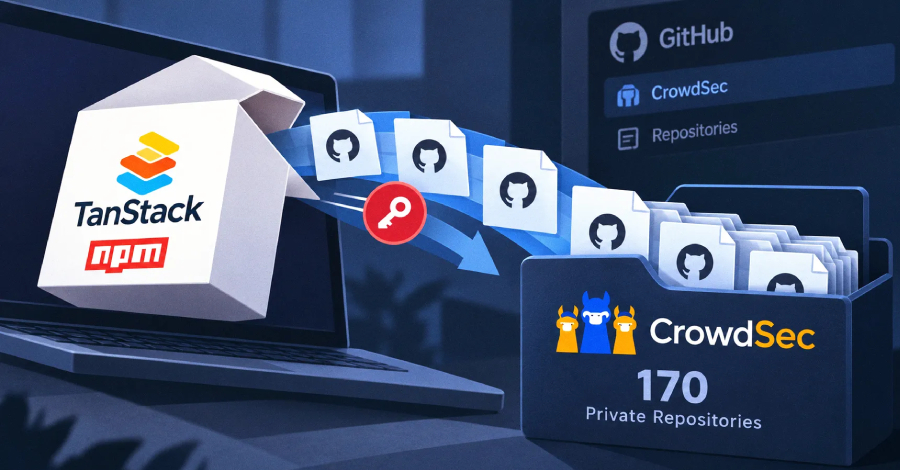
CrowdSec Says TanStack npm Attack Led to Copy of 170 Private GitHub Repositories

An attacker copied about 170 of CrowdSec's private GitHub repositories on May 22 using the account of an employee who had just left, CrowdSec said on September 18. The French security company had kept his GitHub access open. CrowdSec says his laptop was compromised in May's supply chain attack on TanStack, in which malicious versions of TanStack's npm packages stole credentials from
CrowdSec Says TanStack npm Attack Led to Copy of 170 Private GitHub Repositories

We haven't written up this one. The Hacker News has the full story — the link below goes straight to it.

Read the original at thehackernews.com →

More in Tech

Your OpenAPI spec is a contract. Nobody is checking it. I built a CLI that detects spec↔code drift with zero dependencies.

"The generated client keeps calling DELETE /items/{id}." "The server returns 405 Method Not Allowed." An OpenAPI spec is not just documentation.

  • oas-drift CLI tool detects spec↔code drift between OpenAPI spec and Python codebase
  • Tool identifies three types of drift: spec-only, code-only, and method mismatches
  • Lightweight implementation using only Python's standard library

More from Saturday 19 September →