Urgent.News

What's breaking now, across thousands of outlets.

Tech

Your Service Is Healthy, but Its Data Isn’t: Rethinking Cloud-Native Health Checks

Some of the most difficult production issues do not start with a failed service. The application is running, the database is reachable, requests are completed successfully and the monitoring dashboard is green. Yet users report that something is wrong because the information they depend on has stopped changing. I have The post Your Service Is Healthy, but Its Data Isn’t: Rethinking Cloud-Native…
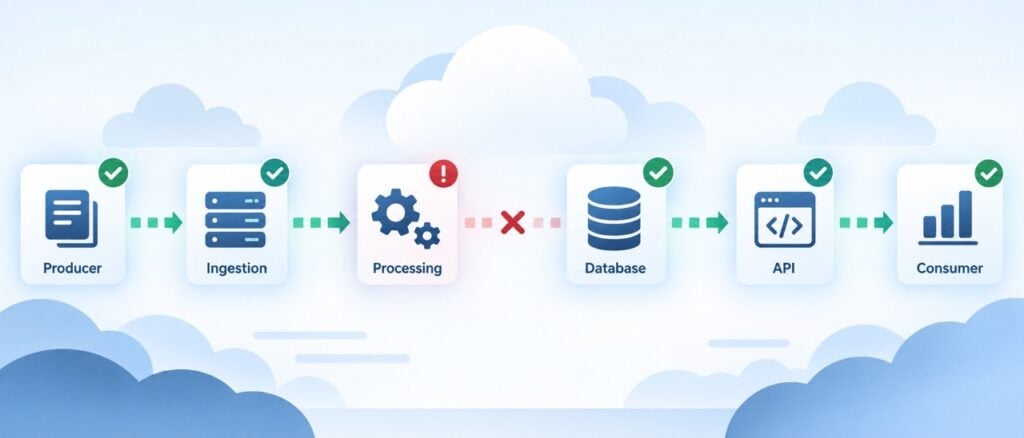
Your Service Is Healthy, but Its Data Isn’t: Rethinking Cloud-Native Health Checks

We haven't written up this one. Container Journal has the full story — the link below goes straight to it.
Read the original at cloudnativenow.com →

More in Tech

When the Payment-Failure Email Is the Exploit: Inside the Magento Template Rendering Chain of CVE-2026-75650

When the Payment-Failure Email Is the Exploit: Inside the Magento Template Rendering Chain of CVE-2026-75650 Opening CVE-2026-75650 is an unauthenticated remote code execution vulnerability in Adobe…

  • CVE-2026-75650 flaw allows unauthenticated remote code execution in Magento platforms.
  • Remediation requires credential rotation in specific order to mitigate post-compromise risks.

The quiet DoS bug in Cisco's email gateway hardening release

The quiet DoS bug in Cisco's email gateway hardening release Cisco's September 2026 hardening release for its email security appliances covers five CVEs.

  • Critical DoS vulnerability CVE-2026-20353 identified in Cisco email gateway hardening release.
  • Flaw affects Secure Email Gateway and Secure Email and Web Manager versions 15.5 and earlier.
  • Resource management and deserialization issues lead to excessive system resource consumption.

More from Friday 18 September →