Indian Hackers Used Anthropic's Claude To Breach OpenAI Systems, Earned ₹6.27 Lakh Bounty
A team of three Indian security researchers used Anthropic's Claude AI models to chain together two software flaws and break into OpenAI's internal systems, ultimately gaining access to employee ChatGPT accounts and the company's internal GitHub code repository. The researchers and the exploit According to WSJ, researchers Harsh Jaiswal, Mohan Pedhapati, and Rahul Maini spent under $3,000 on AI…
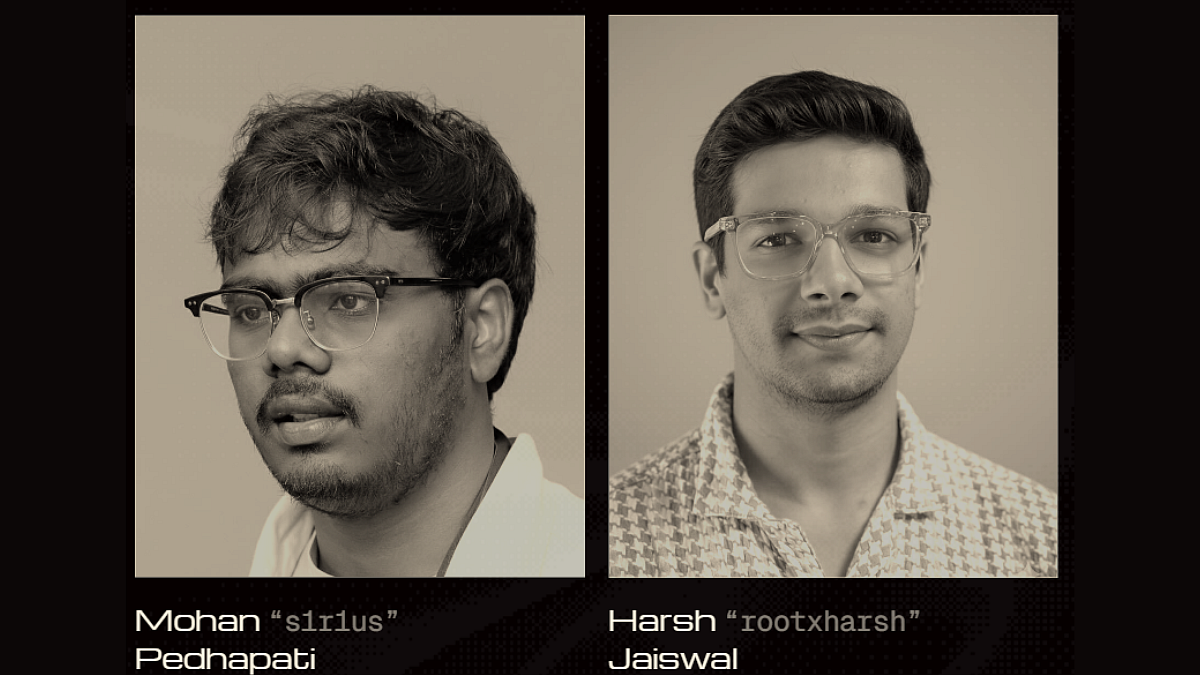
Three Indian security researchers utilized Anthropic's Claude AI models to exploit two software vulnerabilities in OpenAI's internal systems, gaining unauthorized access to employee ChatGPT accounts and OpenAI's internal GitHub code repository. The researchers, Harsh Jaiswal, Mohan Pedhapati, and Rahul Maini, spent less than $3,000 on AI tokens to combine a heap overflow bug in OpenAI's image decoder with a sign-on vulnerability, enabling them to infiltrate the company's systems in a multi-step process.
The exploitation chain began with uploading an image file, followed by ImageMagick decoding, which led to a heap overflow in libheif. This facilitated remote code execution (RCE) on a critical OpenAI Single Sign-On (SSO) flaw, granting access to employees' ChatGPT accounts and OpenAI's internal repository. The researchers then connected this to GitHub, allowing them to submit a pull request inside the internal repository, demonstrating access to OpenAI's systems and ultimately disclosing the vulnerabilities to OpenAI.
Rather than exploiting the compromised access further, the researchers reported the bug responsibly to OpenAI, disclosing the vulnerabilities after demonstrating the access by having OpenAI's coding assistant, Codex, submit a pull request. OpenAI acknowledged and fixed the SSO issue within 14 hours of the initial report. The researchers received a $6,500 (approximately Rs.
6.27 lakh) bounty for their findings, although testing against the community forum was outside the scope of OpenAI's bug bounty program. This incident highlights the increasing role of AI in cybersecurity, with adversaries leveraging powerful AI models to efficiently discover and exploit software vulnerabilities at a fraction of the cost and time required traditionally.
Written by urgent.news from Free Press Journal's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.