Interconnected tech environments and mapping the invisible attack surface
The modern enterprise attack surface is becoming harder to see, and even harder to defend. Cloud platforms, third-party services, AI tools, identities and forgotten Internet-facing assets have created interconnected environments where seemingly minor weaknesses can combine to provide attackers with a route into critical systems. Traditional vulnerability management, built around identifying and…
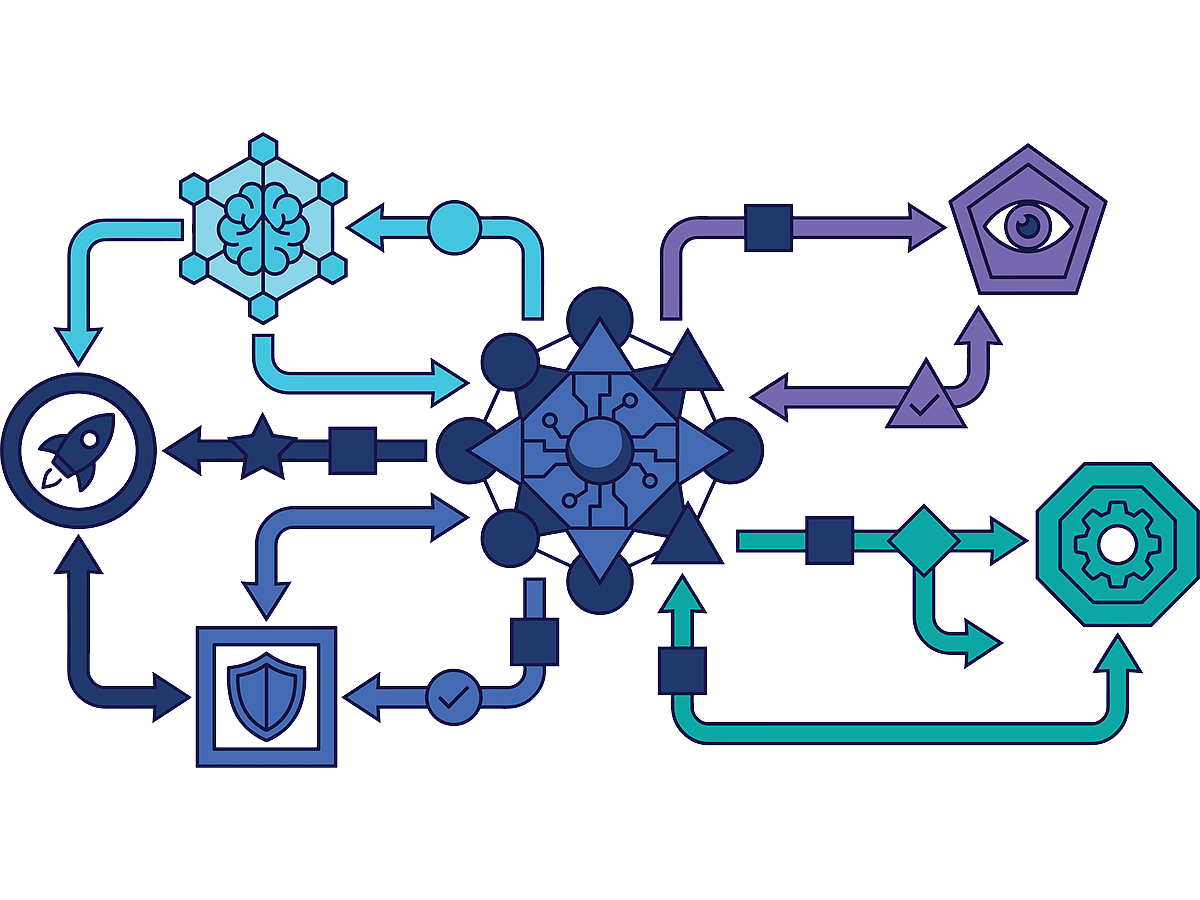
Enterprise attack surfaces are growing in complexity, making them tougher to detect and protect against. Cloud services, third-party applications, AI tools, and neglected internet-facing elements have woven together to form intricate networks where even small vulnerabilities can be exploited to gain access to vital systems. Traditional approaches to vulnerability management, which focus on identifying and rating individual flaws, are struggling to keep up with this intricate landscape.
Meriam ElOuazzani, Censys' Vice President, explains that "traditional vulnerability management starts with what an organization already knows it owns. Attackers don't have that constraint." Consequently, security teams require a comprehensive, internet-wide perspective to truly understand their actual attack surface and how seemingly unrelated weaknesses may be connected.
The challenge lies in shifting the focus from discovering vulnerabilities to comprehending the extent of exposure. Bernard Montel, Tenable's EMEA Field CTO, observes that breaches rarely stem from a single weakness. Instead, they often follow a sequence: an exposed point of entry, improper permissions, and a route to valuable resources.
This underscores the importance of context in assessing risk. Two vulnerabilities with identical severity scores can pose vastly different levels of business risk depending on factors such as their accessibility, exploitability, and connection to sensitive systems. "Context is the key differentiator," ElOuazzani emphasizes. "Real-world exposure and infrastructure context enable teams to prioritize genuine risks rather than treating every Common Vulnerabilities and Exposures (CVE) or severity score equally."
The looming threat of new challenges is on the horizon. Censys reports that over 294,000 internet protocol (IP) addresses are already exposing artificial intelligence (AI) and large language model (LLM) tools, a staggering increase of more than 60 percent in just nine months. Bernard Montel envisions identity management as another significant frontier.
As autonomous AI agents gain the ability to authenticate and act independently, organizations will need to manage an exponentially larger set of permissions to maintain security. By 2030, cyber resilience may hinge less on merely tallying vulnerabilities and more on continuously mapping the interconnections between assets, identities, AI systems, and vulnerabilities, detecting attack paths before adversaries can exploit them.
Written by urgent.news from Gulf News's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.