Google Pixel phones pwned in zero-click attacks
CISA gives federal agencies just 3 days to patch
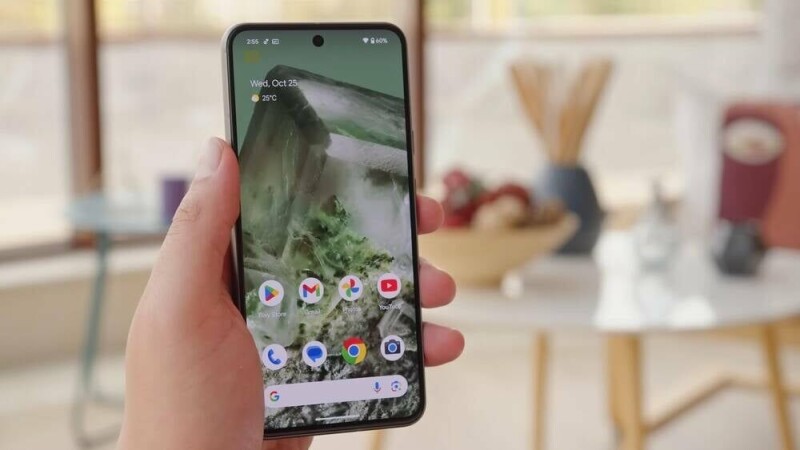
Google Pixel smartphones have been found vulnerable to zero-click attacks due to an improper authorization bug in their cellular modems. This flaw, officially cataloged as CVE-2026-58704, allows attackers to bypass permission checks and escalate privileges without any user interaction. The vulnerability was disclosed by Google on Tuesday, with the company warning that it may have already been exploited.
The Register attempted to obtain further details from Google, but received limited information. The National Institute of Standards and Technology (NIST) has also added this vulnerability to its Known Exploited Vulnerabilities Catalog (KEV), urging agencies to patch the issue within three days. Zero-click attacks, which exploit such flaws, are commonly used by commercial spyware developers to surveil targeted individuals.
Written by urgent.news from The Register's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.
This story
This is one outlet's version. Read the fullest account.
- Google Pixel phones pwned in zero-click attacks theregister.com
- Google rolling out Android 17 QPR2 Beta 5 for Pixel 9to5google.com