Cybersecurity shifts from flaws to resilience
■ Tenable is participating in GISEC Global 2026. What makes the Middle East an important market for Tenable, and what will you be highlighting at the event? The Middle East is at the forefront of digital transformation, with governments and enterprises investing heavily in AI, cloud infrastructure, smart cities and connected technologies. This creates enormous opportunity for growth and…
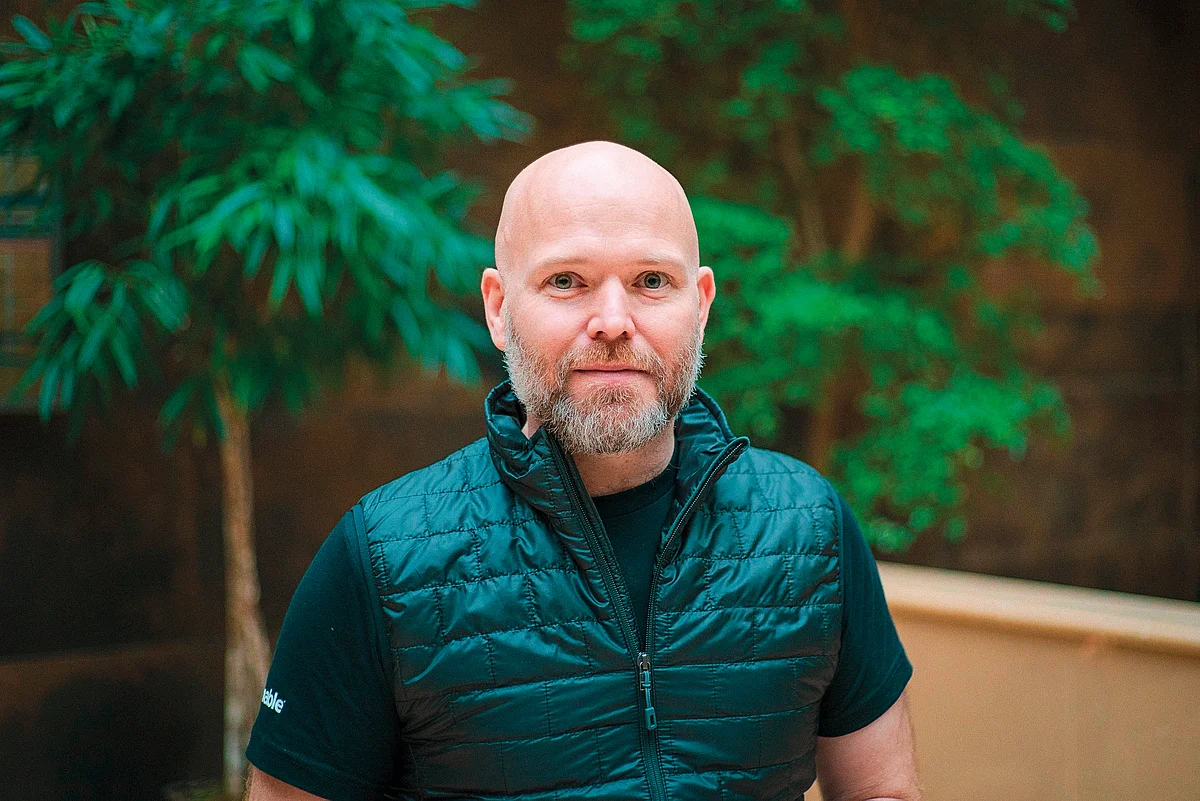
Tenable is participating in GISEC Global 2026, a conference focused on digital transformation and cybersecurity. The Middle East is an important market for Tenable due to its rapid adoption of AI, cloud infrastructure, smart cities and connected technologies. This creates a complex and interconnected cyber environment that requires a unified approach to reducing cyber exposure across IT, cloud, identities, OT and AI.
The UAE and other Gulf countries are accelerating their AI adoption, which brings both opportunities and cybersecurity risks. A 2026 Cloud and AI Security Risk Report found that 70% of organizations have integrated AI or machine learning components, while 18% have granted AI services admin permissions that are rarely audited. This highlights the need to treat AI as part of identity governance, rather than a standalone issue.
Smart cities, cloud computing and connected systems are also being heavily invested in across the Middle East. However, this interconnectivity can make cyber resilience a challenge, as a single weakness can have far-reaching consequences. Organizations should rethink traditional vulnerability management and shift towards understanding which exposures are most likely to cause a business-impacting incident.
This involves considering factors such as vulnerabilities, threats, misconfigurations, identity risks, asset criticality and attack pathways.
Human error, especially in the form of phishing and social engineering, remains a significant factor in cybersecurity incidents. While employee training can be helpful, it is not a foolproof solution. Instead, organizations should focus on addressing exploitable flaws on the endpoint, implementing least privilege principles and short-lived credentials, and monitoring for unusual account behavior. This approach is more effective in preventing incidents than simply hoping employees will follow training guidelines.
Written by urgent.news from Gulf News's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.