Urgent.News

What's breaking now, across thousands of outlets.

Tech

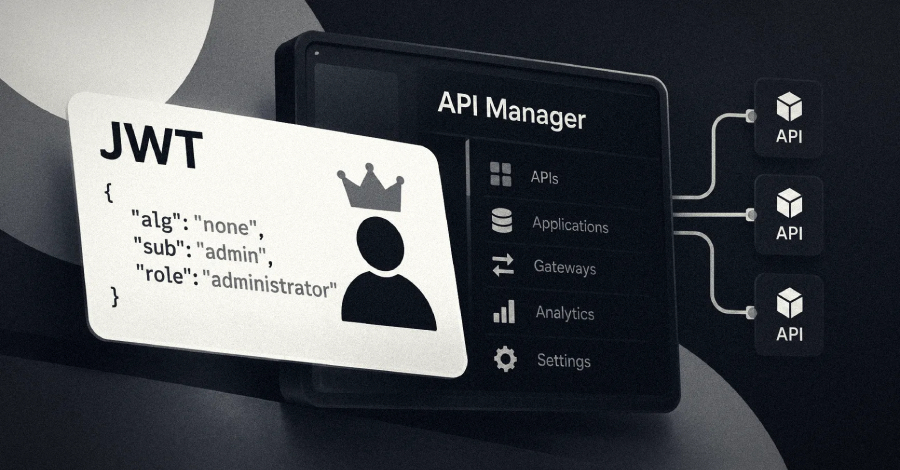
Active Exploitation Attempts Target WSO2 API Manager JWT Bypass With Forged Admin Tokens

A critical security flaw in WSO2 API Manager has come under active exploitation in the wild, according to findings from watchTowr. The vulnerability, tracked as CVE-2026-5430 (CVSS score: 9.8/10.0), is a case of improper verification of a cryptographic signature that could result in account takeover. Hacktron Team has been credited with discovering and reporting the flaw. "JWT authentication
Active Exploitation Attempts Target WSO2 API Manager JWT Bypass With Forged Admin Tokens

We haven't written up this one. The Hacker News has the full story — the link below goes straight to it.
Read the original at thehackernews.com →

More in Tech

HTTP/HTTPS Malleable C2: The Chameleon of Network Communications

Author: @cyberrscourse | Cybersecurity Education & Research Published: September 16, 2026 ⚠️ LEGAL WARNING: The techniques described in this article are for educational purposes only.

  • Malleable C2 disguises communication as regular web traffic using HTTP/HTTPS.
  • Altered patterns mimic Google Analytics or jQuery CDN requests to blend in.
  • Detection techniques include behavioral analysis, JA3/JA4 fingerprinting, and network flow analysis.

More from Wednesday 16 September →