Ditching WebSockets: Server-Sent Events in Next.js 📡
Liquid syntax error: Variable '{{% raw %}' was not properly terminated with regexp: /\}\}/
We haven't written up this one. Dev.to has the full story — the link below goes straight to it.
What's breaking now, across thousands of outlets.
Liquid syntax error: Variable '{{% raw %}' was not properly terminated with regexp: /\}\}/
We haven't written up this one. Dev.to has the full story — the link below goes straight to it.
A skilled human attacker exploited a critical Marimo notebook flaw and moved from an exposed WebSocket session to authenticated access on an SSH bastion host in eight seconds, Sysdig’s Threat Research…
A browser extension used by nearly 31,000 Twitch viewers has been found forwarding live OAuth session tokens to proxy infrastructure controlled by the operator of a Russian-language commercial bot…
Profitable state-owned enterprises generated aggregate profits of Rs. 423.3 billion during the first half of fiscal year 2026, while loss … Read More The post Profitable SOEs Earn Rs.
I wasn’t looking for another project. I just wanted a music player I could leave running while gaming or streaming without wondering how much memory and CPU it was using.
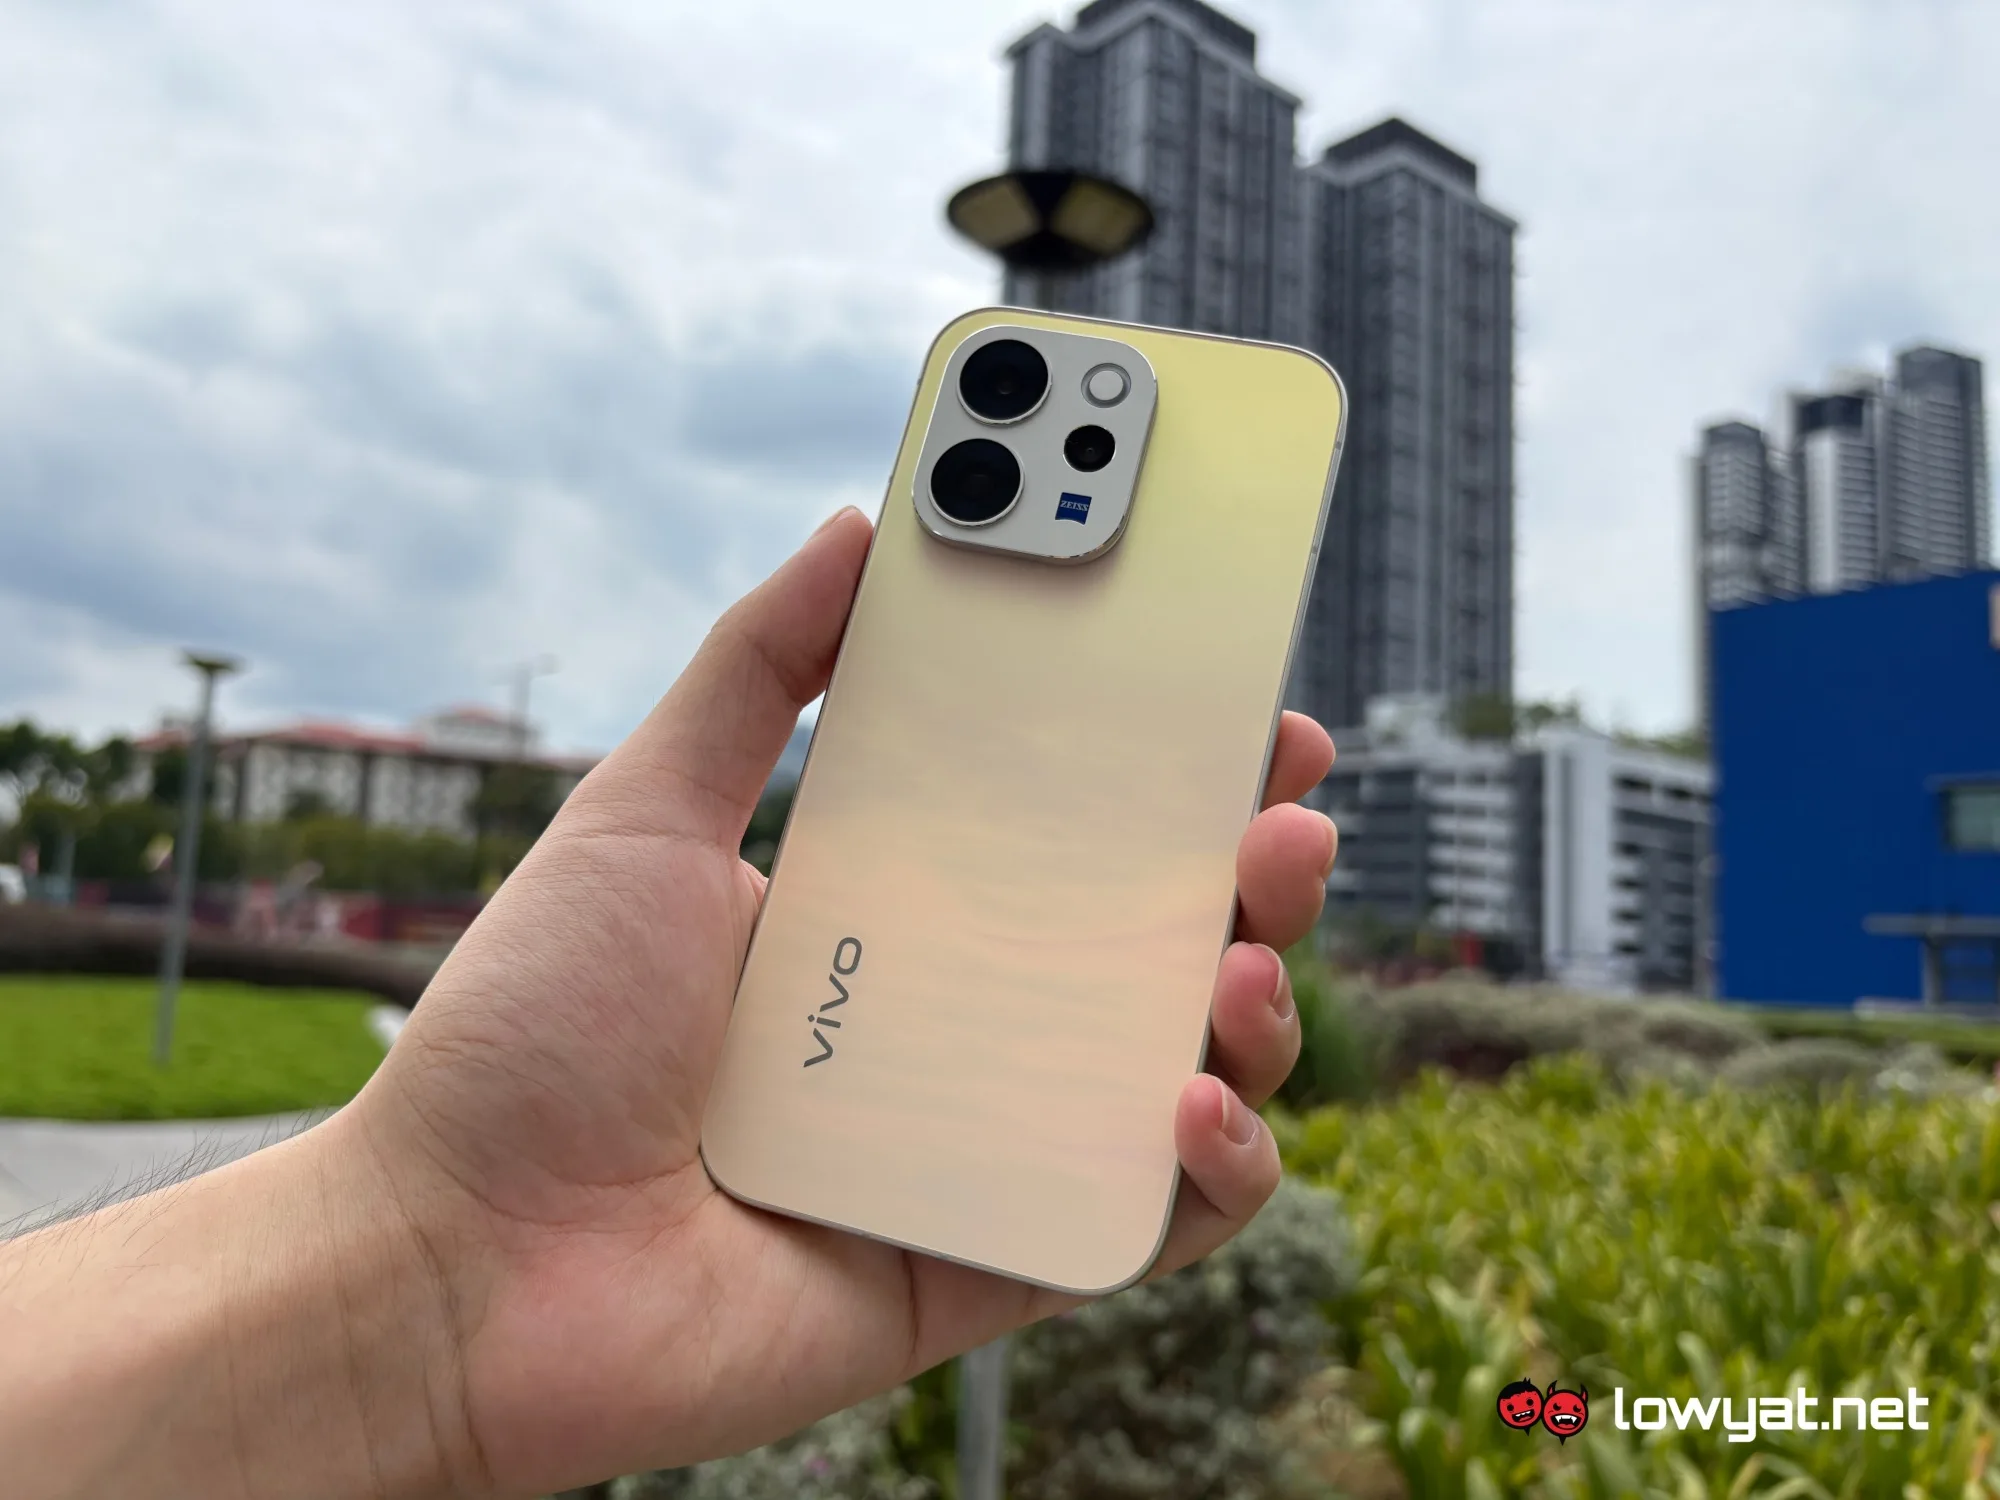
vivo launched the V80 Lite as the newest addition to its V series fairly recently. Now, it looks like the Chinese phone maker is preparing to release another member in the lineup soon.
My local chat app was fast every single time I tested it, and slow every single time I actually used it. That's the tell, and I ignored it for weeks.