Security moves below the operating system as AI PCs take on the data protection job
Chipmakers and device makers are rebuilding enterprise data loss prevention around on-device AI security, as employees paste sensitive material into chatbots and assistants faster than rules-based tools can inspect it. Nearly 40% of all data moving into AI tools now involves sensitive material, according to a 2026 Cyberhaven report. The shift pushes classification off the […] The post Security…
Chip manufacturers and device makers are redefining enterprise data loss prevention through on-device AI security, driven by employees' habit of inputting sensitive information into chatbots and assistants. According to a 2026 Cyberhaven report, nearly 40% of data entering AI tools is sensitive. This shift moves classification away from the cloud and into the silicon, where models can operate efficiently and data remains on the endpoint.
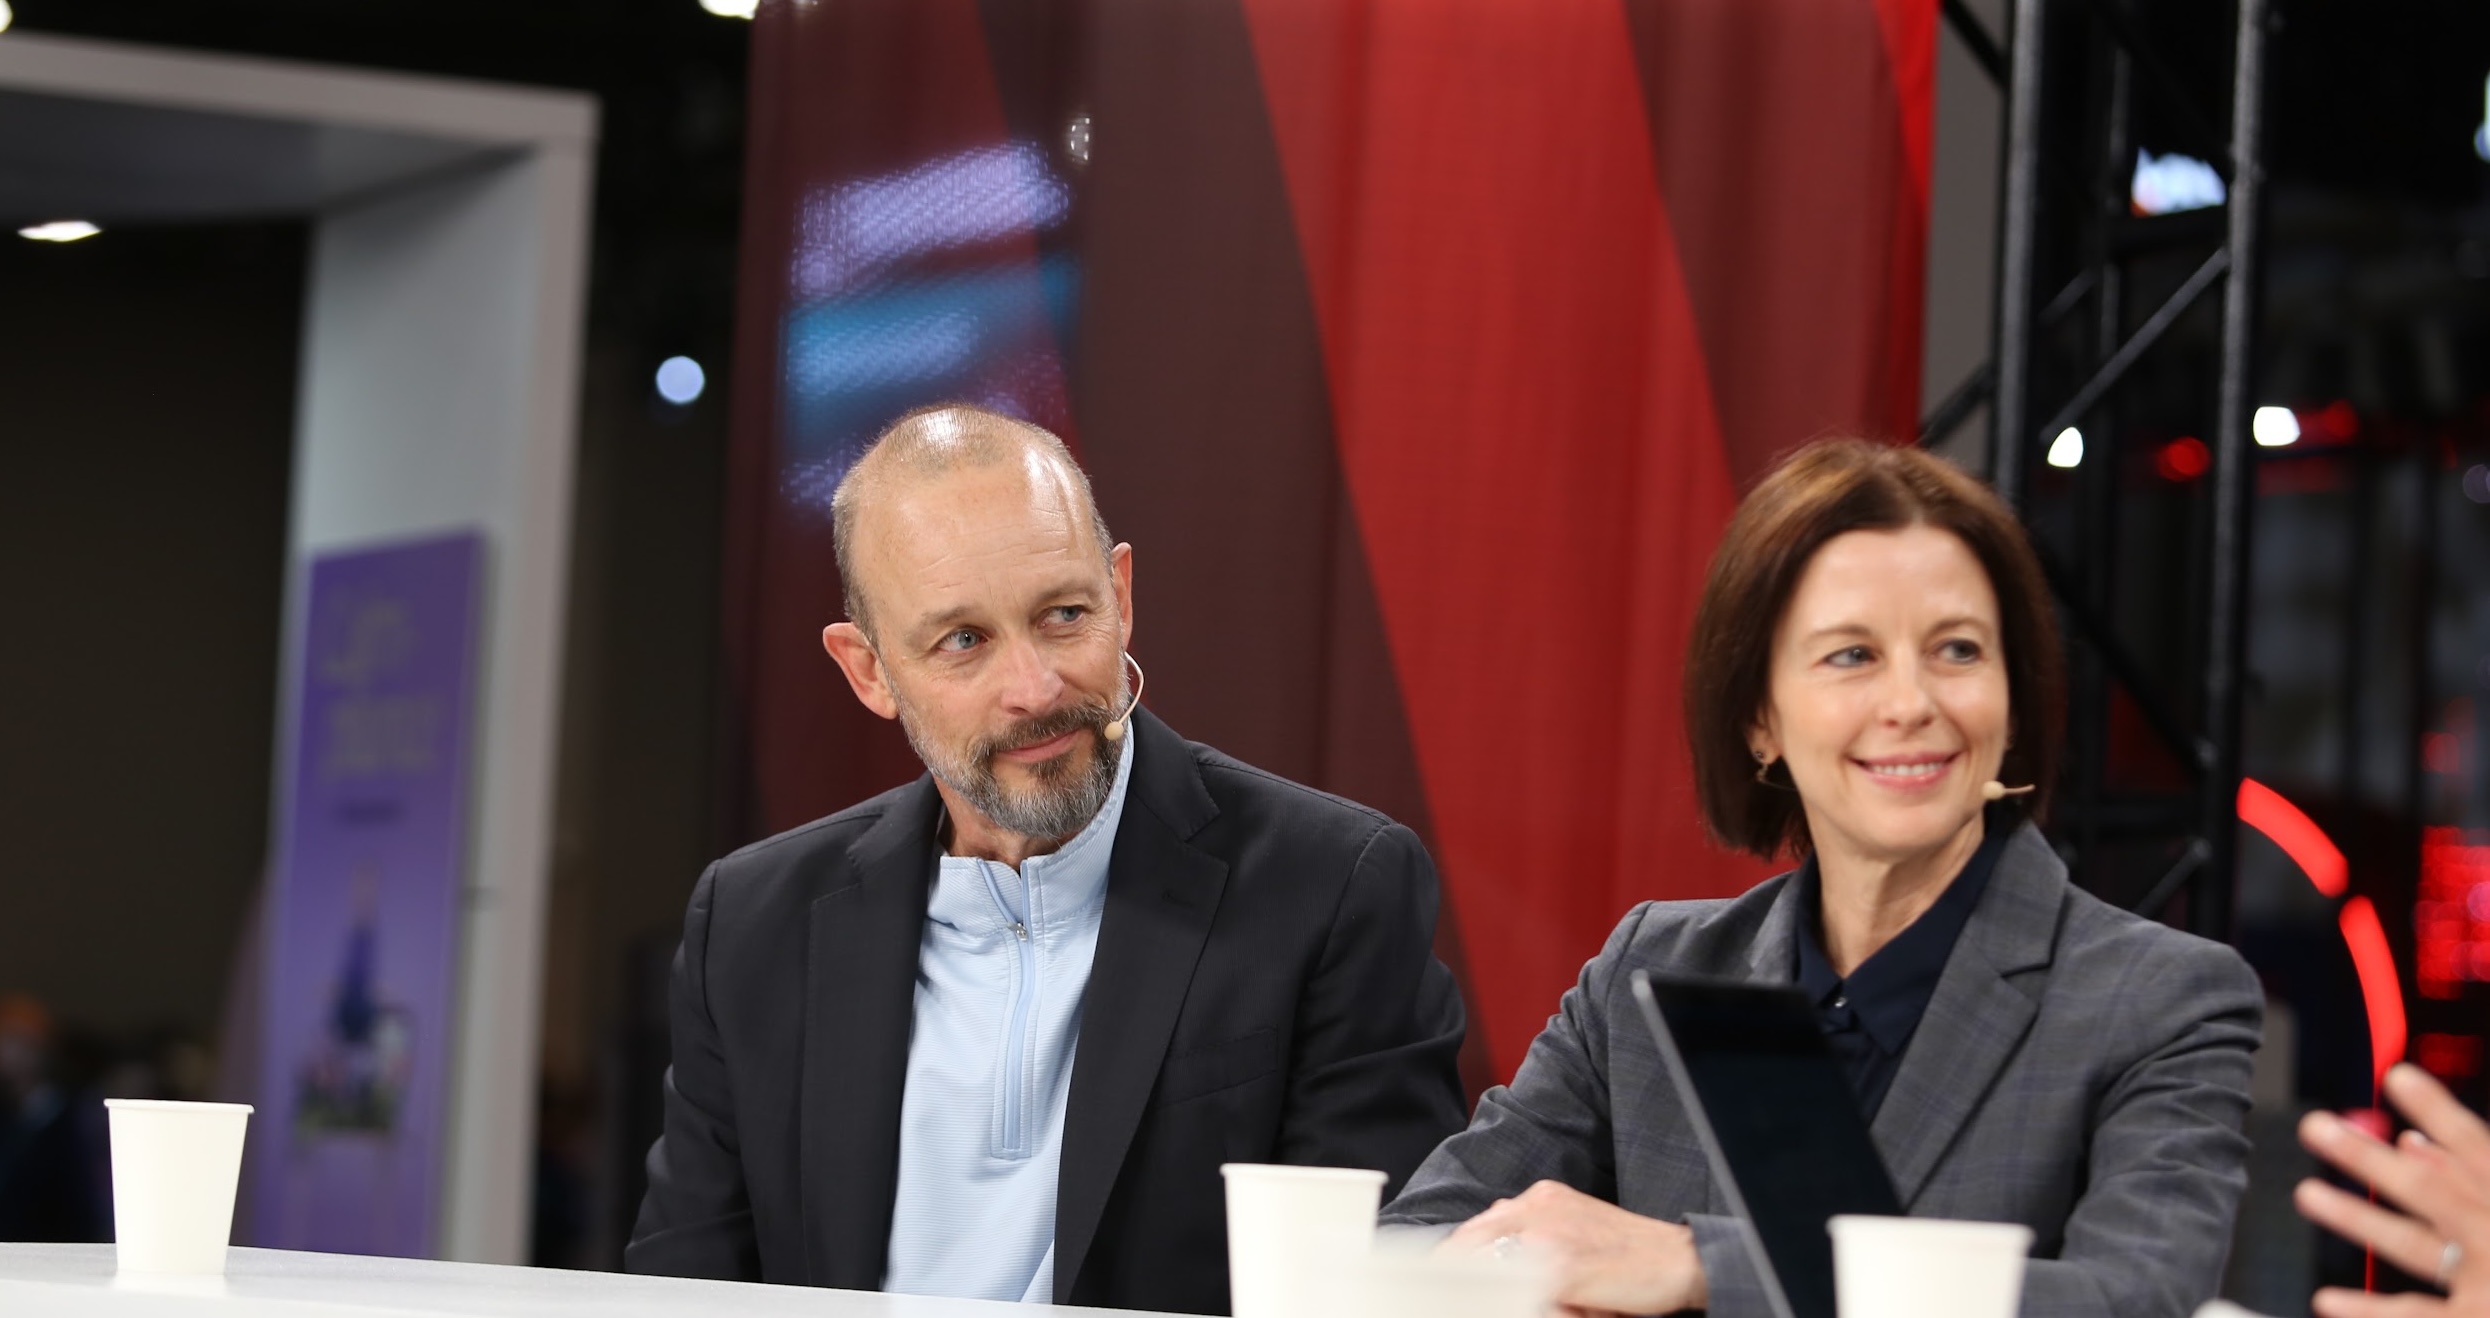
This transition requires a stack that extends below the operating system, encompassing the neural processing unit, firmware, and boot sequence. Intel and Dell Technologies are integrating hardware telemetry into the same security consoles used by analysts, as per Todd Cramer, senior director of business development and security ecosystem at Intel, and Lori Zwilling, senior director of software product management at Dell.
Cramer highlighted Dell's partnership with CrowdStrike, which has introduced its first AI model running on an Intel Neural Processing Unit (NPU) within a Dell device. CISOs' primary concern, according to Cramer, is data protection. Zwilling emphasized that hardware-based detections can identify threats that software tools overlook, such as BIOS integrity status and firmware tampering alerts.
This hardware-centric approach extends to post-quantum readiness, impacting firmware signing and the Intel boot sequence. Zwilling stressed that AI security must be comprehensive, covering the client device, AI models, data, inferencing, containers, and compute infrastructure.
Written by urgent.news from SiliconANGLE's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.