Data loss prevention gets a second act as AI rewrites an old security problem
Security vendors are rebuilding data loss prevention, or DLP, around contextual understanding rather than pattern matching — and AI-powered DLP is giving the category’s most stubborn unsolved problem a second act. Decades of rule-based DLP tools left security teams buried in alerts they could not act on, and the arrival of generative AI has both […] The post Data loss prevention gets a second act…
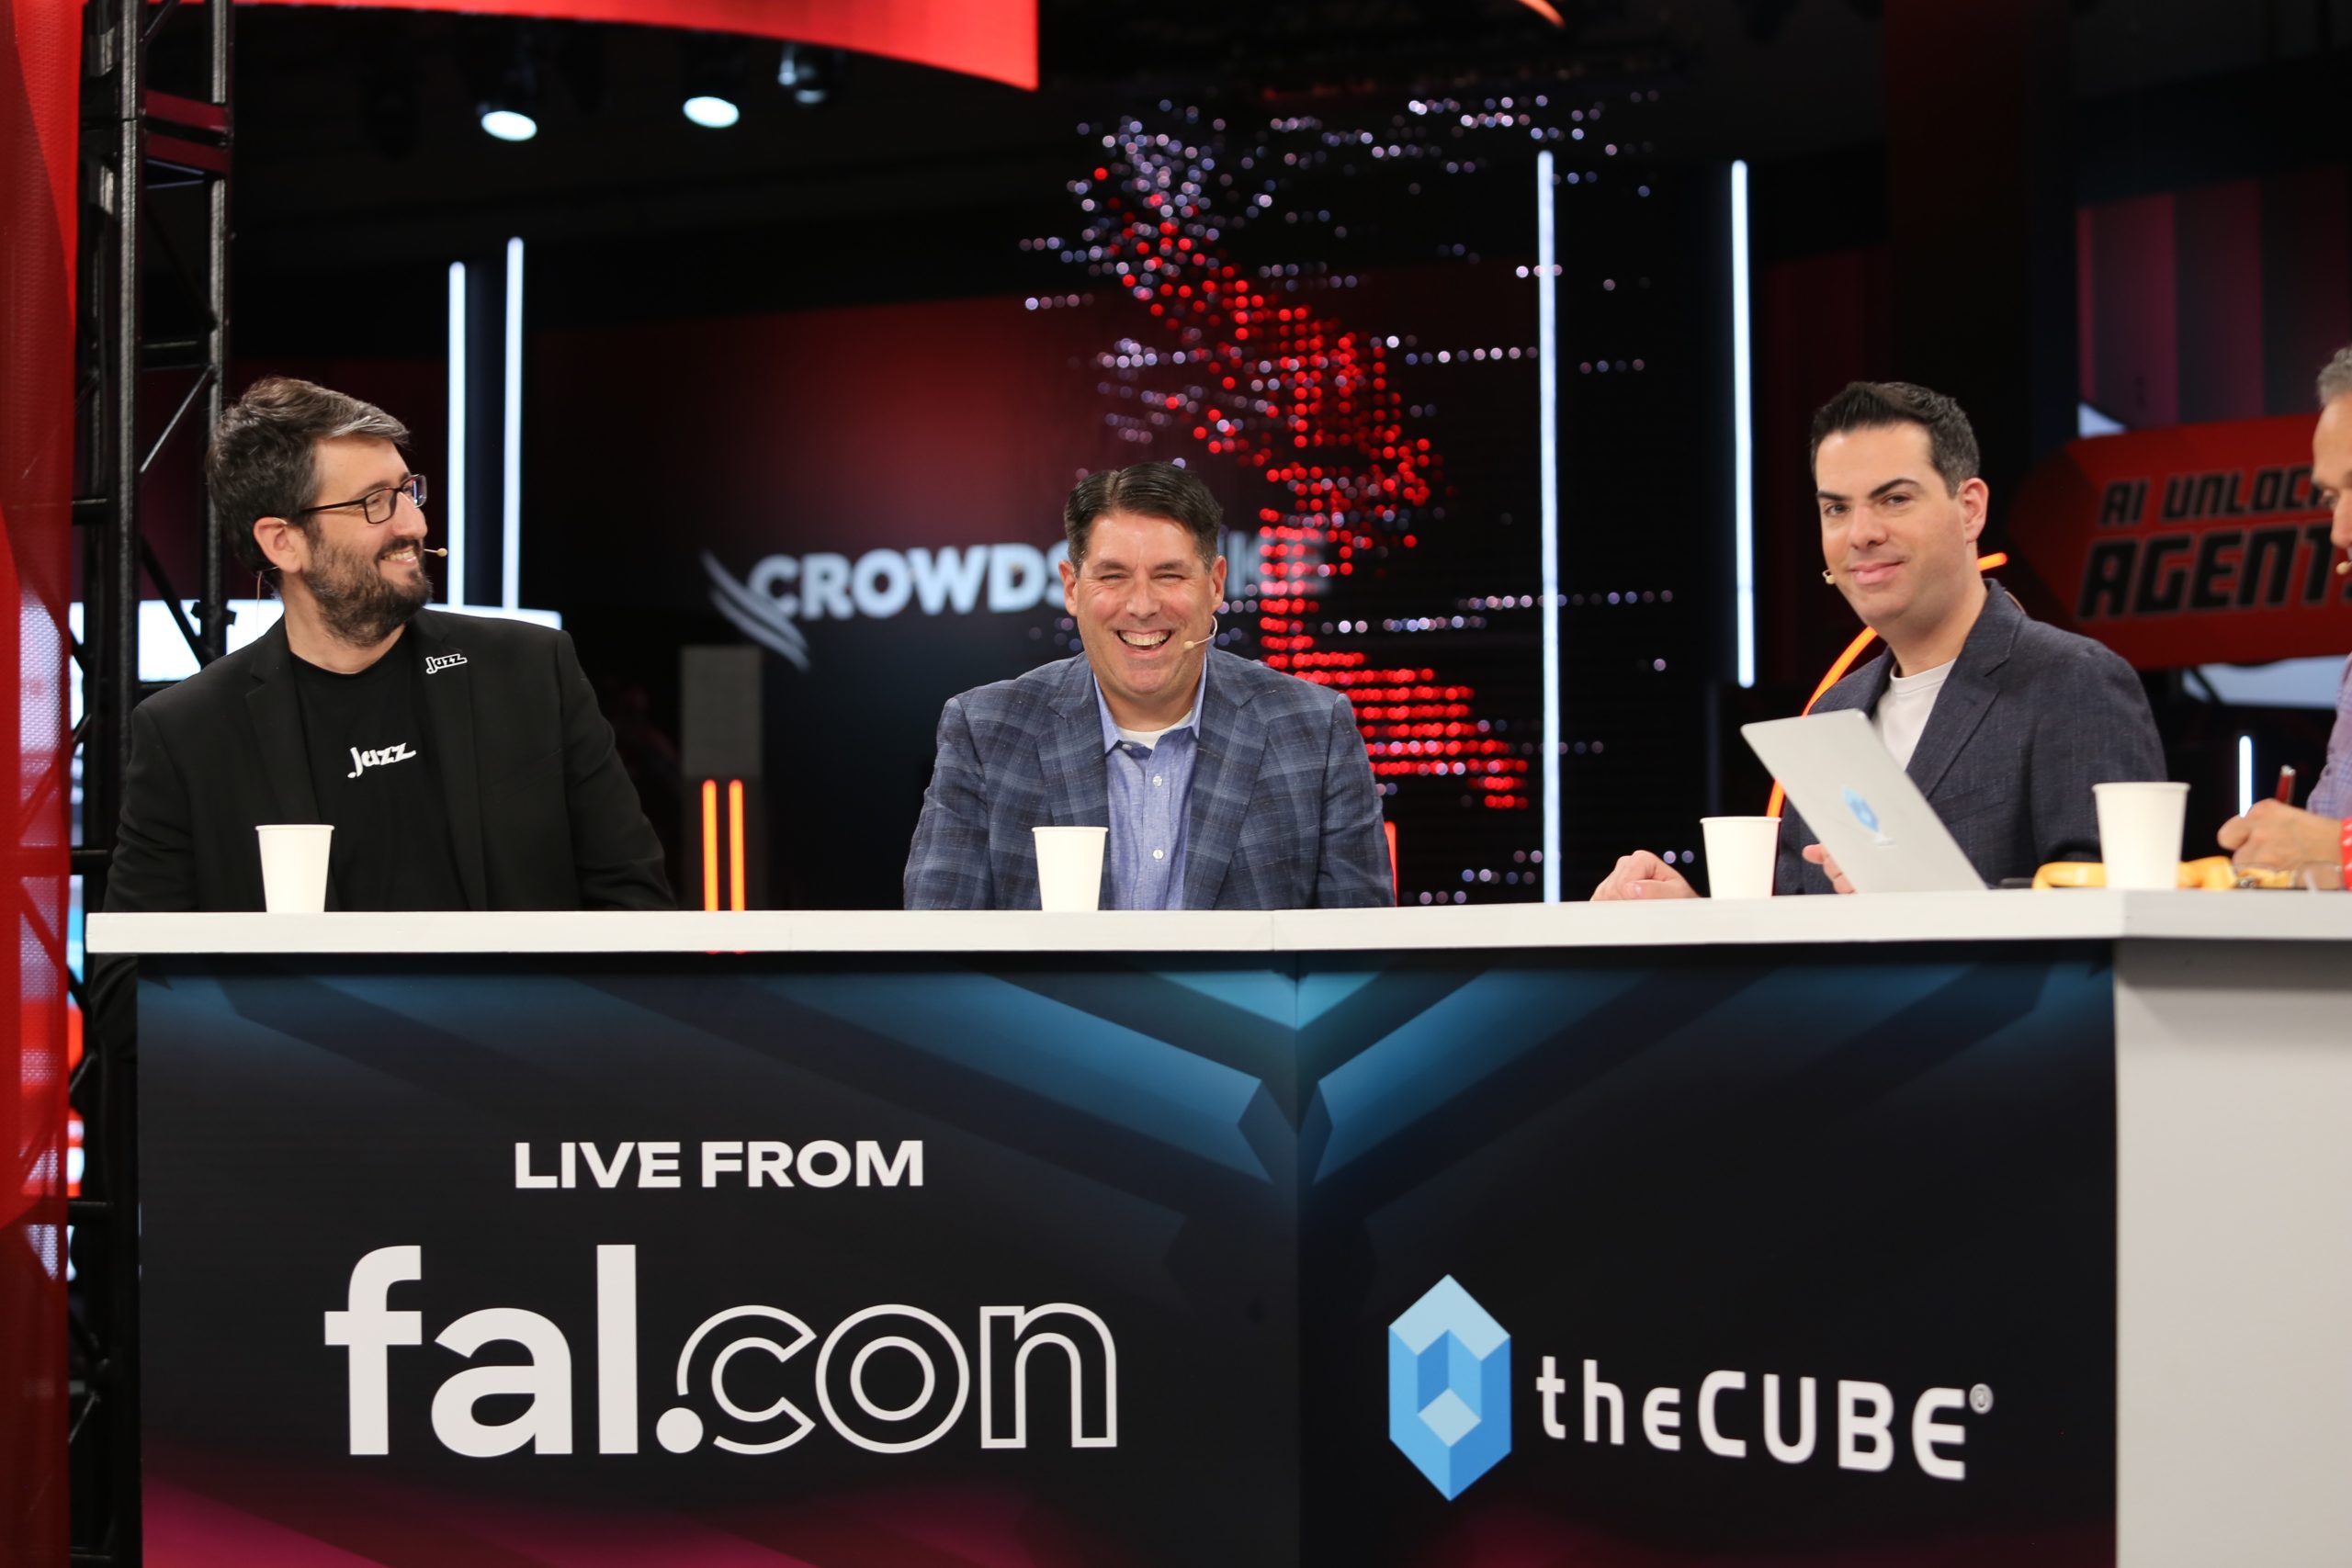
Data loss prevention (DLP) is undergoing a transformation as artificial intelligence (AI) redefines the security problem. Traditional rule-based DLP tools that plagued security teams with alerts they couldn't act on have been replaced by AI-powered solutions that offer a contextual understanding of data flows. This shift has been driven by partnerships between platform companies, cloud providers, and startups, with Israeli startup Jazz emerging from stealth with $61 million in funding.
Jazz's AI-powered investigator, Melody, is being integrated with CrowdStrike's Falcon Foundry, accelerating the startup's growth. CrowdStrike's and Amazon Web Services' accelerator program helped identify gaps in existing DLP solutions, leading to the development of Jazz's business-first approach. As the AI era continues to evolve, security teams need to focus on minimizing response and exposure times, with AI-powered DLP being a crucial component in this ongoing shift.
Written by urgent.news from SiliconANGLE's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.