Urgent.News

What's breaking now, across thousands of outlets.

Tech

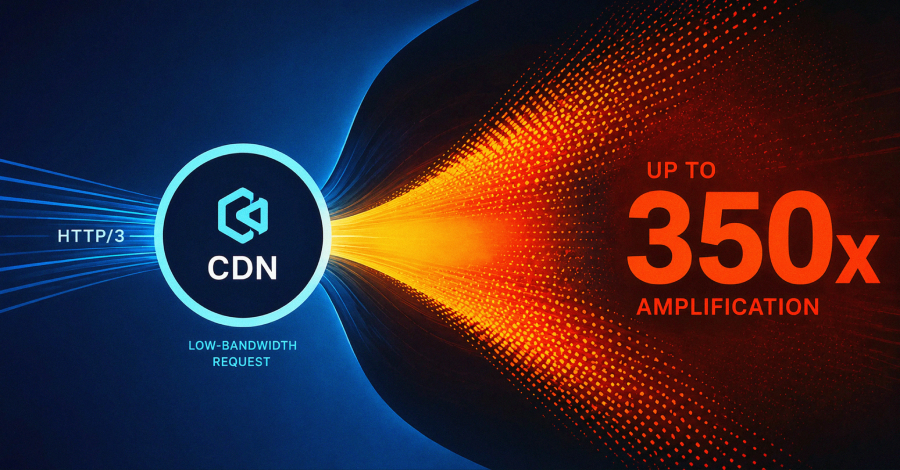
CDN Tsunami Attack Abuses HTTP/3 Translation for Up to 350x DoS Amplification

Cybersecurity researchers have disclosed two denial-of-service (DoS) attacks that exploit how major content delivery networks (CDNs) convert client-facing HTTP/3 traffic into HTTP/1.1 requests to the websites they front, amplifying a low-bandwidth request stream by up to 350x against the origin server. The attacks, collectively named "CDN Tsunami," were evaluated against Alibaba, Baidu,
CDN Tsunami Attack Abuses HTTP/3 Translation for Up to 350x DoS Amplification

We haven't written up this one. The Hacker News has the full story — the link below goes straight to it.
Read the original at thehackernews.com →

More in Tech

The GTA VI leak isn't really about GTA VI — it's an extortion playbook

Originally published in Spanish on El Rack . Browser translation handles the rest of the site fine if you're into homelab/security content.

  • GTA VI leak involves extortion, not accidental release
  • Cyberleek group demands changes in game industry practices
  • Leak follows 2022 attack on Rockstar Games servers

Laravel env() Outside config/: Catch Deployment Bugs Before config:cache

The bug only appears after configuration caching A Laravel application can behave perfectly during development and then fail after deployment because a service class reads an environment variable…

  • Direct env() calls outside config/ may fail during deployment
  • Laravel Env Guard tool scans for unsafe env() usage
  • Review recommends comparing environment file inventories

More from Thursday 20 August →