SafePal discloses data breach affecting 39,798 customers
SafePal said it had patched the flaw and hired an independent security firm to review the fix and its order-processing systems.
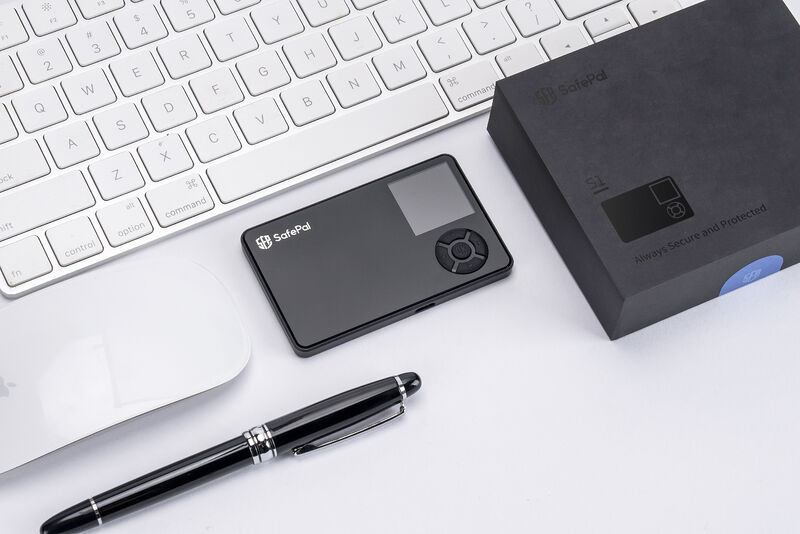
Hardware wallet maker SafePal disclosed a security breach that exposed personal details of nearly 40,000 clients. The compromised data included names, physical addresses, and contact information, putting users at risk of phishing and identity theft. However, the breach did not affect any cryptocurrency funds or private keys. SafePal offers both hardware wallets and software for secure digital asset management.
The latest attack follows a $120 million theft from Coldcard hardware wallets. While the incidents highlight the risks associated with crypto-storage solutions, they also underscore the importance of assessing concentration risk and diversifying storage methods. SafePal identified an "authorization flaw" in a plug-in used for tracking customer orders, which allowed attackers to view other customers' order information.
The breach affected 39,798 customers who placed orders between March 2, 2025, and April 11, 2026. SafePal confirmed that the breach did not compromise core wallet security, as seed phrases, private keys, and other sensitive information remained protected. Users who shared their private keys or seed phrases via phishing attempts should treat their wallets as compromised and move their assets to a new wallet.
SafePal patched the vulnerability and enhanced security measures after notifying affected customers and engaging a third-party security audit. The company also retained customers' personal data in the order-processing system for only 90 days and removed over 30 fraudulent websites and phishing links linked to the breach. Customers can verify if their data was affected through a verification tool on SafePal's website.
Written by urgent.news from CoinDesk's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.
This story
This is one outlet's version. Read the fullest account.