A dangerous Zoom screen-sharing bug could have let hackers hijack other devices on a call
It doesn't matter if the attacker is the host or a participant.
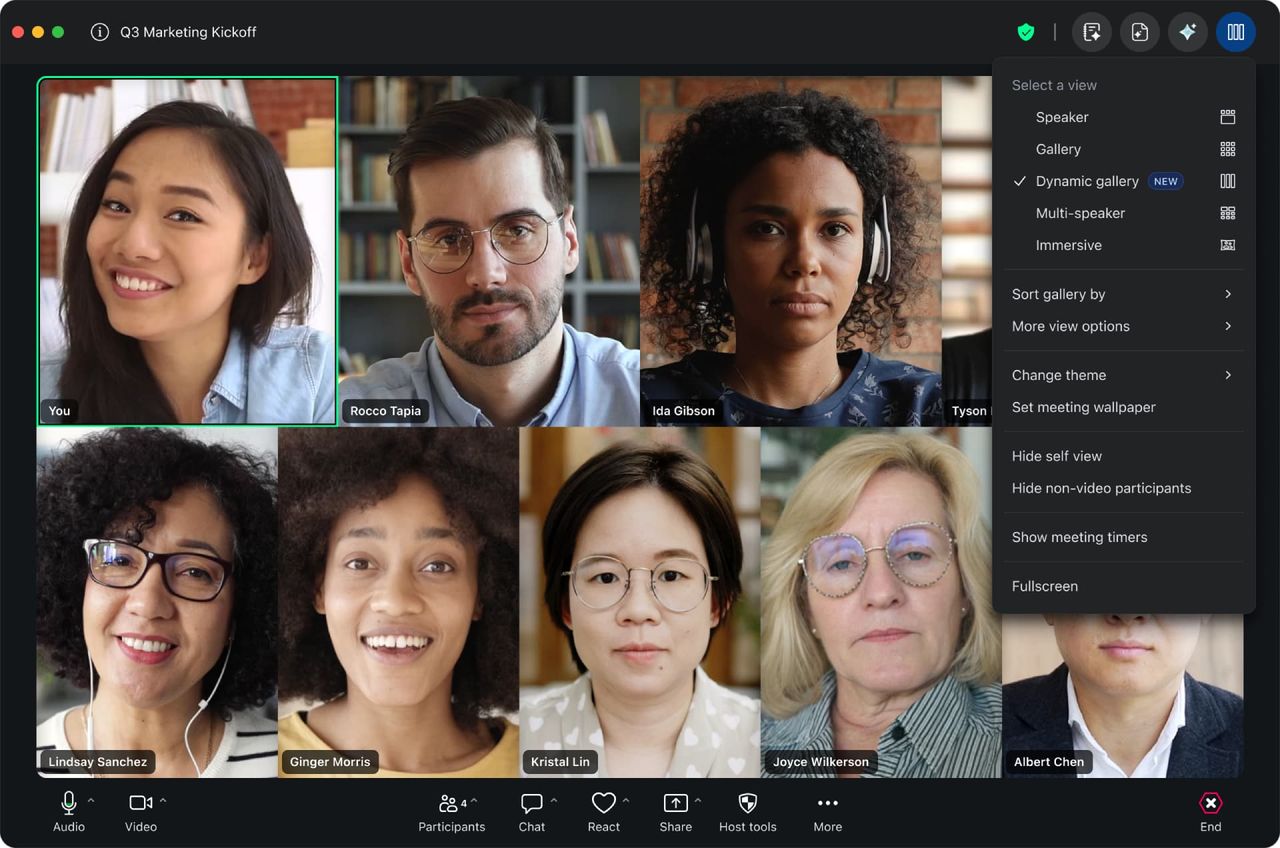
A dangerous Zoom screen-sharing bug could have allowed hackers to hijack other devices connected to a call, according to security researchers. The vulnerabilities, present in every version of Zoom up to version 7.0.5 on all devices and operating systems, required only the victim to join a video call to be compromised. The flaws were discovered using AI-powered security research, with security firm A Security using frontier models to identify and exploit the bugs in less than 24 hours.
Once exploited, the malicious actors could take control of the device, steal files, access sensitive information, and execute further attacks. Zoom acknowledged the vulnerabilities, labeled them as CVE-2026-53413, CVE-2026-53414, and CVE-2026-53415, and advised users to update their client to the latest version, 7.1.5 and 7.0.6.
The researchers warned that the AI-powered tools have made such exploits accessible to non-nation-state actors with minimal resources.
Written by urgent.news from TechRadar's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.