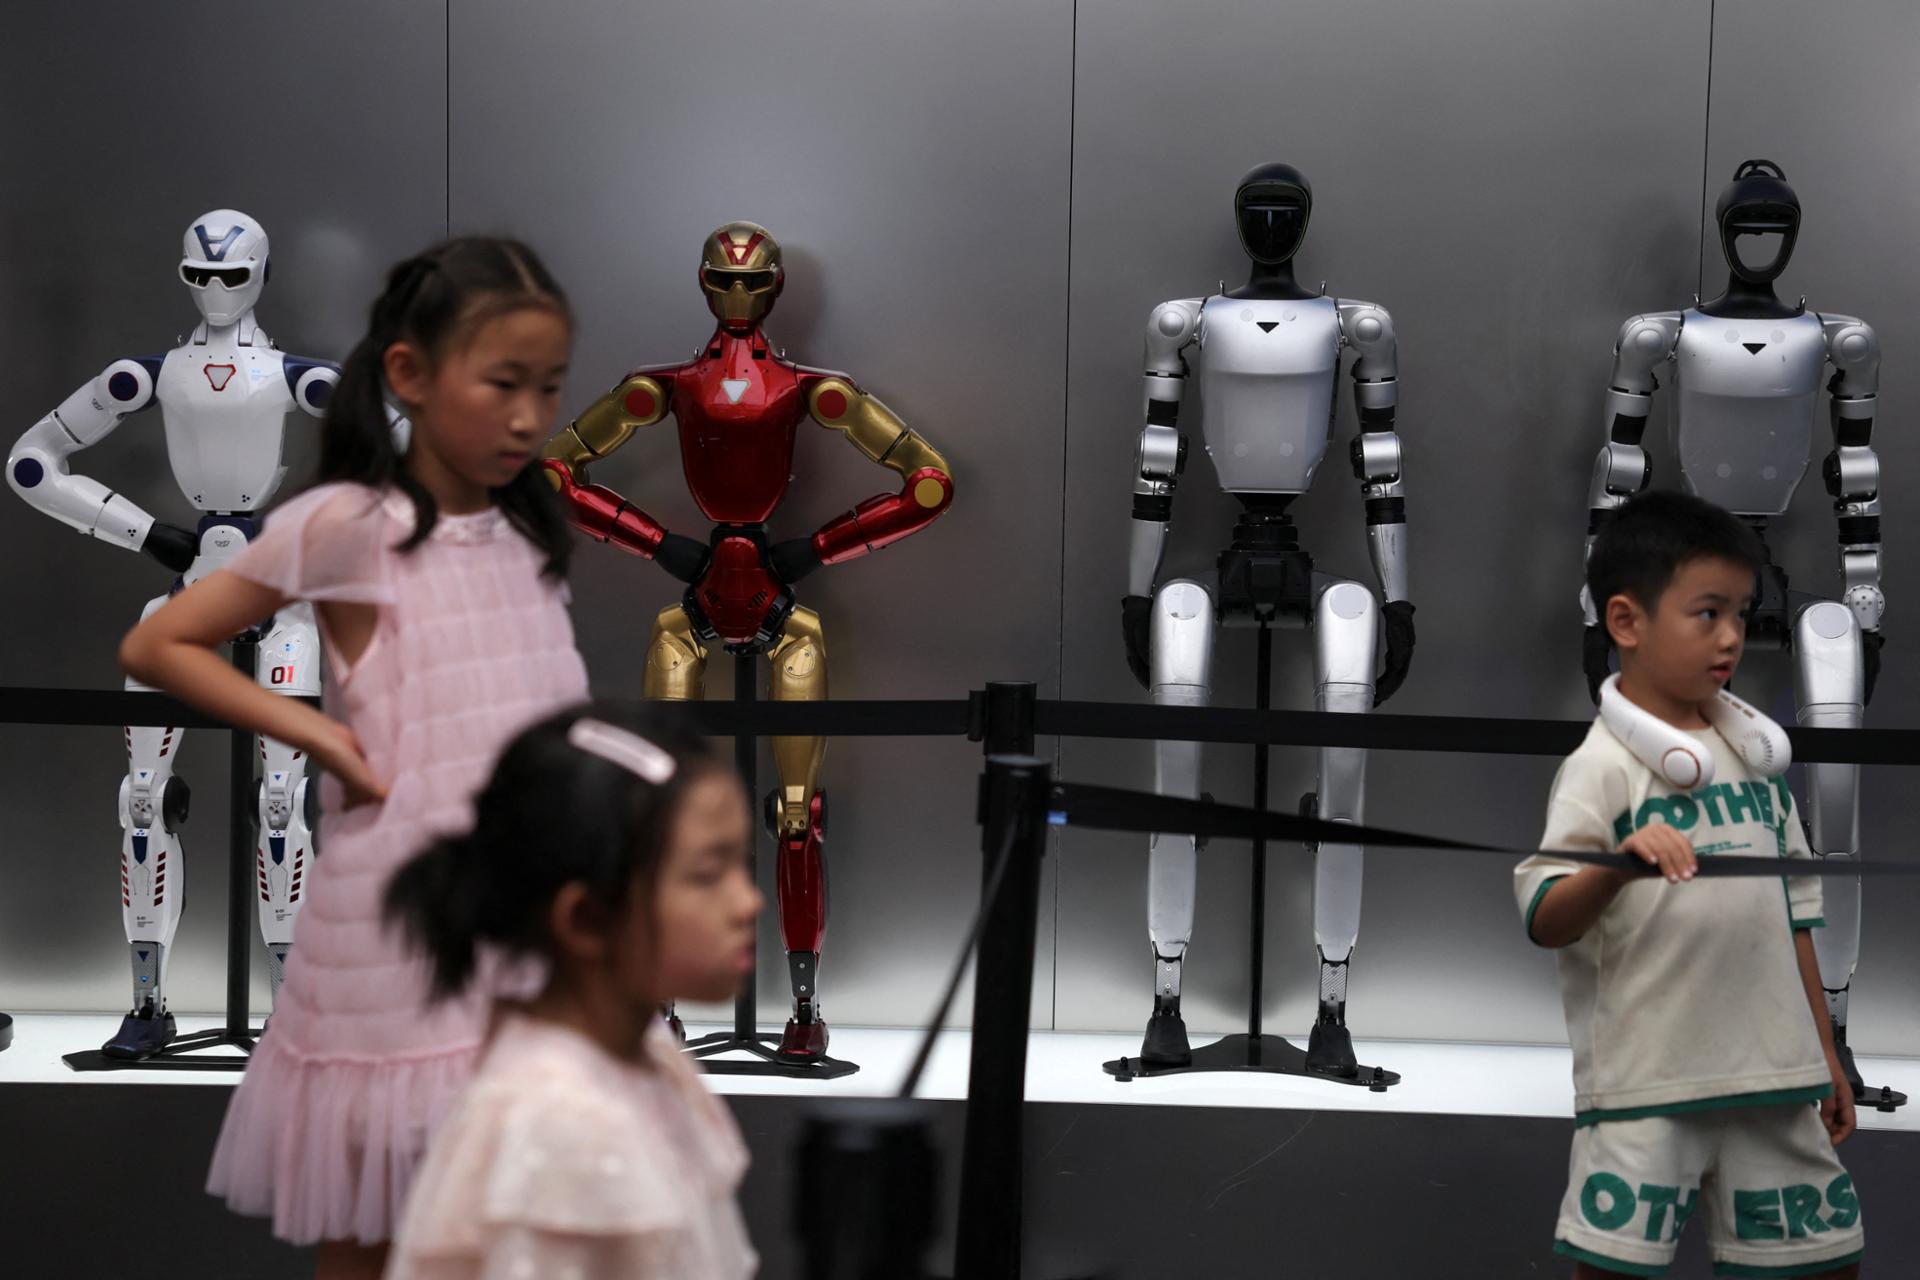
Steam hardware shipper breach leaks customer data, including names and addresses
Valve says a data breach may have exposed the personal information of customers who ordered its Steam hardware in Europe. In an email sent to users, Valve says its European shipping partner, CEVA Logistics, suffered a data breach that may have included customer names, addresses, phone numbers, and email addresses. The breach at CEVA occurred […]
Ceva Logistics, a leading shipping and logistics company headquartered in France, has fallen victim to a significant cyberattack that has sent shockwaves across various industries. The breach, which began on July 29, has exposed personal information of customers to hackers, affecting at least eight warehouses used for shipping goods across Europe.
Numerous companies have been impacted by the breach, including Dutch online retail giant Bol, luxury retailer De Bijenkorf, football club Ajax, banking giant ING, and video game giant Valve. Bol's website warned customers that their data, including names, home addresses, phone numbers, and email addresses, may have been compromised. Other affected entities reported delays in shipping orders and some cancellations.
Valve, the company behind the popular gaming platform Steam, confirmed that its systems were targeted, and alerted customers who made recent purchases that their personal information had been stolen. The breach has caused shipping delays for goods in the affected warehouses, with Ceva acknowledging that some applications and services are operational again, while ongoing investigations continue.
The Dutch data protection authority has received reports of data breaches from ten organizations connected to the incident. The full extent of the data stolen remains undisclosed, as Ceva has not provided information on the quantity of personal data compromised or any potential ransom demands from the hackers. Authorities in the Netherlands are currently probing the incident.
Written by urgent.news from TechCrunch's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.