One pasted Terminal command opens the door to Mac crypto wallet theft
Researchers have uncovered Mac malware that can steal credentials and drain all or a selected percentage of a cryptocurrency wallet, in yet another reminder not to paste random commands from the internet into Terminal. New malware via ClickFix The Go-based malware arrived through a ClickFix attack , which disguises a malicious instruction as a CAPTCHA or error message. Instead of exploiting macOS…
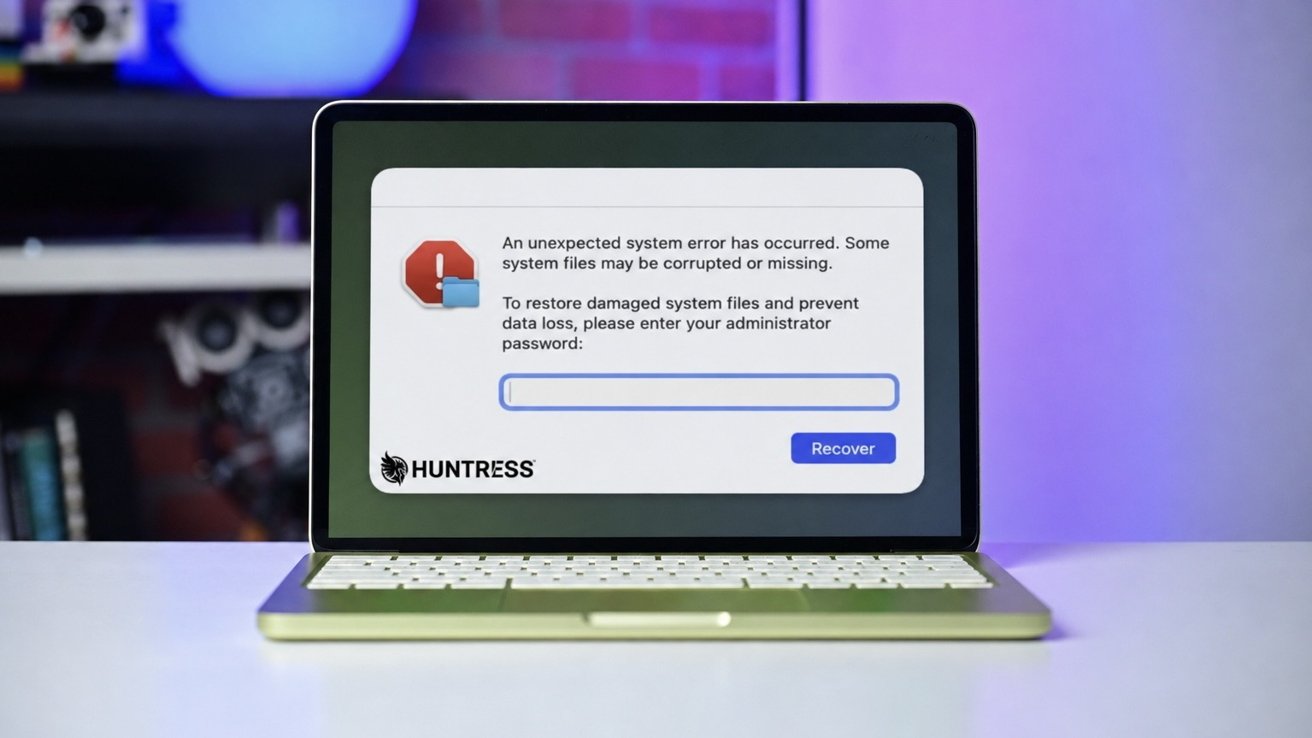
Researchers have discovered malicious Mac malware capable of stealing credentials and draining cryptocurrency wallets. The malware was distributed through a ClickFix attack, which presents a malicious command as a CAPTCHA or error message. Rather than exploiting macOS directly, the attackers tricked the victim into executing the command to install the malware.
Once activated, a Bash script identified the Mac and downloaded a payload tailored for either Apple Silicon or Intel hardware. Afterward, it erased its temporary file, wiped the Terminal screen, and eliminated the command from shell history. Huntress security analysts identified the infection during a post-incident review in June on a compromised Mac, which they reported on August 6.
Written by urgent.news from AppleInsider's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.