Paperclip AI Flaws Let Attackers Run Host Commands via Malicious Agent Imports
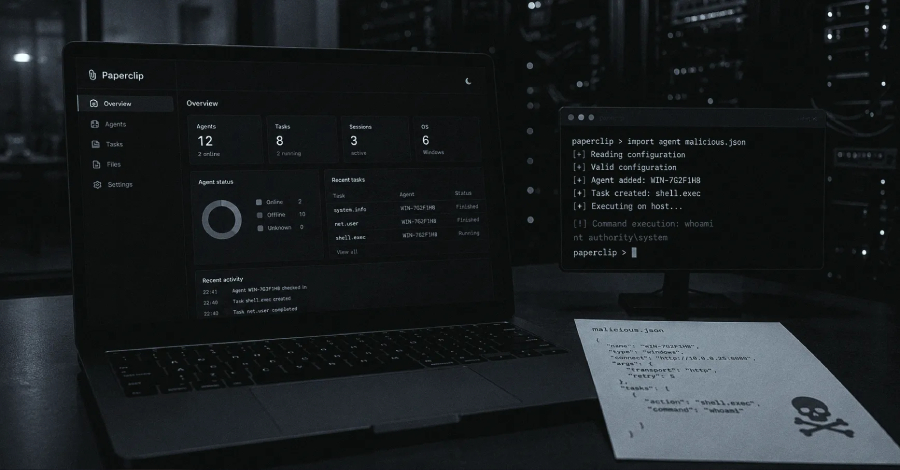
Two security flaws in Paperclip could let attackers execute commands on a network server or a developer's computer. Paperclip is an open-source control plane for teams of artificial intelligence (AI) agents, and both paths rely on importing a malicious agent and starting it. A third flaw could expose sensitive data and control-plane details through application programming interface (API) routes
We haven't written up this one. The Hacker News has the full story — the link below goes straight to it.