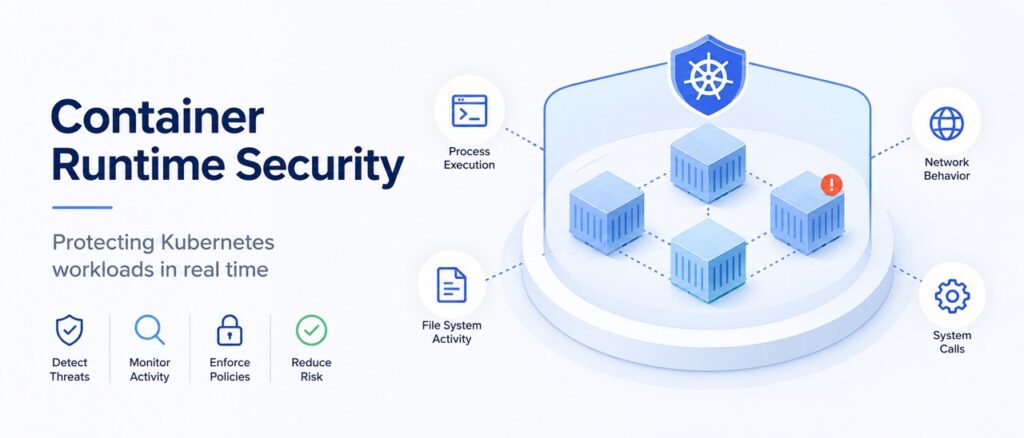
Container Runtime Security in Kubernetes: What Teams Overlook
Kubernetes security conversations tend to center on the things that happen on the left-hand side of the process. Scanning images, hardening Dockerfiles, and working with registry access controls all tend to frontload. This is necessary, but it leaves significant gaps once containerized workloads are running in production. Container adoption is The post Container Runtime Security in Kubernetes:…
We haven't written up this one. Container Journal has the full story — the link below goes straight to it.